Open Source Innovation - Empowering Telcos to Own Their Destiny
Explore how open source innovation empowers telecom companies to control their future and drive industry transformation through collaborative development and shared resources.
SMT Solvers in IT Security - Deobfuscating Binary Code with Logic
Explore SMT solvers for deobfuscating binary code in IT security. Learn practical applications, theoretical limitations, and solutions for enhancing malware analysis and vulnerability identification.
ManaTI: Web Assistance for Threat Analysis with Domain Similarity
Explore web-based threat analysis with ManaTI. Learn to use WHOIS similarity for domain classification, improving efficiency and accuracy in detecting network security threats.
Building a Software Security Program
Discover how to build a comprehensive Software Security Program addressing people, process, and technology challenges in software development, reducing risk and improving efficiency.
Introducing HAMISPA - High Availability MISP in AWS
Learn to deploy a highly available MISP (Malware Information Sharing Platform) in AWS for enhanced threat intelligence sharing and collaboration.
Find and Fix Software Security Problems - Preventing Security Mistakes
Explore effective strategies for identifying, fixing, and preventing software security issues. Learn how to prioritize and address vulnerabilities to enhance overall system security.
OWASP Security Knowledge Framework
Learn about the OWASP Security Knowledge Framework, its features, and how it can enhance your application security practices through this informative presentation by the project creators.
Only an Electron Away from Code Execution
Explore vulnerabilities in Electron-based applications and learn techniques for achieving code execution, presented by security researcher Silvia Väli at Hack.lu 2018.
Building with Privacy by Design
Explore privacy-by-design principles and their practical implementation in software development, enhancing user trust and data protection.
Building SLSA 3 Conformant Attestors for Artifacts Generated on GitHub
Learn to create SLSA 3 compliant attestors for GitHub artifacts, enhancing software supply chain security with minimal effort using recent framework extensions.
Improve Vulnerability Management with OCI Artifacts - It Is That Easy
Learn to enhance vulnerability management using OCI artifacts. Discover how to efficiently utilize SBOMs, signed attestations, and open-source tools for improved supply chain security at scale.
Automated Cloud-Native Incident Response with Kubernetes and Service Mesh
Explore automated incident response in cloud-native environments using Kubernetes and service mesh. Learn best practices, tools, and techniques for effective security management and threat mitigation.
DevSecOps Best Practices in Cloud Native Computing - CMCC Case Study
探索中国移动通信公司的DevSecOps最佳实践,了解如何将安全无缝集成到云原生开发和运维流程中,提高效率和安全性。
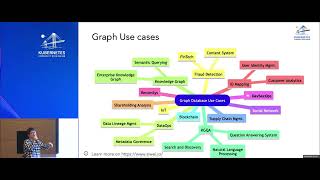
Graph Driven DevSecOps in Practice
Explore graph-driven DevSecOps implementation strategies, enhancing security integration in cloud-native development pipelines for improved efficiency and risk mitigation.
Trust No System: The Unsettling Reality of Zero Trust
Challenging "Zero Trust" in cloud-native security, this talk explores trust as an observer's decision, debunks myths, and offers strategies for managing trust in cloud environments.
What Can Go Wrong When You Trust Nobody? Threat Modeling Zero Trust
Explore Zero Trust principles and threat modeling for cloud-native systems. Learn to implement secure architectures using Istio, Kubernetes, SPIRE, and OPA for robust, distributed workload protection.
Evolution of On-Node Adaptive Power Tuning for Efficient Computing Systems
Explore adaptive power-tuning models using TuneD and Kubernetes Power Manager to optimize resource usage and reduce energy consumption in data centers.
Software Bill of Materials (SBOM) in Kubernetes - Best Practices and Approaches
Explore SBOM implementation in Kubernetes, comparing approaches and best practices. Learn how Paketo Buildpacks embeds SBOMs in application images using Syft, enhancing software supply chain security.
What Data Tells Us About Software Supply Chain Security and What To Do About It
Experts analyze data from surveys and reports on cloud-native and open source software security, providing actionable insights to improve software supply chain security for organizations and projects.
Putting Hackers Breaching Your Cluster in Automatic Quarantine
Explore automatic isolation techniques for breached apps in Kubernetes clusters, enhancing overall security and minimizing potential damage from hacker intrusions.
Building Stronger User Support Groups for Cloud Native Technologies
Brainstorming session on revitalizing user support groups post-COVID, exploring ideas for physical meetings, global Zoom groups, and CNCF support to enhance learning and sharing experiences in the cloud native community.