How to Spy with Python - Understanding PRISM and Cloud Security
Explore PRISM's impact on cloud services and learn strategies for securing data and preserving privacy in the cloud, with insights on leveraging cloud-based software while maintaining confidentiality.
OWASP Top 10 Mobile Risks: 2014 Reboot
Explore the updated 2014 OWASP Top 10 Mobile Risks, comparing changes since 2011, understanding new threats, and learning recommended fixes for iOS, Android, and Windows Phone platforms.
The Rise of SaaS-Targeted Malware - Zeus Variant Attacking Salesforce Users
Demonstration of a new Zeus malware variant targeting Salesforce users, showcasing its stealthy data exfiltration capabilities and discussing implications for SaaS security.
New Frameworks, Old Problems: Web Security Challenges in Modern Development
Exploring security challenges in modern web frameworks like Play! and Node.js, comparing solutions from established frameworks, and offering practical code examples to address common vulnerabilities.

Content Security Policy (CSP) - Understanding and Implementing Web Protection
Learn about Content Security Policy (CSP), a powerful browser security feature that mitigates cross-site scripting attacks. Discover its benefits, implementation strategies, and future impact on web security.
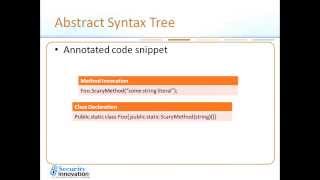
Adventures in Reviewing Mountains of Code
Explore strategies for efficiently reviewing large codebases, including experiments, tools, and unexpected challenges encountered during a 2.6 million line code assessment.
Seven Deadly Sins of Mobile Application Development - Unlocking Mobile Hacking Vulnerabilities
Unlock mobile app security secrets: Learn common development mistakes, session management vulnerabilities, and best practices to protect against attacks and impersonation.
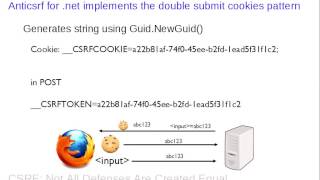
CSRF Defense Strategies - Not All Are Created Equal
Explore CSRF vulnerabilities, defense mechanisms, and their implementations. Learn about synchronizer token patterns, double submit cookies, and challenge-response systems for effective protection against CSRF attacks.
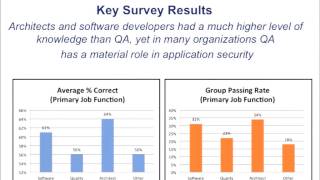
Can AppSec Training Really Make Developers Security-Smart?
Explore the effectiveness of AppSec training for developers through a year-long survey, revealing surprising insights on knowledge retention and practical application in software security programs.
Surviving an Application DoS - Strategies and Open Source Defense Framework
Explore strategies to defend against Application-Level DoS attacks using a new open-source Node.js framework. Learn to identify threats, analyze traffic patterns, and implement active defense measures.
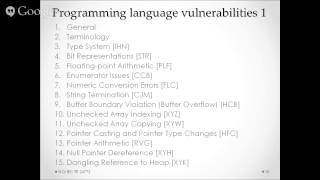
Guidance on Avoiding Programming Language Vulnerabilities - TR24772 Explanation
Overview of ISO/IEC TR 24772:2010, guiding programmers on avoiding vulnerabilities through language selection and use. Insights from a contributor on enhancing software security.
The Perilous Future of Browser Security
Explore browser security challenges, tradeoffs, and solutions. Learn about critical vulnerabilities, secure browser design, and balancing security with user experience in the face of evolving threats.
Can AppSec Training Really Make a Smarter Developer?
Explores the effectiveness of AppSec training for developers through a year-long survey, revealing surprising insights on knowledge retention and its impact on application security strategies.
NIST Missions and Impacts on US Industry, Economy, and Citizens - Lecture
Explore NIST's mission, impact on US industry, and cybersecurity initiatives. Learn about current programs, projects, and R&D activities in this premier scientific institution.
Pushing Content Security Policy to Production - Case Study of Real-World Implementation
Practical insights on implementing Content Security Policy in a live web application, covering challenges, browser nuances, third-party integrations, and real-world violation reports.
Fixing XSS with Content Security Policy
Learn how Content Security Policy (CSP) can prevent XSS attacks, understand its versions, browser support, and implementation strategies for web applications. Gain insights on balancing CSP with traditional security measures.
The European Commission's Upcoming Open Source Plans
Explore the European Commission's future strategies and initiatives for open source software, presented by a key representative from the organization.
Realtime Systems, RISC-V Vector Processing, Open Source in Europe, and Software Transparency - Keynotes Day 3
Explore cutting-edge topics in open source technology with expert keynotes on realtime systems, RISC-V processors, strategic challenges, and software transparency.
AGL Instrument Cluster Expert Group Discussion
Explore AGL Instrument Cluster Expert Group's insights on functional safety, architecture, and communication mechanisms for automotive software development.
Plan Your Learnings - Friendly User Testing for Automotive Software Updates
Explore friendly user testing for automotive software updates, balancing safety standards with innovation. Learn strategies for gathering user feedback and improving in-field performance.
Open Source in Safety Critical Applications
Explore the role of open source software in safety-critical systems with insights from Kate Stewart of The Linux Foundation.