OWASP Zap - Introduction and Usage Guide
Explore OWASP Zap's capabilities for web application security testing with David Scrobonia's comprehensive overview, highlighting key features and best practices for effective vulnerability detection.
Securing Single Page Applications - Design Considerations and Pitfalls
Explore security pitfalls in Single Page Applications and learn mitigation strategies. Covers stateless design, JSON handling, caching, local storage, and resource sharing, with practical demos and key takeaways.
Automated Gadget Chain Discovery for Deserialization Vulnerability Remediation
Explore automated discovery of Java deserialization gadget chains for vulnerability assessment and prioritized remediation, with insights on a new FOSS toolkit for evaluating security risks.
Threat Model-as-Code: Integrating Security into the Software Development Lifecycle
Integrating threat modeling into software development lifecycle using "Automaton" framework, enabling actionable outputs and automated security testing for improved product security.
Chromebooks and Network Motes: Enforcing Security Posture from Device to Cloud
Explore innovative security strategies using Chromebooks and network motes, balancing developer productivity with robust data protection in resource-constrained environments.
Empowering the Employee - Incident Response with a Security Bot
Explore how a Slack bot engages employees in incident response, enhancing security awareness and efficiency while providing valuable insights for quick, appropriate action.

Identity Theft: Attacks on SSO Systems
Explore vulnerabilities in SAML-based SSO systems, including XML signature attacks and user directory flaws. Learn how these issues can lead to identity theft and authentication bypasses in modern organizations.
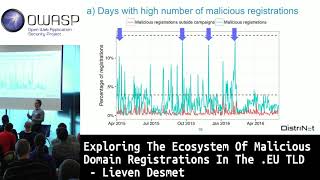
Exploring the Ecosystem of Malicious Domain Registrations in the .eu TLD
Extensive analysis of malicious domain registrations in .eu TLD, revealing cybercriminal tactics and campaign patterns. Insights into automated processes and operational aspects of large-scale malicious activities.
The Evil Friend in Your Browser - Browser Extension Security Risks
Explore the hidden dangers of browser extensions, their security model limitations, and potential risks to user privacy. Learn about real-world analysis findings and discuss improved security measures.
Monitoring Application Attack Surface and Integrating Security into DevOps Pipelines
Explore methods for calculating and tracking web application attack surface evolution, and learn to integrate security testing into CI/CD pipelines using metrics-based policies.
Embedding GDPR into the Software Development Lifecycle
Practical guide to integrating GDPR requirements into software development lifecycle, covering privacy awareness, risk analysis, secure coding, threat modeling, and breach notification processes.
Securing C Code That Seems to Work Fine
Explore strategies for securing C codebases in high-performance environments, balancing best practices with startup culture. Learn from real-world successes and failures in implementing application security controls.
Popular Approaches to Preventing Code Injection Attacks are Dangerously Wrong
Explores limitations of current code injection prevention methods and introduces Name Space Layout Randomization (NSLR) as a novel approach to secure Java applications against known and zero-day vulnerabilities.
Detecting CSRF Vulnerability Reliably - Programmatic Approach
Explore a programmatic approach to reliably detect CSRF vulnerabilities in web applications, overcoming common shortcomings of existing tools and improving automated security testing.
Remediating XSS in GitHub Open Source Projects - Lessons Learned
Insights on scaling XSS remediation across GitHub open source projects, focusing on risk reduction, adding security controls, and automating code modification for diverse applications.
Creating Accessible Security Testing with ZAP - AppSecCali 2019 Lightning Talk
Introducing OWASP ZAP's Heads Up Display: A new UI that makes security testing more intuitive for developers and professionals, enabling efficient use of the attack proxy tool.
Open-Source OWASP Tools for Enhancing Penetration Testing Coverage
Explore open-source OWASP tools for efficient white box penetration testing. Learn about Code Pulse for real-time code coverage and Attack Surface Detector for comprehensive endpoint discovery to enhance security assessments.
A Seat at the Table: Effective Security Collaboration in DevOps - AppSecCali 2019
Discover effective collaboration strategies for security professionals in the DevOps era, focusing on new skills, approaches, and speed to engage early and add value in software development.
Philanthropy and Democracy: Dangerous Liaisons
Explore the complex relationship between philanthropy and democracy, examining the benefits and potential threats of big philanthropy to democratic governance and societal progress.
Baking Security Into the Software Development Lifecycle - CISO Panel
CISOs discuss strategies for integrating security into rapid application development, sharing real-world experiences on managing evolving methodologies and pressures to publish securely.
Application Security for DevSecOps - Don't Learn, Don't See, Don't Run
Explore the future of DevSecOps with insights on seamless security integration, emerging technologies, and adoption strategies for the next three years in application development.