Tangled Web: Defense in Deception - 2017
Explore defensive deception strategies for web applications, including tools and techniques to detect, confuse, and corral attackers. Learn to plan, execute, and monitor effective deception in cybersecurity.
Why Has Your Toaster Been through More Security Testing than AI Systems
Exploring the lack of standardized security testing for AI systems in critical sectors, contrasting with rigorous certifications for everyday appliances and traditional software.
Implementing Differential Privacy for the 2020 US Census
Explore the implementation of differential privacy for the 2020 US Census, including technical challenges, organizational hurdles, and the development of innovative algorithms to protect respondent privacy.
Contact Tracing Apps - Engineering Privacy in Quicksand
Explore privacy challenges and solutions in contact tracing apps, focusing on end-to-end protection within complex ecosystems and overcoming obstacles in real-world implementation.
Stack Overflow: A Story of Two Security Tales - Enhancing Software Security
Exploring Stack Overflow's dual impact on software security: potential vulnerabilities and effective solutions. Highlights research findings and proposes design tweaks to enhance secure development practices.
Take Control of and Secure Your Passwords Using Vaultwarden on Portainer
Learn to set up and secure a self-hosted password manager using Vaultwarden on Portainer, covering installation, configuration, and integration with browsers for enhanced password security.
Hackersploit Talks Linux and Server Security - Craft of Code
Insightful discussion on cybersecurity, penetration testing, and Linux with Hackersploit, covering career insights, learning paths, and upcoming security content for tech enthusiasts.

The State of Memory Safety - Fireside Chat
Experts discuss memory safety vulnerabilities, their impact on modern computing, and strategies for protection. Explores current landscape, challenges, and progress in addressing this critical security issue.
Broken CAPTCHAs and Fractured Equity - Privacy and Security in hCaptcha's Accessibility Workflow
Exploring hCaptcha's accessibility workflow, its privacy implications, and security vulnerabilities. Discusses the future of CAPTCHAs and the challenge of balancing inclusivity with security in online verification systems.
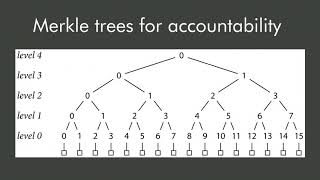
Securing the Software Supply Chain - Go Checksum Database
Exploring Go's checksum database design to secure software supply chains, addressing vulnerabilities in third-party dependencies and enhancing ecosystem integrity.
2019 OWASP Top 10 - Part 1
Comprehensive exploration of the first half of OWASP Top 10, covering critical web application security risks and effective mitigation strategies for developers and security professionals.
Security Instrumentation - The Future of Software Security
Explore security instrumentation as a revolutionary approach to enhance software security, offering dynamic capabilities like intrusion detection, SBOM reporting, and runtime protection without code changes.
Security Code Analysis is for Everyone - 2019
Learn proactive approaches to identify and fix software vulnerabilities using Security Code Analysis, addressing complex applications and diverse development environments.
Thwarting Intruders with Ever Morphing Infrastructure - 2019
Explore innovative cybersecurity strategies using dynamic infrastructure reshuffling to disrupt attack lifecycles and enhance network defense against intruders.
Living in AppSec - Promised, Fantasy, or Wonderland? - 2019
Explore GitHub's AppSec practices, successes, and ongoing challenges in creating an ideal security environment for application development.
Running FaaS with Scissors - DevSecOps and Serverless Security Testing - 2019
Explore DevSecOps and FaaS technologies to enhance secure code creation, utilizing OpenFaaS for faster, more consistent security assessments and continuous testing with quick feedback loops.
The DevSecOps Builder's Guide to the CI/CD Pipeline
Comprehensive guide to integrating security into DevOps practices, focusing on CI/CD pipeline implementation for enhanced software delivery and protection.
Bridging GDPR from Application to Cloud - 2018
Explore GDPR's impact on cloud services, DevOps, and SRE processes. Learn best practices for designing applications with built-in data protection to achieve GDPR compliance.
Securing Creative Content in the Digital Media Industry
Exploring modern security challenges in media, balancing content protection with user experience in a cloud-first era. Discusses innovative approaches to safeguard digital assets while fostering creativity.
StreamAlert: A Serverless Real-time Intrusion Detection Engine
Discover StreamAlert: a serverless, real-time intrusion detection engine that scales effortlessly, allowing security teams to focus on catching attackers with simple and complex rules for any log type.
How WhatsApp Reduced Spam While Launching End-to-End Encryption
Explore WhatsApp's innovative approach to reducing spam while implementing end-to-end encryption, featuring effective techniques and challenges faced in protecting user privacy and communication.