Readactor: Practical Code Randomization Resilient to Memory Disclosure
Explore practical code randomization techniques resilient to memory disclosure attacks, enhancing software security against return-oriented programming and other code-reuse threats.
Leave Me Alone - App-Level Protection against Runtime Information Gathering on Android
Explores app-level protection against runtime information gathering on Android, proposing App Guardian to pause suspicious background processes and thwart malicious monitoring attempts without system modifications.
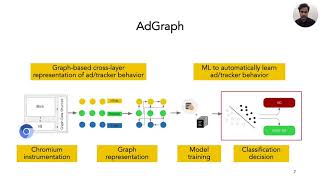
AdGraph: A Graph-Based Approach to Ad and Tracker Blocking
Innovative graph-based machine learning approach for detecting online ads and trackers, offering improved accuracy and performance compared to traditional filter list methods.
RetroWrite- Statically Instrumenting COTS Binaries for Fuzzing and Sanitization
Explore static instrumentation of COTS binaries for enhanced fuzzing and sanitization using RetroWrite, a framework for rewriting position-independent code.
Short Text, Large Effect - Measuring the Impact of User Reviews on Android App Security & Privacy
Exploring the impact of user reviews on Android app security and privacy, analyzing 4.5M reviews to identify concerns and measure developers' responses through code changes.
CaSym: Cache Aware Symbolic Execution for Side Channel Detection and Mitigation
Explores cache-aware symbolic execution for detecting and mitigating side-channel vulnerabilities, offering novel abstract cache models and guidance for effective countermeasures.
Iodine - Fast Dynamic Taint Tracking Using Rollback Free Optimistic Hybrid Analysis
Explores fast dynamic taint tracking using optimistic hybrid analysis, reducing overhead while maintaining soundness. Introduces Iodine tool for efficient security policy enforcement without rollbacks.
Understanding Linux Malware
Explore Linux malware analysis challenges, infrastructure design, and insights from a large-scale study of 10,548 samples, addressing the growing threat in embedded devices and IoT.
Revealer- Detecting and Exploiting Regular Expression Denial-of-Service Vulnerabilities
Explore techniques for detecting and exploiting ReDoS vulnerabilities, including static analysis, pattern identification, and automated exploit generation.
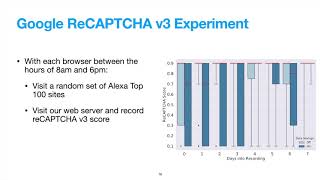
Meddling Middlemen - Empirical Analysis of the Risks of Data-Saving Mobile Browsers
Empirical analysis of data-saving mobile browsers, exploring their effectiveness, impact on usability, and potential security risks. Examines proxy server configurations, privacy concerns, and proposes improved designs.
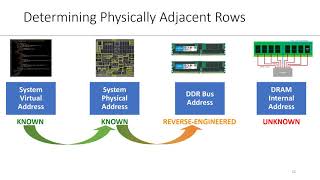
Are We Susceptible to Rowhammer? An End-to-End Methodology for Cloud Providers
Comprehensive methodology for cloud providers to assess DRAM vulnerability to Rowhammer attacks, including near-optimal instruction sequences and row adjacency mapping techniques for modern Intel platforms.
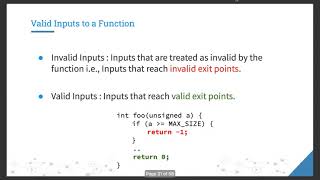
SPIDER - Enabling Fast Patch Propagation in Related Software Repositories
Explore fast patch propagation in software repositories, focusing on security patches, solution requirements, and implementation techniques for efficient and safe updates.
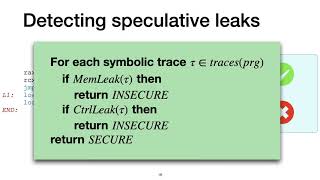
SPECTECTOR - Principled Detection of Speculative Information Flows
Principled detection of speculative information flows in computer systems, focusing on security against Spectre-like attacks through speculative non-interference and symbolic execution techniques.
Shining Light on Shadow Stacks
Comprehensive analysis of shadow stack mechanisms for protecting against control-flow hijacking attacks, evaluating performance, compatibility, and security. Proposes a novel design using a dedicated register.
Talos - Neutralizing Vulnerabilities with Security Workarounds for Rapid Response
Neutralizing vulnerabilities using error-handling code for rapid response, minimizing patch delays while maintaining functionality. Explores automated security workarounds to mitigate risks in popular Linux server applications.
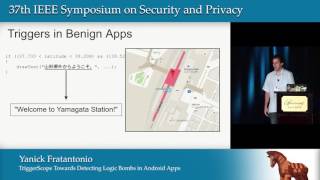
TriggerScope - Towards Detecting Logic Bombs in Android Applications
Explore techniques for detecting logic bombs in Android apps using symbolic execution and path predicate analysis. Learn about TriggerScope, a tool for identifying time-, location-, and SMS-related triggers in mobile applications.
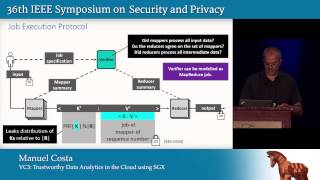
Trustworthy Data Analytics in the Cloud Using SGX
Explore trustworthy cloud-based data analytics using SGX technology. Learn about VC3, a system enabling secure MapReduce computations while preserving confidentiality and integrity of code and data.
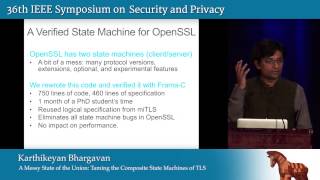
A Messy State of the Union - Taming the Composite State Machines of TLS
Explore critical security vulnerabilities in TLS implementations, including the FREAK flaw, and learn about a verified composite state machine for OpenSSL that addresses these issues.
Counterfeit Object-Oriented Programming
Explores counterfeit object-oriented programming, a novel code reuse attack technique in C++ applications, demonstrating its effectiveness against existing defenses and discussing potential prevention strategies.
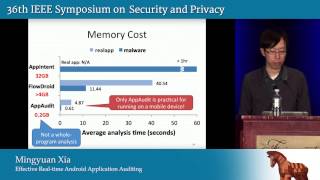
Effective Real-Time Android Application Auditing
Innovative approach combining static and dynamic analysis for efficient, real-time Android app auditing to detect data leaks, offering improved speed and accuracy over existing methods.
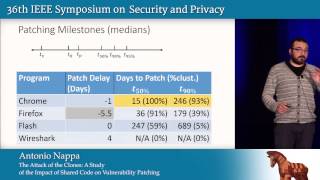
The Attack of the Clones - A Study of the Impact of Shared Code on Vulnerability Patching
Explores impact of shared code on vulnerability patching, revealing delays between patch releases and novel exploitation techniques. Analyzes patch deployment data from millions of hosts to improve cybersecurity strategies.