
Advanced ROP Framework - Pushing Return-Oriented Programming to Its Limits
Discover advanced return-oriented programming techniques with ROP ROCKET framework, featuring syscall bypassing, cross-architecture exploitation, and innovative bad byte handling for enhanced security testing.
Email Spoofing and Domain Impersonation Through Cloud Services
Dive into advanced email security exploitation techniques, learning how to bypass SPF & DMARC through Cloudflare partnerships and serverless applications for domain spoofing.
Automotive USB Fuzzing: Efficient Methods and Real-World Vulnerabilities
Dive into automotive USB fuzzing techniques and discover efficient methods for testing vehicle vulnerabilities through direct USB connections, featuring real-world case studies and practical demonstrations.
Bootsquad: Introduction to Secure Boot Exploitation and Defense
Dive into the world of cybersecurity and virtual reality as Joe Mast presents Bootsquad, exploring innovative security concepts and challenges in the DCGVR Village at DEF CON 31.
Taking Down Applications with Logic - DEF CON 31
Dive into advanced application security techniques and learn how logical vulnerabilities can be exploited to compromise web applications, demonstrated through real-world examples.
Grand Theft Actions - Abusing Self-Hosted GitHub Runners for Supply Chain Attacks
Dive into critical security vulnerabilities in GitHub Actions, exploring real-world attacks on self-hosted runners and learning how to prevent supply chain compromises in major open-source projects.
Finding and Exploiting Local Security Vulnerabilities in 1Password for MacOS
Explore critical security vulnerabilities in 1Password's MacOS app, including local vault exploitation, IPC weaknesses, and Chrome extension flaws that could compromise password security.
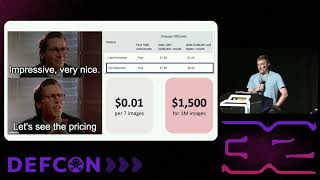
Secret Life of Rogue Devices: Lost IT Assets on the Public Marketplace
Uncover the alarming journey of lost corporate devices in public markets through data scraping, OCR clusters, reverse engineering, and conversations with underground collectors.
The XZ Backdoor Story: How a Supply Chain Attack Nearly Compromised SSH Servers
Uncover the gripping investigation of the XZ backdoor incident, exploring the mysterious maintainer Jia Tan, technical analysis of the compromise, and crucial lessons for open-source security.
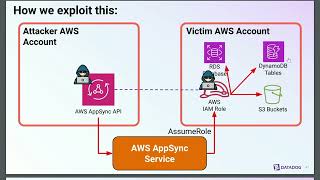
Exploiting Cloud Provider Vulnerabilities for Initial Access in AWS
Dive into advanced AWS security vulnerabilities, focusing on IAM role exploitation, confused deputy attacks, and critical misconfigurations that enable unauthorized cloud environment access.
Early Microprocessors and the 6502: A Historical and Technical Introduction
Explore the fascinating history of early microprocessors, focusing on the 6502 chip, its programming, and impact on vintage computing systems, with hands-on demonstrations and resources.
AWS CloudQuarry: Digging for Secrets in Public AMIs
Dive into AWS security vulnerabilities through an analysis of 3.1M AMIs, exploring credential exposure risks, detection methodologies, and essential cloud security practices for preventing breaches.
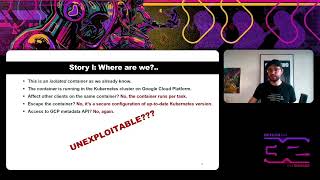
Exploiting the Unexploitable - Advanced JavaScript Vulnerability Chains in Kibana
Dive into advanced exploitation techniques for JavaScript vulnerabilities, focusing on Prototype Pollution attacks and RCE chains through real-world Kibana Bug Bounty examples and defense strategies.
Transforming Application Security: Protecting Everything as Code
Explore modern application security challenges and solutions in cloud-native environments, from threat modeling to real-time detection, with emphasis on securing 'everything as code' ecosystems.
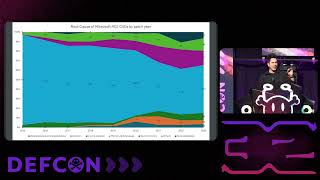
The Rise and Fall of Binary Exploitation - A Technical Analysis of Memory Safety and Exploit Mitigations
Explore the evolution of binary exploitation, memory safety challenges, and modern protection mechanisms in operating systems, focusing on Windows security mitigations and their effectiveness.
Creating Custom Electronic Conference Badges - A Guide to OpenTaxus Design
Learn to design and customize electronic conference badges using OpenTaxus - from hardware modifications in KiCAD to software changes in CircuitPython, plus cost management and production logistics.
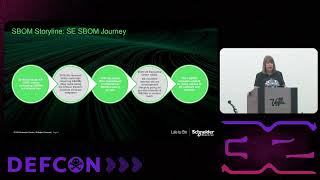
The Missing Link: How to Collect and Leverage Software Bill of Materials (SBOMs)
Discover how Schneider Electric efficiently manages software security through SBOM collection and implementation, with real-world examples from Log4j and OpenSSL vulnerability responses.
Hacking Apple's USB-C Controller: From JTAG Access to Code Execution on iPhone 15
Dive into advanced hardware hacking techniques to exploit Apple's ACE3 USB-C controller, using reverse engineering, side-channel analysis, and fault injection to gain code execution access on iPhone 15.
Inside Llama 3 Red Team Process - AI Safety and Security Assessment
Delve into Meta's AI Red Team's comprehensive approach to testing Llama 3's safety, exploring methodologies, automated attacks, and emerging security challenges in AI systems.
Practical Exploitation of DoS in Bug Bounty Programs
Discover practical techniques for identifying and exploiting DoS vulnerabilities in bug bounty programs, covering N+1 errors, GraphQL crashing, and Cache Poisoning with real-world examples and responsible reporting practices.
Splitting the Email Atom: Exploiting Parsers to Bypass Access Controls
Discover techniques for exploiting email address parsing vulnerabilities to bypass security controls, spoof domains, and access protected systems through RFC-compliant manipulation.