Tackling Dreaded .Net Cold Starts When Going Serverless
Explore solutions to overcome .NET cold starts in serverless architectures, understanding the underlying issues and implementing effective strategies to enhance performance and relevance.
Access All Areas - Making Accessibility More Accessible
Explore strategies for making digital content universally accessible, addressing challenges in converting existing documents and discussing future automation possibilities using AI.
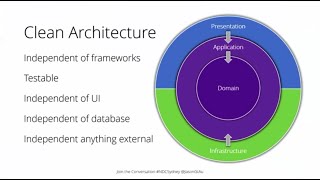
Clean Architecture with ASP.NET Core 3.0
Practical guidance on building scalable, maintainable ASP.NET Core 3.0 applications using Clean Architecture principles. Covers project organization, design strategies, and best practices for enterprise development.
Blazor in More Depth
Explore advanced Blazor features with its architects, including server-side streaming, WebAssembly authorization, and internal workings. Informal, interactive session welcoming audience questions and demo requests.
Measuring DevSecOps - Building Metrics to Understand Effectiveness and Success
Explore essential DevSecOps KPIs, learn to track and visualize security metrics, and gain insights to improve your team's effectiveness using Azure DevOps and supportive tools.
Why Don't Users Do What They are Supposed to Do? A Look at Users and Security
Exploring user behavior in cybersecurity through HCI design. Investigates why users ignore threats and how developers can improve security tools by understanding user perspectives.
The Future of AppSec is Cloud-Native
Explore cloud-native technologies' impact on application security, transforming DevSecOps from blocker to enabler. Learn tools and processes for enhanced visibility, vulnerability discovery, and feedback loops.
Modern Web Vulnerabilities 2020
Explore modern web vulnerabilities, including insecure deserialization, SSRF, ESI injection, prototype pollution, and HTTP request smuggling, with demos and prevention strategies.
Implementing OpenID Connect and OAuth 2.0 – Tips from the Trenches
Architectural patterns for identity & access control using OpenID Connect and OAuth 2.0, addressing common challenges in token-based systems for modern applications.

SignalR Deep Dive - Building Servers
Explore building SignalR servers beyond .NET, gaining insights into its inner workings and potential extensions for various programming languages and platforms.
Make Your Custom .NET GC - Whys and Hows
Explore the Local GC feature in .NET Core 2.1, enabling custom garbage collection implementation or using default GC outside .NET. Learn the process, benefits, and challenges of creating your own GC.
The OWASP Top Ten Proactive Controls 2018
Explore critical security techniques for web application development, including secure coding practices, data protection, and access control, as outlined in the OWASP Top Ten Proactive Controls 2018.
Rip It Up And Start Again
Explore how organizational structures and team responsibilities impact microservice architecture success, focusing on modern autonomous delivery teams and key concepts like Conway's law and Dunbar's number.

Blazor - A New Framework for Browser-Based .NET Apps
Explore Blazor WebAssembly for building interactive client-side apps using C# and Razor. Learn component-based architecture, API access, testing, deployment, and offline support.
Securing Serverless Applications in Azure
Learn to secure serverless apps in Azure using Key Vault, ClaimsPrincipal binding, and other techniques to enhance developer productivity while maintaining robust security measures.

How to Use the Roboflow Upload API - Python
Learn to programmatically add images and annotations to datasets using Roboflow's Upload API, enabling active learning and continuous improvement of computer vision models.
Sentence Similarity With Transformers and PyTorch
Learn to measure semantic similarity between sentences using BERT and PyTorch. Explore tokenization, vector creation, and cosine similarity calculation for powerful NLP applications.
Identify Stocks on Reddit with SpaCy - NER in Python
Learn to extract stock mentions from Reddit using SpaCy's Named Entity Recognition, enabling automated classification and analysis of unstructured text data for financial insights.
Table Question-Answering with TAPAS in Python
Learn to implement table question-answering using TAPAS in Python, covering retrieval pipelines, dataset preprocessing, and advanced aggregation queries with Hugging Face transformers and Pinecone vector database.
Hugging Face Datasets - Dataset Builder Scripts for Beginners
Learn to create and manage dataset builder scripts for Hugging Face, including download management, Apache Arrow datatypes, and integration with popular machine learning frameworks for efficient model training and fine-tuning.
Box Logo Tutorial - 3D Animation in After Effects
Learn to create dynamic 3D box logos in After Effects with advanced techniques for lighting, animation, and interactive controls.