STRC - The Security Training and Research Cloud
Explore cloud-based cybersecurity training and research with STRC, covering defense, networking, data centers, automation, and practical labs for skill development.
Assessing Mobile Applications with the MobiSec Live Environment
Explore mobile app security assessment using MobiSec Live Environment, covering tools and techniques for identifying vulnerabilities in iOS and Android applications.
Can Cloud and Security Be Used in the Same Sentence
Explore cloud security concerns, best practices, and benefits in enterprise environments. Learn about encryption, two-factor authentication, and DevOps approaches for improved security and efficiency.
Character Assassination Fun and Games with Unicode - Adrian Crenshaw
Explore Unicode's potential for character obfuscation, homograph attacks, and steganography in cybersecurity. Learn about encoding, browser protections, and real-world implications.
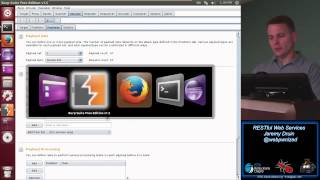
RESTful Web Services
Learn to secure RESTful web services by exploring test methods, authentication, responses, and common vulnerabilities. Gain practical insights for robust API protection.
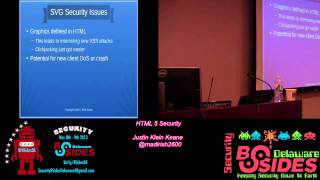
HTML 5 Security
Explore HTML5 security vulnerabilities and best practices with Justin Klein Keane. Learn about emerging threats and defensive strategies for modern web applications.
Cloud Business and Academia - Bringing It All Together - Cloud Security Alliance Delaware
Explore the intersection of cloud technology, business, and academia with insights from the Cloud Security Alliance Delaware chapter.
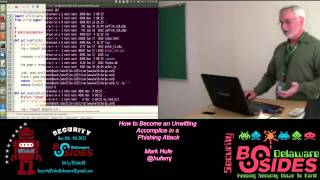
How to Become an Unwitting Accomplice in a Phishing Attack
Explore phishing attack techniques, consequences, and prevention strategies through real-world examples and forensic analysis. Learn to identify vulnerabilities and protect against unwitting involvement in cybercrime.
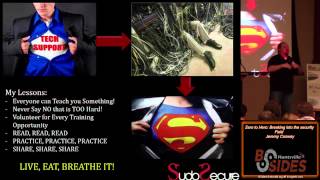
Zero to Hero - Breaking into the Security Field
Practical advice for breaking into the cybersecurity field, covering education, certifications, networking, and personal development strategies for aspiring professionals.
HTTPS Now You See Me
Explore HTTPS encryption, its vulnerabilities, and methods to intercept secure communications in this informative cybersecurity presentation.
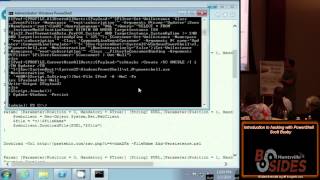
Introduction to Hacking with PowerShell
Learn to leverage PowerShell for ethical hacking and penetration testing, exploring its powerful scripting capabilities for security professionals and system administrators.
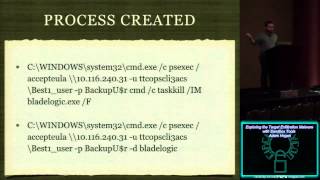
Exploring the Target Exfiltration Malware with Sandbox Tools
Explore target exfiltration malware using sandbox tools. Learn static and dynamic analysis techniques, process management, and considerations for effective malware detection and security automation.
Gitdigger - Creating Useful Wordlists and Hashes from GitHub Repositories
Learn to extract valuable data from GitHub repositories using GitDigger, creating wordlists and hashes for security testing and analysis.
OWASP Top 10 of 2013 - It's Still a Thing and We're Still Not Getting It
Explore OWASP Top 10 vulnerabilities from 2013, their ongoing relevance, and why organizations struggle to address them effectively in web application security.
Lockade Electronic Games for Locksport
Explore electronic lockpicking games for locksport enthusiasts, enhancing skills and understanding of lock mechanisms through interactive digital simulations.
Burp for All Languages
Learn to leverage Burp Suite for web application security testing across various programming languages with expert insights and practical techniques.
Exploiting Browsers Like A Boss
Learn advanced browser exploitation techniques and strategies for identifying vulnerabilities in web applications from cybersecurity expert Bryce Kunz.
NoSQL Injections - Moving Beyond or 11
Explore advanced NoSQL injection techniques and defense strategies with expert Matt Bromiley, moving beyond basic vulnerabilities to enhance database security.
Shellcode Time - Come on Grab Your Friends - Wartortell
Explore shellcode creation techniques, from assembly basics to advanced concepts like modular payloads and JSON objects, enhancing your understanding of low-level programming and security.
More New Shiny in the Metasploit Framework
Explore new Metasploit Framework features including enhanced credential handling, browser exploit improvements, and post-exploitation tools for Firefox and Android. Learn about infrastructure updates and future development plans.
Step On In The Waters Fine - An Introduction to Security Testing Within a Virtualized Environment
Explore virtualized security testing with hands-on guidance, from hardware setup to offensive VMs. Learn essential skills for self-taught hackers and aspiring cybersecurity professionals.