How to Take Over a Production System in the Cloud
Explore real-world cloud security vulnerabilities, their root causes, and effective mitigation strategies through examples and demonstrations. Learn to protect your cloud systems from potential threats.
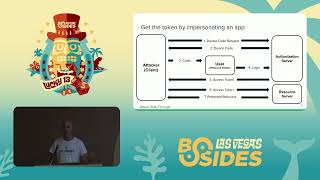
Oauth Third Party Not Departing
Explore OAuth vulnerabilities and security risks in third-party integrations, focusing on potential exploits and mitigation strategies for robust authentication systems.
SBOM is Here - Making Progress - Not Excuses
Explore the progress and implementation of Software Bill of Materials (SBOM) in cybersecurity, discussing challenges, opportunities, and practical strategies for effective adoption and utilization.
Making Your Website Vulnerable for Fun and Security Awareness
Learn to intentionally create website vulnerabilities for security awareness and testing, enhancing your understanding of web application security risks and defenses.
Orada Bir Gök Var Uzakta
Doğa temelli bilim eğitiminin önemi ve Usturlab Atölye'nin çocuklar için yürüttüğü yenilikçi eğitim programları hakkında ilham verici bir konuşma.
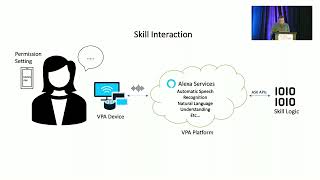
SkillDetective - Automated Policy-Violation Detection of Voice Assistant Applications in the Wild
Automated tool for detecting policy violations in voice assistant apps, analyzing 54,055 Alexa skills and 5,583 Google actions, identifying over 6,000 violations across 52 policy requirements.
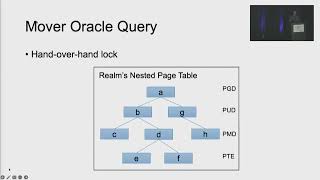
Design and Verification of the Arm Confidential Compute Architecture
Explores Realms, a new confidential computing abstraction protecting data privacy in virtual machines. Introduces novel verification techniques for secure firmware in complex, concurrent systems.
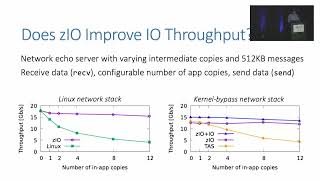
zIO - Accelerating IO-Intensive Applications with Transparent Zero-Copy IO
Explore zIO, a transparent zero-copy IO mechanism that enhances performance of IO-intensive applications by eliminating unnecessary data copies and optimizing data consistency management.
Justitia - Software Multi-Tenancy in Hardware Kernel-Bypass Networks
Explore software multi-tenancy in hardware kernel-bypass networks, addressing challenges in network sharing policies while preserving low latency and CPU efficiency in modern datacenters.
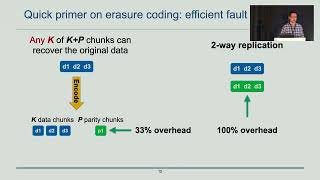
C2DN - How to Harness Erasure Codes at the Edge for Efficient Content Delivery
Explore innovative CDN design using erasure coding for improved performance, efficiency, and load balancing in content delivery networks.
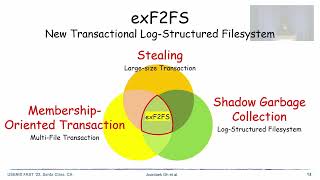
ExF2FS - Transaction Support in Log-Structured Filesystem
Innovative log-structured filesystem with transaction support, enhancing multi-file operations and garbage collection for improved performance in database systems and software installations.
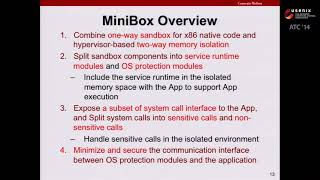
MiniBox - A Two-Way Sandbox for x86 Native Code
Explore MiniBox, a groundbreaking two-way sandbox for x86 native code, offering mutual protection between applications and operating systems in cloud computing environments.
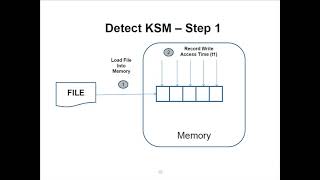
Hyperprobe - Towards Virtual Machine Extrospection
Explores a novel framework for detecting host OS kernel versions from within guest operating systems, leveraging hypervisor features and bugs to enable virtual machine extrospection.
Grand National 2021 - Managing Extreme Online Demand at William Hill
Strategies for managing unprecedented online demand during a major sporting event, focusing on SRE preparation, lambda@edge logic, and queueing systems to handle traffic spikes.
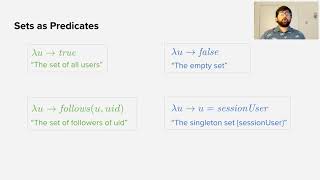
STORM - Refinement Types for Secure Web Applications
STORM: A web framework for building MVC applications with compile-time enforcement of security policies, reducing trusted code to under 1% and providing static security enforcement with minimal overhead.
The Rise of the Citizen Developer - Assessing the Security Impact of Online App Generators
Assessing security risks of online app generators for citizen developers, revealing vulnerabilities in generated apps and their impact on the mobile ecosystem's overall health.
T-Fuzz - Fuzzing by Program Transformation
Innovative fuzzing technique that removes input checks to explore deeper code paths, improving bug discovery in software. Combines program transformation with symbolic execution for effective results.
Angora - Efficient Fuzzing by Principled Search
Innovative fuzzing technique combining mutation-based speed with high-quality input generation, outperforming existing fuzzers in bug detection and branch coverage through advanced constraint-solving methods.
Hackers vs. Testers - A Comparison of Software Vulnerability Discovery Processes
Explore the processes, skills, and challenges of software testers and white-hat hackers in identifying security vulnerabilities, based on a comparative study of 25 professionals.
A Machine Learning Approach to Prevent Malicious Calls Over Telephony Networks
Innovative machine learning solution to combat telephony spam and scams, using user-tagged call logs to design effective features for predicting and blocking malicious calls with high accuracy.
How the BIOS Assures Its Handling of Inputs
Explore BIOS input handling, firmware interfaces, and analysis techniques for formal validation and vulnerability detection, including static, dynamic, and symbolic execution approaches.