Inside Out - The Cloud Has Never Been So Close
Explore a novel graph-based approach to cloud infrastructure attacks, revealing vulnerabilities in resource relationships and demonstrating potential privilege escalation techniques.
New Exploit Technique in Java Deserialization Attack
Unveiling advanced Java deserialization vulnerabilities: analysis of 10,000+ libraries, new exploit techniques, and their profound impact on Java security. Enhances attack vectors beyond deserialization.

Fuzzing and Exploiting Virtual Channels in Microsoft Remote Desktop Protocol for Fun and Profit
Explore coverage-based fuzzing of RDP client virtual channels, targeting complex functionalities like Sound, Graphics, USB, and Filesystem to uncover potential vulnerabilities and crashes.
Chain of Fools - An Exploration of Certificate Chain Validation Mishaps
Explore implications of poor cryptographic API design, insecure certificate chain validation, and widespread usage of APIs like Android SafetyNet. Recommendations for implementers and API authors are proposed.
Shifting Knowledge Left - Keeping up with Modern Application Security
Explore modern application security challenges in DevSecOps, including evolving web technologies, persistent vulnerabilities, and emerging framework defenses against common threats.
Automation Techniques in C++ Reverse Engineering
Explore dynamic analysis techniques for C++ reverse engineering, focusing on structure usage and function argument types through DLL injection-based automation.
Discovering Hidden Properties to Attack the Node.js Ecosystem
Novel attack method against Node.js platform using hidden property abusing. Explores vulnerabilities in JavaScript data exchange to tamper with critical program states in server-side applications.
iOS Kernel PAC, One Year Later
Análisis de la evolución y vulnerabilidades de la autenticación de punteros del kernel de iOS, con demostraciones de nuevos métodos para eludir la seguridad en iOS 13.3.
Detecting Fake 4G Base Stations in Real Time
Learn to detect and understand 4G/LTE IMSI-catchers, explore their capabilities, and discover software solutions for identifying fake base stations. Gain insights into cell network security improvements.
Demigod - The Art of Emulating Kernel Rootkits
Explore advanced techniques for emulating and analyzing kernel rootkits, enhancing cybersecurity defenses against high-privilege malware operating at the OS level.
Heroku Abuse Operations - Hunting Wolves in Sheep's Clothing
Explore techniques for detecting and responding to malicious activity disguised as legitimate use in cloud platforms. Learn to identify and mitigate abuse scenarios that bypass traditional security measures.
FASTCash and INJX_Pure - How Threat Actors Use Public Standards for Financial Fraud
Explore how cybercriminals exploit public standards to conduct ATM fraud through INJX_Pure and Lazarus FASTCash malware, showcasing their programming skills and understanding of financial transactions.
Whispers Among the Stars - A Practical Look at Perpetrating Satellite Eavesdropping Attacks
Experimental exploration of satellite broadband vulnerabilities using affordable equipment. Demonstrates eavesdropping techniques across land, air, and sea communications with minimal detection risk.
OAuth vs. SAML vs. OpenID Connect
Explore key identity federation protocols: OAuth, SAML, and OpenID Connect. Compare features, security levels, and use cases to make informed decisions for your application's single sign-on implementation.
Don't Touch Me That Way
Explore iOS fingerprint API security: correct usage, vulnerabilities, and potential attacks. Hands-on demo with code, tools, and test applications for mobile app developers and security professionals.
It's 10pm, Do You Know Where Your Access Keys Are?
Strengthen AWS infrastructure against attacks: Learn to secure environments, monitor for threats, and recover from incidents using AWS tools like Config, CloudWatch, and IAM.
LangSec for the Masses
Explore AWS security best practices, including hardening, monitoring, and recovery techniques. Learn to protect your infrastructure against common attacks and respond to security breaches effectively.
Be Ready for BeyondCorp - Enterprise Identity, Perimeters and Your Application
Explore BeyondCorp's enterprise security model, focusing on user and device authentication, access control, and implementation in open-source web applications using tools like SAML and Django.
Could a Few Lines of Code Mess It All Up
Explores risks of open source dependencies, revealing potential vulnerabilities in popular packages and discussing impacts on app security. Offers insights on mitigating risks in hybrid development.
IOT and AppSec
Explore the intersection of Internet of Things (IoT) and application security, examining potential vulnerabilities and strategies for safeguarding connected devices and systems.
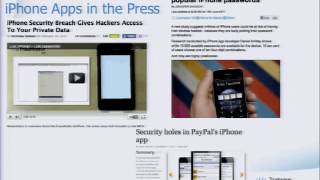
Hacking and Defending iPhone Application
Explore iPhone app vulnerabilities and defense strategies through hands-on demonstrations and practical techniques for securing iOS applications.