Web Timing Attacks Made Practical
Explore practical web timing attacks, improving data collection and statistical analysis for more effective penetration testing. Learn adaptive techniques and open-source tools for identifying cryptographic vulnerabilities.
Faux Disk Encryption - Realities of Secure Storage on Mobile Devices
Explore mobile device data security challenges, debunk full-disk encryption myths, and learn sophisticated secure storage techniques for iOS and Android, addressing real-world application vulnerabilities.
Internet-Scale File Analysis
Explore TOTEM and DRAKVUF systems for large-scale malware analysis, addressing challenges in file diversity, volume, and dynamic analysis through cloud-based orchestration and hardware virtualization.
Lessons Learned from Eight Years of Breaking Hypervisors
Explore vulnerabilities in popular hypervisors, examining security features, attack surfaces, and design flaws. Gain insights on improving hypervisor security through real-world examples and expert recommendations.
Blended Web and Database Attacks on Real-Time, In-Memory Platforms
Explore innovative attack vectors on real-time, in-memory platforms, blending web and database vulnerabilities. Learn about new SQL injection techniques, server-side JavaScript exploits, and R-based attacks in SAP HANA.
Firmware.RE - Firmware Unpacking, Analysis and Vulnerability-Discovery as a Service
Large-scale analysis of firmware images reveals vulnerabilities across embedded systems, highlighting security challenges and the need for improved tools and techniques in firmware analysis.
PDF Attack - A Journey from the Exploit Kit to the Shellcode
Explore PDF-based attacks, from exploit kits to shellcode analysis. Learn to extract and analyze obfuscated JavaScript, modify malicious PDFs, and understand cybercriminal techniques using peepdf tool.
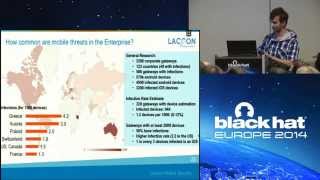
A Practical Attack Against VDI Solutions
Demonstration of a proof-of-concept attack exploiting screen scraping to bypass VDI security measures, highlighting vulnerabilities in secure BYOD solutions.
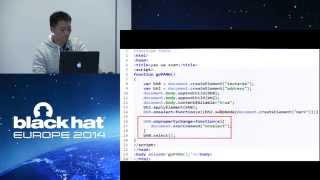
The Power of Pair - One Template that Reveals 100+ UAF IE Vulnerabilities
Discover a unique fuzzing strategy that revealed over 100 IE use-after-free vulnerabilities. Learn about the vulnerability hunting system and techniques used to find critical browser security flaws.
How to Find Bugs in USB Device Drivers
Explore USB device driver vulnerabilities using vUSBf framework. Learn about fuzzing techniques, bug detection, and potential security risks in USB implementations across various operating systems.
Man in the Binder - He Who Controls IPC, Controls the Droid
Explore Android's Binder IPC system, its security implications, and potential vulnerabilities through a POC rootkit demonstration and in-depth analysis of low-level Binder operations.
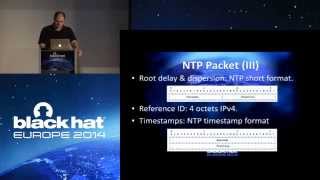
Bypassing HTTP Strict Transport Security
Explore vulnerabilities in HTTP Strict Transport Security (HSTS) and learn how attackers can exploit inter-operation weaknesses to bypass this protection and launch SSLStrip attacks.
OpenStack Cloud at Yahoo Scale - How to Avoid Disaster
Learn strategies to secure large-scale OpenStack deployments, including hardening techniques, compromise mitigation, and network architecture considerations, based on Yahoo's experience managing massive cloud infrastructure.
Next Generation Disassembly Framework
Explore next-gen disassembly framework for multi-architecture binary analysis. Learn about Capstone engine's features, design challenges, and potential applications in reversing, exploit development, and malware detection.
The Node.js Highway - Attacks Are At Full Throttle
Explore Node.js security issues and effective measures for secure application development. Learn about weak cryptography, testing, MongoDB, and see a practical demo.

Stagefright - Scary Code in the Heart of Android
Exploring Android's Stagefright framework vulnerabilities, focusing on discovery techniques, OS internals, and security implications. Demonstrates proof-of-concept code and discusses mitigation strategies.
Bringing a Machete to the Amazon
Explore AWS security challenges, vulnerabilities, and solutions. Learn assessment techniques and tools to protect your cloud infrastructure and applications.
C++11 Metaprogramming Applied to Software Obfuscation
Explore advanced C++11 metaprogramming techniques for software obfuscation, including compile-time code generation, polymorphism, and practical applications like string encryption and call obfuscation.
Scala Security - Examining the Play and LiftWeb Frameworks
Explore security aspects of Scala's Play and LiftWeb frameworks, including OWASP Top 10 vulnerabilities, exploitation mitigations, and a new Scala library for SSRF prevention.
Attacking the Linux PRNG on Android
Explore vulnerabilities in Android's Linux PRNG, focusing on early boot attacks and real-world exploitation vectors. Learn about potential security risks and mitigations for embedded platforms.
Freeze Drying for Capturing Environment-Sensitive Malware Alive
Innovative techniques for capturing and analyzing environment-sensitive malware through "freeze drying" and live process migration, enabling dynamic analysis of sophisticated threats like Citadel and ZeuS/GameOver.