Attacking and Defending the Microsoft Cloud - Office 365 & Azure AD
Explore common attacks on Microsoft Cloud, learn effective defenses, and gain insights into securing Office 365 and Azure AD environments. Applicable to other cloud providers.
Over-the-Air - How We Remotely Compromised the Gateway, BCM, and Autopilot ECUs of Tesla Cars
Detailing Tesla car hacking techniques, including remote compromises of gateway, BCM, and Autopilot ECUs. Explores vulnerabilities, attack chains, and Tesla's security enhancements in response.
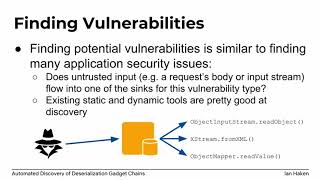
Automated Discovery of Deserialization Gadget Chains
Explore automated discovery of deserialization gadget chains, understanding vulnerabilities, and learning techniques to find and mitigate exploits in Java libraries and applications.
ZEROing Trust - Do Zero Trust Approaches Deliver Real Security?
Analyze effectiveness of zero trust security across modern OS platforms, examining measurable properties to establish trust in various threat scenarios.
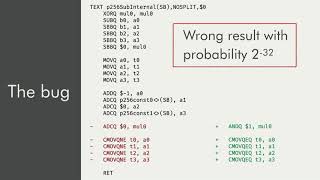
Squeezing a Key through a Carry Bit
Explore a practical key recovery attack on Go's P-256 elliptic curve implementation, targeting JSON Web Encryption through a subtle carry bit bug.
Two-Factor Authentication, Usable or Not? - A Two-Phase Usability Study of the FIDO U2F Security Key
Explore the usability of FIDO U2F Security Keys for two-factor authentication through a comprehensive two-phase study, evaluating effectiveness and user experience.
The Cost of Complexity - Different Vulnerabilities While Implementing the Same RFC
Exploring security vulnerabilities in DNS implementations due to complexity and ambiguity in RFC 1035, focusing on message compression and its impact on TCP/IP stacks.
Hunting Vulnerabilities of gRPC Protocol Armed Mobile - IoT Applications
Explore security vulnerabilities in gRPC-powered mobile and IoT apps. Learn about common pitfalls, attack vectors, and strategies to enhance protection in this high-performance protocol.
Racing the Dark - A New TOCTTOU Story From Apple's Core
Unveils macOS kernel vulnerabilities, highlighting memory mapping issues and race conditions that bypass security updates. Emphasizes the need to reevaluate macOS/iOS memory mapping mechanisms.
The Tangled Webview - Javascriptinterface Once More
Unveils new Android WebView vulnerabilities related to JavascriptInterface, bypassing all verifications. Presents a novel attack model and discusses security implications for mobile app developers.
Analyzing and Fuzzing for Qualcomm Hexagon Processor
Explore techniques for analyzing and fuzzing Qualcomm Hexagon processors, overcoming challenges in firmware analysis, emulation, and hardware-dependent targets for enhanced security research.
In-Field Emulation and Fuzzing of PLCs to Uncover the Next Zero-Day Threat in Industrial Control Systems
Explore innovative techniques for uncovering vulnerabilities in Industrial Control Systems through in-field emulation and fuzzing of PLCs, focusing on proactive security measures beyond network-level exploits.
FPs Are Cheap - Show Me the CVEs
Evaluating SAST tools: Learn how to assess their effectiveness in finding real vulnerabilities using synthetic test suites and practical examples of CVEs.
Design Pitfalls in Commercial Mini-Programs on Android and iOS
Explore security vulnerabilities in app-in-app paradigms for Android and iOS, focusing on mini-programs' design flaws and potential risks to user privacy and data protection.
Attacking and Defending Machine Learning Applications of Public Cloud
Explore techniques for attacking and defending machine learning applications in public cloud environments, focusing on visual classification vulnerabilities and countermeasures.
Identifying Multi-Binary Vulnerabilities in Embedded Firmware at Scale
Explore techniques for identifying vulnerabilities in embedded firmware, focusing on multi-binary analysis, dynamic and static approaches, and scalable solutions for IoT device security.
Cutting Edge - Microsoft Browser Security — From People Who Owned It
Deep dive into Microsoft Edge security architecture, exploring sandbox initialization, browser broker implementation, and renderer security isolation.
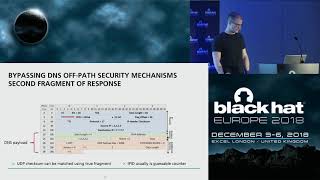
Off-Path Attacks Against PKI
Explore vulnerabilities in Certificate Authorities and learn how off-path attackers can compromise PKI security, undermining the foundation of Internet application trustworthiness.
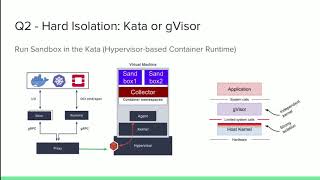
Cloud-Native Sandboxes for Microservices - Understanding New Threats and Attacks
Explore redesigned sandboxing for container environments, improving detection of microservice-oriented attacks and addressing performance challenges in contemporary systems.
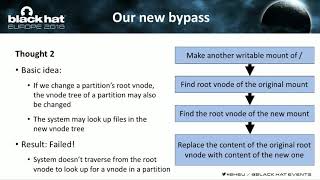
The Last Line of Defense - Understanding and Attacking Apple File System on iOS
Explore APFS architecture, previous attacks, and a new method to bypass mitigations, potentially compromising iOS file system security.
Applied Self-Driving Car Security
Explore self-driving car security with industry experts, covering technology, potential attacks, and defense strategies for this emerging field.