Security Design and High Risk Users
Security design for high-risk users: understanding human outcomes, adversary capabilities, and synthesizing solutions. Explores challenges and practical processes for improving security beyond code and systems.
DCART - Decoupled Components for Automated Ransomware Testing
Explore a framework for controlled ransomware testing, focusing on decoupled components for detonation and detection. Learn about design, development, and automated testing methodologies for behavioral ransomware analysis.
Exploiting Zoom on MacOS
Exploración detallada de una vulnerabilidad de ejecución remota de código en el cliente Zoom para macOS, incluyendo técnicas de ingeniería inversa y explotación aplicables a otras aplicaciones.
Binder - The Bridge To Root - Hongli Han and Mingjian Zhou
Exploración detallada de la vulnerabilidad "Waterdrop" en el controlador Binder de Android, que permite escalar privilegios y obtener acceso root en dispositivos populares, incluyendo los Pixel más recientes.
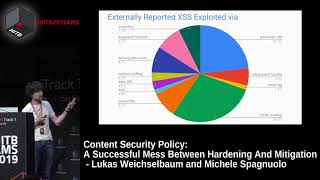
A Successful Mess Between Hardening and Mitigation
In-depth analysis of Content Security Policy for XSS prevention, exploring its effectiveness, debunking myths, and sharing real-world data on successful XSS mitigation in sensitive applications.
Overcoming Fear - Reversing With Radare2
Comprehensive guide to reversing with Radare2, covering installation, basic commands, visual modes, configuration, and practical applications. Suitable for beginners and professionals in computer security.
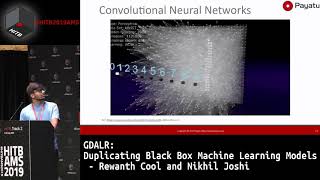
Duplicating Black Box Machine Learning Models
Exploración de técnicas avanzadas para duplicar modelos de aprendizaje automático de caja negra, destacando vulnerabilidades en servicios en la nube y proponiendo un nuevo método de ataque más eficiente.
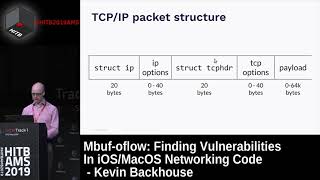
Finding Vulnerabilities in iOS - MacOS Networking Code
Explore iOS/macOS networking vulnerabilities, focusing on mbuf processing in XNU kernel. Learn about network packet structures, vulnerability discovery techniques, and PoC exploit development.
Hourglass Fuzz - A Quick Bug Hunting Method
Introducción a Hourglass Fuzz, un método rápido de búsqueda de errores para Android que supera las limitaciones de los sistemas de fuzzing típicos, con ejemplos de vulnerabilidades descubiertas en controladores gráficos y Bluetooth.
Hey Attacker! I Can See You!
Exploring cloud-scale deception technology to track and analyze attackers, enhancing Azure security through psychological and technical approaches for better threat intelligence and user protection.
Swiping Through Modern Security Features
Exploring iOS 6 security features and jailbreak techniques, including kernel ASLR, code signing, and exploit methods. Insights from expert developers on bypassing modern mobile security protections.

SSRF PWNs - New Techniques and Stories
Découvrez de nouvelles techniques d'attaques SSRF, leurs impacts sur la sécurité des applications web et des exemples concrets d'exploitation, présentés par deux experts en sécurité informatique.
A Short History of the JavaScript Security Arsenal
Explore the evolution of JavaScript security tools and techniques over six years, from basic port scanners to advanced frameworks, with insights from expert Petko D. Petkov.
Hacking in the Far East
Explore security challenges and hacking techniques in Japan, South Korea, and Hong Kong. Gain insights into corporate policies, smart cards, social engineering, and unique cultural aspects affecting cybersecurity in East Asia.
Harmony In Motion
Exploring the challenges of seamless user experience in the metaverse, focusing on IoT integration, connectivity, and security in a fully connected, intelligent world.
A New Fuzzing Method for Android
Innovative Android fuzzing method combining function points to find vulnerabilities. Proven effective with 50+ bugs discovered on major OEM devices, inspiring new approaches in mobile security research.
Static Binary Analysis - The Essentials
Dive into reverse engineering and static malware analysis essentials with Igor Kuznetsov. Learn visual inspection, disassembly techniques, and structure analysis using IDA Pro and Ghidra.
Web Applications Bug Hunting - Fundamentals
Explore web application security fundamentals, attack vectors, and tools for bug hunting. Learn key concepts to kickstart your career in application security.
Zero-Day Exploits of Operation WizardOpium
Detailed analysis of zero-day exploits and watering-hole attacks in Operation WizardOpium, covering technical aspects, spreading methods, and security implications.
Hiding in Plain Sight - PhantomLance Comes into Play
Uncover the sophisticated PhantomLance Android spyware, its evolution, deployment tactics, and connections to other malware campaigns in this cybersecurity investigation presentation.
Zebrocy’s Multi-Language Malware Salad
Explore Zebrocy's unique APT tactics, multi-language malware, and evolving techniques in this cybersecurity analysis by Kaspersky's Kurt Baumgartner.