Infrastructure Based Security
Explore infrastructure-based security, covering cloud, IoT, hiring experts, historical perspectives, and modern challenges. Learn strategies to implement robust security measures in today's complex digital landscape.
Python - The Wonder Woman of Embedded Device Reversing
Explore Python's power in embedded device reverse engineering, covering triage, scripting, analysis, and IDA integration for efficient vulnerability research.
Aiding Static Analysis - Discovering Vulnerabilities in Binary Targets through Knowledge Graph
Explore advanced techniques for vulnerability detection in binary targets using knowledge graphs, static analysis, and specialized tools like Binary Ninja and Kraken.
Hunting for Memory Resident Malware
Explore techniques for detecting memory-resident malware, including API analysis, post-breach detection, and CLR hooking. Learn why memory hunting is crucial in cybersecurity.
Windows Rootkit Development - Python Prototyping to Kernel Level C2
Explore kernel-mode drivers for network traffic control, TCP connection handling, and proxy manipulation. Learn weaponization and deployment strategies for advanced Windows rootkit development.
Red Team Level Over 9000 - Fusing the Power of NET With a Scripting Language of Your Choosing
Explore advanced red teaming techniques by combining .NET with scripting languages, covering concepts like IronPython, WebAssembly, and PowerShell for enhanced offensive capabilities.
Old Tools New Tricks - Hacking WebSockets
Explore WebSocket hacking techniques, from basic concepts to advanced exploits, using various tools and methods for secure testing and vulnerability assessment.
Adventures in Azure Privilege Escalation
Explore Azure privilege escalation techniques, from initial entry to tenant admin access, with practical examples and demonstrations for enhancing cloud security knowledge.

You Moved to Office 365 - Now What
Explore Office 365 security, auditing, and protection strategies. Learn about cloud attack prevention, Azure Sentinel, and identity protection to enhance your organization's cloud security posture.
Attacking Azure Environments with PowerShell
Learn to exploit Azure environments using PowerShell, covering data dumping, modules, and various services. Gain insights into escalation techniques and practical demonstrations.
Bug Hunting in RouterOS
Explore RouterOS vulnerabilities, including developer backdoors, key negotiation, and protocol analysis. Learn about CVEs and policy discovery techniques for enhanced network security.
Perfect Storm - Taking the Helm of Kubernetes
Explore Kubernetes security, from container basics to advanced attack techniques and cloud security considerations, with practical insights and defensive strategies.
Android App Penetration Testing 101
Learn Android app penetration testing essentials, including tools, methodologies, and practical techniques for identifying vulnerabilities and securing mobile applications.
Offensive Browser Extension Development
Learn to develop and analyze browser extensions, exploring potential security risks and malicious behaviors in web store submissions and installations.
Contextomy - Let's Debug Together
Explore a critical iOS design flaw allowing remote code execution through debug session hijacking. Learn about the vulnerability's discovery, research, exploitation, and Apple's fix.
Bheem OS - A Next-Gen Reasonably Secure OS
Explore Bheem OS, a next-gen secure operating system that isolates apps in MicroVMs, offering enhanced security, usability, and performance. Learn about its architecture, features, and advantages over traditional systems.
Introduction to the OWASP ModSecurity Core Rule Set
Learn about OWASP ModSecurity Core Rule Set, a powerful open-source web application firewall. Discover key features like paranoia levels and anomaly scoring, and see its effectiveness in protecting against various attacks.
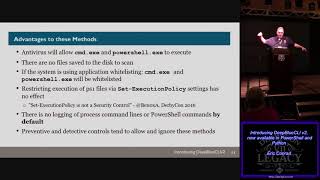
Introducing DeepBlueCLI v2 Now Available in PowerShell and Python
Explore DeepBlueCLI v2's enhanced features for Windows malware detection, including PowerShell and Python implementations, regex improvements, and automated whitelisting techniques.
Subverting Trust in Windows - A Case Study of the How and Why of Engaging in Security Research
Explore Windows security research through a case study on subverting trust, covering dynamic analysis, code signatures, and PowerShell, with insights on validating trust and lessons learned.
Practical Techniques for AV Bypass
Explore practical techniques for bypassing antivirus software, covering various scenarios, tools, and programming languages to enhance your cybersecurity skills.
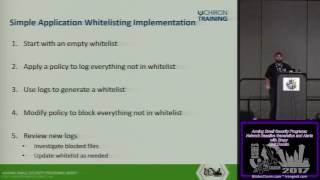
Arming Small Security Programs - Network Baseline Generation and Alerts
Learn to generate network baselines and alerts for small security programs using Bro, Python scripts, and Brophy. Enhance your network monitoring and threat detection capabilities.