The Insecurity Caused by Trusting Your Client-Side Storage
Explore vulnerabilities in client-side storage, including cookies and web storage, and learn exploit patterns and attack vectors to enhance web application security.
The State of Credential Stuffing and the Future of Account Takeovers
Explore credential stuffing, account takeovers, and evolving cybersecurity threats. Learn about attack methods, defense strategies, and the future of online fraud prevention.
Attacking Modern Web Technologies
Explore modern web vulnerabilities with top hacker Frans Rosén. Learn about exploiting postMessage, WebSockets, cloud misconfigurations, and more. Gain insights to enhance your web security knowledge.
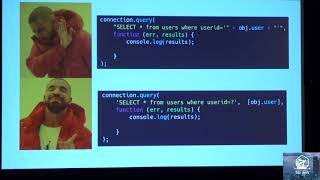
OWASP Top 10 for JavaScript Developers
Explore JavaScript vulnerabilities in OWASP Top 10, covering client and server-side issues with focus on modern frameworks and NodeJS. Learn prevention techniques for secure web development.
Magecart - A Growing Threat to E-Commerce Sites
Explore Magecart's e-commerce threats, attack techniques, and defense strategies. Learn about vulnerabilities, compromises, and protective measures for online shops and payment systems.
Uninvited Guests - Understanding Malicious Web Bots with OWASP Handbook
Explore malicious web bots and automated threats using OWASP's Handbook. Learn about scalping, scraping, and sniping, with real-world examples and countermeasures for better online security.
The Importance of the Cloud and the Developers Communities in Fighting Cyber Crime
Explore cloud and AI's role in cybersecurity, innovative trends, and Microsoft's strategies to combat evolving cyber threats in this insightful talk by a leading industry expert.
DevSecOps with OWASP DevSlop
Learn DevSecOps through hands-on examples with OWASP DevSlop. Explore secure component management, secret handling, testing techniques, and open-source tools to enhance your pipeline security.
Common API Security Pitfalls
Explore common API security pitfalls, their root causes, and best practices for protection. Learn to assess and improve API security, focusing on authentication, encryption, and input validation.
Temporal - It's Not Your Developers' Fault
Explore how software development evolution impacts security, from traditional methods to Cloud Native workloads, and why increasing breaches aren't solely developers' responsibility.
Temporal - Code-Origin Policy - Towards a Formal User Privacy Protection for the Web
Explore a novel approach to web privacy protection through code-origin monitoring, offering customizable user safeguards and formal assurance mechanisms for JavaScript execution.
Temporal - Achieving the Web Isolation Nirvana - How Far Along Are We?
Explore web isolation's evolution, current approaches, and future challenges. Learn about a client-side sandboxing solution and discuss the future of web application security.
AppSec - From Outsiders to Allies
Chris Wysopal explores AppSec's evolution from hacker-driven to a critical ally in software development, emphasizing the need for collaboration, shared accountability, and integrated security practices in modern development processes.
Extending WAFs at the Application Layer
Explore application-level security control with Sanwaf, an alternative to traditional WAFs. Learn its structure, datatypes, and implementation for enhanced web application protection.
Why Developers Struggle with AppSec
Explore challenges developers face in application security, trust issues, and solutions for integrating security into the development process, with insights on tools and production biases.
Magecart 2020 - The New Face of XSS
Explore Magecart's evolution, injection techniques, and threat complexity. Learn from real-world case studies and discover strategies to prevent these sophisticated web skimming attacks.
Before It's Out the Door - Securing Outbound Open Source
Explore strategies for securing open-source projects before release, covering governance, code review, and infrastructure. Learn to address security concerns and manage community projects effectively.
HTTP3 Security
Explore HTTP3 security with Robin Marx: handshakes, QuickSense, passive proxies, deep packet inspection, and QUIC vs TCP. Gain insights into the latest web protocol advancements.
The Now and the Future of Malicious WebAssembly
Explore WebAssembly's evolution, performance, and security implications, including its use in cryptojacking and potential future developments in web-based attacks.
OWASP Based Threat Modelling - Creating A Feedback Model in an Agile Environment
Learn to create an effective threat modeling feedback system in Agile environments using OWASP principles. Explore frameworks, processes, and strategies for risk management and application security.
OWASP Flagship Projects - OWASP ModSecurity Core Rule Set
Explore OWASP ModSecurity Core Rule Set: web application firewall rules, paranoia levels, and project developments for enhanced security and threat protection.