OWASP Flagship Projects - OWASP Dependency-Check
Learn to identify and mitigate vulnerabilities in software dependencies using OWASP Dependency-Check, enhancing application security through effective composition analysis.
OWASP Flagship Projects - OWASP Juice Shop
Explore OWASP Juice Shop, a vulnerable web application for security training. Learn about challenges, cross-site scripting, coding exercises, and future enhancements in this comprehensive overview.
OWASP Flagship Projects - OWASP Amass
Explore OWASP Amass, a powerful tool for information gathering and external asset discovery in cybersecurity. Learn its features, data sources, and future developments.
Lessons Learned from the DevSecOps Trenches
Panel discussion on scaling AppSec programs, featuring insights from security leaders at major tech companies. Covers high-ROI efforts, effective tools, and lessons learned to help organizations improve their security practices.
Contact Center Authentication
Explore best practices for authenticating customers over the phone in contact centers, including research findings, common pitfalls, and innovative solutions for improved security and user experience.
Threat Model Every Story - Practical Continuous Threat Modeling Work for Your Team
Explore continuous threat modeling for agile teams, focusing on collaborative methodologies and the PyTM open-source tool to enhance product security throughout development.
Cache Me If You Can - Messing with Web Caching
Explore web caching vulnerabilities including Web Cache Deception, Edge Side Include Injections, and Web Cache Poisoning. Learn detection techniques and mitigation strategies for these emerging threats in application security.
Automated Account Takeover - The Rise of Single Request Attacks
Explore the rise of single request attacks in account takeovers, their sophistication, and effective mitigation strategies through real-world case studies and expert insights.
Cloud Forensics - Putting The Bits Back Together
Explore cloud forensics challenges and solutions in AWS, focusing on server breaches, disk imaging, and incident response techniques for various EC2 instance types and EBS volumes.
Remediate The Flag - Practical AppSec Training Platform
Hands-on platform for developers to find and fix security vulnerabilities in code. Offers real-time feedback, scoring, and customizable exercises to improve application security skills.
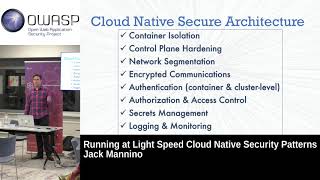
Running at Light Speed - Cloud Native Security Patterns
Explore cloud-native security patterns, including container isolation, control plane hardening, and network segmentation. Learn about authentication, authorization, and secrets management in cloud environments.
Human Factors That Influence Secure Software Development
Explores human factors influencing secure software development, including environmental conditions, developer characteristics, and team dynamics. Discusses strategies to identify and mitigate vulnerability-prone code before issues arise.
Battle Tested Application Security
Insights on building effective Application Security programs, focusing on security culture, defensive capabilities, and organizational empowerment across different environments.
Flying Above the Clouds - Securing Kubernetes
Explore Kubernetes security, from container isolation to authentication and authorization. Learn to build resilient cloud-native systems and deploy secure services in a distributed environment.
Serverless Infections - Malware Just Found a New Home
Explore serverless security risks through a live demo of RCE attacks, data infiltration, and self-duplicating malware in cloud environments. Learn best practices for securing serverless architectures.
Deserialization - What, How and Why Not
Explore insecure deserialization risks, vulnerabilities, and prevention techniques through code examples and live demos, focusing on Java but applicable to other languages.
A New Framework to Automate MSTG and MASVS in Your CI/CD Pipeline
Automate mobile app security testing using BDD and UI automation frameworks. Integrate OWASP MASVS/MSTG into CI/CD pipelines for faster, repeatable security checks at DevOps speed.
Web Application Compromise Mitigation with Crypto Anchoring - AppSecUSA
Explore crypto anchoring as a solution to protect sensitive data from breaches, paired with effective monitoring for enhanced web application security.
The Anatomy of a Secure Web Application in Java Using Spring Security and Apache Fortress
Practical guidance on implementing secure Java web applications using Spring Security and Apache Fortress. Covers authentication, authorization, and confidentiality controls with hands-on demos and code examples.
Security as a Service - Work Where You Engineers Live
Integrating security into existing development workflows for efficient vulnerability management and faster response times. Learn how to leverage automation and project tracking tools to enhance security practices.
Open Source Security Tools for Kubernetes Applications
Explore open-source tools for securing Kubernetes applications, covering image scanning, runtime security, and anomaly detection. Learn practical strategies for maintaining a secure cloud-native environment.