Monitoring Attack Surface and Integrating Security into DevOps Pipelines
Explore strategies for integrating security into DevOps pipelines, focusing on attack surface monitoring, automated testing, and merging static and dynamic results.
Doing Security in 100 Milliseconds - The Speed of Serverless Computing
Explore serverless computing's impact on security, covering key areas like software supply chain and attack detection. Learn practical approaches and see a demo of building and securing a serverless application.
Reversing Web Applications
Explore web application reverse engineering techniques, from information gathering to active testing, to understand behavior, analyze code, and improve security assessments.
SSL and the Future of Authenticity
Explore SSL's role in online security, challenges with certificate authorities, and innovative approaches to authentication in the digital age.
Threat Modeling Cloud Apps - What You Don't Know Will Hurt You
Explore threat modeling for cloud applications, focusing on AWS services, security controls, and potential risks. Learn to identify assets, adapt to cloud architectures, and address new security challenges.
Android Security, or This Is Not the Kind of 'Open' I Meant
Explore Android security vulnerabilities, reverse engineering techniques, and potential solutions with insights from Trustwave SpiderLabs expert Mike Park.
Pwning Intranet with HTML 5
Explore HTML5's potential for intranet exploitation using BeEF framework. Learn footprinting, network discovery, port scanning, and inter-protocol exploitation techniques.
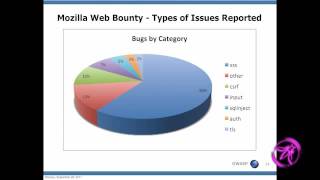
Security Evolution - Bug Bounty Programs for Web Applications
Explore the evolution of web security through bug bounty programs, focusing on Mozilla's experience, benefits, challenges, and ethical considerations.
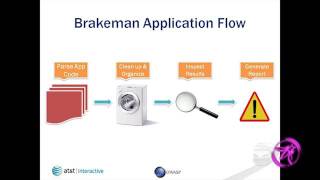
Brakeman & Jenkins - The Duo Detects Defects in Ruby on Rails Code
Explore static analysis tools for Ruby on Rails, focusing on Brakeman and Jenkins integration. Learn about security warnings, code updates, and best practices for detecting defects.
An Introduction to ZAP - The OWASP Zed Attack Proxy
Learn to use ZAP, an open-source web application security scanner. Explore features like active scanning, fuzzing, and brute force attacks to enhance your penetration testing skills.
Implementing AppSensor in ModSecurity
Explore advanced web application security techniques using AppSensor and ModSecurity, focusing on detection points, SQL injection prevention, and innovative defense strategies.
A DevOps View of AppSec
Explore DevOps history and its impact on AppSec, charting a path for DevSecOps success through standardization, automation, and Agile principles.
Cloud Security at Scale - Managing the Chaos
Explore the challenges and best practices for securely migrating large enterprises' legacy infrastructure to the cloud, with actionable insights for a successful transition.
Securing Modern API and Microservice Based Applications by Design
Learn to secure modern API and microservices architectures with expert insights on key concerns, architectural patterns, and actionable solutions for robust application security.
The A's, B's, and Four C's of Testing Cloud-Native Applications
Explore cloud-native app testing with the A's, B's, and Four C's framework, covering threat modeling, API testing, and security management for modern software development.
Micro-services Challenges - Istio to the Rescue
Explore Istio's solutions for micro-services challenges, including traffic management, policy enforcement, and security, to enhance scalability and operational efficiency.
New Age Cloud Security - How to Build Secure Multi-Cloud Applications and Still Sleep Well
Learn to build secure multi-cloud applications with modern techniques. Explore industry trends, development phases, and essential components like TLS, DNS, user management, and data encryption for robust cloud security.
Breaking Into Red Teaming
Explore essential skills, objectives, and methodologies for successful Red Team operations, covering physical access, cloud infrastructure, and effective communication strategies.
How to Build an Effective Malware Protection Architecture for File Uploads in Modern Web Apps
Explore a novel approach to automated malware analysis for file uploads in web apps, focusing on scalability, performance, and effective detection of malicious content.
Security Testing - Is Automation Failing Us?
Explore the challenges of security testing automation and its impact on identity, privacy, and overall system protection in modern software development.
Secure Configuration in the Cloud
Explore secure configuration management in cloud environments, focusing on protecting sensitive assets, managing configuration secrets, and implementing best practices for DevOps security.