Security Appliances Internals
Explore the inner workings of security appliances, their architecture, and implementation. Gain insights into cloud security and key takeaways for effective defense strategies.
All Your Cloud Are Belong To Us - Hunting Compromise in Azure
Explore techniques for identifying and mitigating compromises in Azure cloud environments, focusing on network security, threat detection, and best practices for cloud security.
Ads Networks Are Following You, Follow Them Back
Explore how ad networks track users and learn techniques to monitor and analyze their behavior, including tools like ET Toolkit and HTTP Bloom for enhanced web privacy.
When Virtual Hell Freezes Over - Reversing C++ Code
Explore advanced C++ code reversing techniques, focusing on dynamic object creation, vtables, and multiple inheritance. Learn automated methods for efficient analysis.
Hunting Android Malware - A Novel Runtime Technique for Identifying Malicious Applications
Novel runtime technique for identifying malicious Android apps through instrumentation, addressing frustrations with static analysis and offering practical demonstrations and insights.
Witness the Russian Attack - Live Demos of Their Steps, Tools, Techniques
Explore Russian cyberattack techniques through live demonstrations, covering infection methods, web injects, traffic manipulation, and victim targeting strategies.
Attacking Nextgen Firewalls
Explore techniques for attacking next-generation firewalls, focusing on administrative interfaces, embedded systems, and potential vulnerabilities in security features like VPNs and user authentication.
SyScan360'16 Singapore - Key Value Injections Here
Explore key value injections, their impact on serialization, and implications for React and CouchDB in this technical deep dive.
iOS 678 Security - A Study in Fail
Explore iOS security vulnerabilities, jailbreak techniques, and Apple's responses across iOS 6-8. Gain insights into historical exploits and the evolving landscape of iOS security.
Navigating a Sea of Pwn - Windows Phone 8 Appsec
Explore Windows Phone 8 app security, covering structure, models, restrictions, encryption, and vulnerabilities. Learn about marketplace validation and protection strategies.
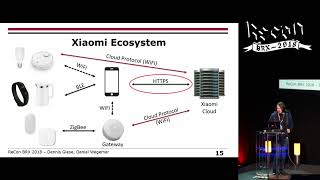
Reversing IoT - Xiaomi Ecosystem
Explore Xiaomi IoT ecosystem security, firmware extraction, and cloud communication. Learn to modify devices, implement new functions, and gain independence from proprietary cloud services.
Scaling MISP With The Cloud
Learn strategies for scaling MISP using cloud technologies to enhance threat intelligence sharing and improve cybersecurity operations in large-scale environments.
Hardware Side Channel Attacks on the Cheapest
Explore side channel attacks on low-cost hardware, covering power analysis, encryption vulnerabilities, and practical demonstrations. Learn acquisition techniques and countermeasures.
API Security - Is it the New Application Attack Surface and How to Secure at Enterprise Scale
Explore API security challenges, threats, and enterprise-scale solutions. Learn about modern attack surfaces, recent breaches, and effective strategies for protecting sensitive data in API-driven architectures.
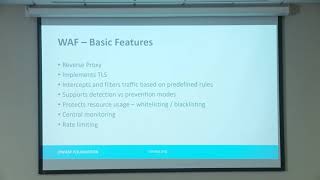
Your Frontier Defense - Understanding Web Application Firewalls
Explore WAF options, features, and challenges across cloud providers and self-managed solutions for enhanced web application security and defense-in-depth strategies.
Doing This One Crazy Thing Will Change Your AppSec Program Forever
Discover how to revolutionize your AppSec program through effective communication, prioritization, and innovative strategies for securing software development.
Developing and Managing an OWASP Project - Projects 101
Learn to create, manage, and grow an OWASP project. Explore naming, sponsorship, levels, services, and resources for successful open-source security initiatives.
The Final Frontier - Automating Dynamic Security Testing
Automating dynamic security testing: strategies for efficient, scalable DAST integration in software delivery pipelines, addressing challenges and trade-offs for seamless DevSecOps implementation.
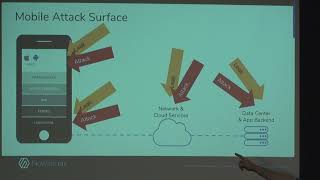
Insiders Guide to Mobile AppSec with OWASP MASVS
Explore mobile app security essentials using OWASP MASVS, covering data storage, network issues, authentication, and anti-tampering. Learn practical tools and tactics for effective mobile pen testing and security assessment.
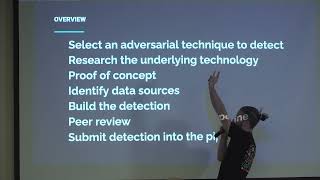
Detection Engineering Methodologies
Comprehensive methodology for engineering effective threat detections, covering structure, processes, and technologies for a successful detection program.
Reversing Client Side JavaScript Using the Chrome Dev Tools Protocol
Explore Chrome Dev Tools protocol for JavaScript reversal, bug finding, and vulnerability detection. Learn to modify web app behavior and automate pentesting tasks using Go-based plugins.