How Surveillance Law was Expanded in Canada - What the Media has Reported - What’s Next
Explore Canada's expanded surveillance laws, media coverage, court cases, and future implications for cybercrime investigations and individual privacy rights.
Practical Uses of Program Analysis - Automatic Exploit Generation
Explore automatic exploit generation through program analysis techniques, including instrumentation and symbolic execution, with practical demonstrations and tool insights.

Threat Modeling for the Gaming Industry
Explore gaming industry security challenges, focusing on client-side logic, network protocols, account management, and untrusted platforms to enhance overall security and user experience.
OO RE with HexraysCodeXplorer
Explore object-oriented reverse engineering techniques for modern malware analysis, focusing on C++ code reconstruction and tools like HexRaysCodeXplorer for tackling complex malware frameworks.
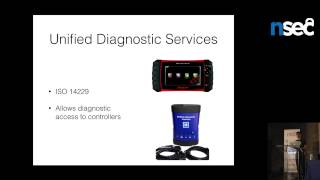
Hopping on the CAN Bus
Learn to hack your car's CAN bus using an open-source toolkit. Explore CAN basics, attack methods, hardware/software tools, diagnostic protocols, and security implications for modern vehicles.
SSO Wars - The Token Menace
Explore SSO vulnerabilities, focusing on JWT and SAML tokens. Learn attack vectors, signature verification issues, and real-world implications for frameworks like WCF and SharePoint.
From Email Address to Phone Number - A New OSINT Approach
Explore innovative OSINT techniques to uncover phone numbers from email addresses, enhancing privacy and security investigations with cutting-edge methodologies and tools.
Serverless Infections - Malware Just Found a New Home
Explore serverless architecture vulnerabilities and learn how malware can exploit AWS Lambda functions, with insights on prevention and security best practices.
Securing Robots at Scale
Explore robot security challenges, attack surfaces, and protection strategies for hardware, software, and user privacy in the era of widespread robotic adoption.
Lessons Learned by the WordPress Security Team
Insights from WordPress Security Team's journey: challenges, strategies, and lessons in safeguarding open-source software and educating users on cybersecurity best practices.
The Chrome Crusader
Explore Chrome extension vulnerabilities, security considerations, and potential exploits. Learn about architecture, headers, and isolation techniques for safer browsing experiences.
CheckPlease - Payload-Agnostic Sandbox Detection
Explore payload-agnostic sandbox detection techniques, including sleep evasion, encryption, and user activity analysis. Learn to build profiles and implement various detection methods across languages.
Pwning Software-Defined Networking - SDN
Explore software-defined networking vulnerabilities, focusing on OpenFlow, controllers, and REST APIs. Learn to manipulate traffic flow and exploit SDN weaknesses.
WAFs FTW! A Modern DevOps Approach to Security Testing Your WAF
Explore modern DevOps approach to security testing Web Application Firewalls (WAFs) using Framework for Testing WAFs (FTW). Learn objective WAF evaluation, rapid prototyping, and continuous testing strategies.
Federated Login CSRF
Explore federated login CSRF vulnerabilities in OpenID Connect and OAuth 2.0, examining attack scenarios, risks, and mitigation strategies for secure identity linking in web applications.
Androsia - A Tool for Securing In Memory Sensitive Data
Innovative tool for securing sensitive data in Android apps through static analysis and bytecode transformation, enhancing defense-in-depth even after compromise.
Building Secure ASP.NET Core MVC Applications
Explore ASP.NET Core MVC security features, including XSS and CSRF protection. Learn to build robust web applications with modular architecture and cross-platform compatibility.
Differences Between Web Application Scanning Tools When Scanning for XSS and SQLi
Investigates differences between web application scanning tools for XSS and SQLi, addressing challenges in modern web architectures and suggesting improvements for effective vulnerability detection.

Cryptography in the Age of Heartbleed
Cryptography expert discusses challenges in encryption, recent vulnerabilities in web protocols, and securing cryptographic software against sophisticated attackers, emphasizing the need for simplification.
The DevSecOps Playbook - From A Practitioner's Perspective
Practical guide to implementing DevSecOps, covering mindset shifts, automation, communication strategies, skill requirements, and collaborative tools for safer software development.
Creating an AppSec Pipeline With Containers in a Week - How We Failed and Succeeded
Explore the journey of implementing an AppSec pipeline using Docker containers, addressing challenges, solutions, and best practices for effective security integration in development workflows.