Run-Time Tools to Aid Application Security Assessments
Explore runtime tracing tools and techniques for application security assessments, enhancing your ability to uncover vulnerabilities in real-world testing scenarios.
Red Teaming macOS Environments with Hermes the Swift Messenger
Explore the development of Hermes, a Swift implant for macOS red teaming, integrated with Mythic C2 framework. Learn about its capabilities and detection methods using Apple's ESF.
Hook, Line and Sinker - Pillaging API Webhooks
Explore "Webhook Boomerang flaws" and learn how to exploit SSRF vulnerabilities in API webhooks, potentially compromising cloud credentials despite security measures.
Exposed Secrets - How Public Git Repositories and Docker Images Expose Millions of Secrets Like API Keys and Security Certificates Every Year
Uncover the alarming spread of exposed API keys and secrets in public repositories. Learn about research findings, causes, and implications for cybersecurity.
The Power of Guardrails - How to Slash Your Risk of XSS in Half
Discover how secure code defaults can significantly reduce XSS vulnerabilities and elevate overall security. Learn strategies to implement effective guardrails and minimize recurring security risks.
Go With The -Work-flow
Unveiling security risks in cloud workflow platforms: misconfigurations, credential exposure, data leakage, insecure coding, and containerized malware. Eye-opening research for IT professionals.
Offensive Javascript Techniques for Red Teamers
Explore advanced JavaScript techniques for network reconnaissance and exploitation, focusing on rapid execution and targeting internal vulnerabilities from external sources.
Software Bill of Materials - Progress toward Transparency of Third-Party Code
Explore progress in developing software bills of materials, their value in enhancing transparency of third-party components, and ongoing efforts to standardize and implement across sectors.
Building Identity for an Open Perimeter
Explore Netflix's cloud-first approach to identity and security, focusing on SSO, MFA, adaptive authentication, and user-centric solutions for a modern, open perimeter.
The 5 Most Dangerous New Attack Techniques, and What's to Come
Experts from SANS Institute discuss the most dangerous new attack techniques, including hardware attacks, big data weaponization, crypto mining, ICS safety threats, and cloud breaches, offering insights on defeating these evolving threats.
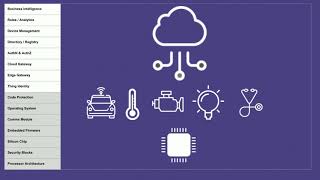
Identity-Based Security and Privacy for the Internet of Things
Explore IoT identity management challenges, opportunities, and solutions for seamless authentication, robust security, and user-controlled privacy across diverse devices and platforms.
Padding Oracles Everywhere
Explore padding oracle attacks in cryptography, their widespread impact, and practical exploitation techniques in various systems and protocols.
A Visual Journey to Demystifying OAuth2 and OIDC - Why Do They Exist and How to Properly Use Them to Secure Your Applications
Explore OAuth2, OIDC, and related security standards through visual explanations. Learn their purposes, differences, and proper implementation for secure authentication and authorization.
Hacking JavaScript Desktop Apps with XSS and RCE
Explore techniques for auditing Electron apps, understanding XSS in desktop environments, and exploiting vulnerabilities to achieve remote code execution in JavaScript-based applications.
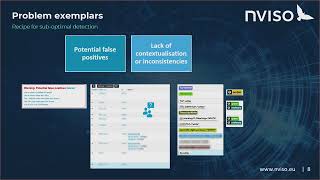
In Curation We Trust - Generating Contextual and Actionable Threat Intelligence
Optimizing threat intelligence with MISP: Learn to curate, contextualize, and automate TI feeds for actionable insights, reducing false positives and enhancing SOC, IR, and malware analysis collaboration.
Defeating EDRs Using Dynamic Invocation in C#
Explore advanced techniques for bypassing Endpoint Detection and Response systems using Dynamic Invocation in C#, enhancing your understanding of cybersecurity vulnerabilities and defenses.
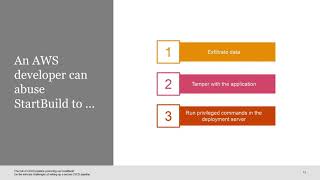
The Risk of CI - CD Pipeline Poisoning via CodeBuild
Explore CI/CD pipeline vulnerabilities in AWS services, focusing on CodeBuild abuse. Learn how small decisions can compromise security, bypass controls, and potentially lead to pipeline poisoning.
Incident Response in the Cloud - Foggy with a Ray of Sunshine
Explore challenges and solutions for incident response in cloud environments, focusing on logging options, visibility issues, and automated response techniques for improved security operations.
Cryptographically Secure Data Analysis for Social Good
Secure multi-party computation enables analysis of sensitive salary data to calculate pay disparities while maintaining confidentiality, demonstrating potential for social impact in privacy-constrained contexts.
Putting Privacy Notices to the Test
Exploring challenges and improvements in privacy notices and security warnings, discussing cognitive processes, and presenting user studies to enhance effectiveness through iterative design.
Secrets at Scale - Automated Bootstrapping of Secrets & Identity in the Cloud
Explore Netflix's innovative approach to securely managing secrets and identities for thousands of microservices in a cloud environment, addressing scalability and self-healing challenges.