Demystifying COM
Explore the intricacies of Component Object Model (COM) technology, its security implications, and potential vulnerabilities in Windows systems with expert James Foreshaw.
Real Life Software Defined Security
Explore practical implementations of software-defined security, examining real-world applications and strategies for enhancing cybersecurity through programmable, adaptable solutions.
Towards a LangSec Aware SDLC
Explore integrating Language-theoretic Security principles into the Software Development Life Cycle for enhanced system security and robustness.
Introduction to IoT Reverse Engineering
Introduction to firmware reverse engineering for IoT devices, focusing on information gathering, emulation environment setup, and analysis techniques. Includes a practical example using a home router.
Invoke-DOSfuscation - Techniques for S-level CMD Obfuscation
Explore advanced CMD obfuscation techniques used by threat actors, including string manipulation and encoding methods. Learn about new obfuscation approaches and their detection implications for cybersecurity professionals.
Building Systems on Shaky Grounds - 10 Tactics to Manage the Modern Supply Chain
Explore 10 tactics for managing modern software supply chains, balancing open-source benefits with security risks. Learn to assess vendors, conduct red team exercises, and implement effective incident response strategies.
Injecting Security into Web Apps
Explore innovative approaches to web application security beyond traditional WAFs, focusing on internal application monitoring and real-time threat detection to prevent zero-day attacks and data exfiltration.
The Forbidden Image - Security Impact of SVG on the WWW
Explore SVG's security implications, potential vulnerabilities, and protective measures. Learn about malicious SVG examples and a new filtering tool for safer SVG usage on the web.
A Close Look at Rogue Antivirus Programs
Comprehensive analysis of rogue security software, examining characteristics, behavioral patterns, and potential benefits. Explores methods to differentiate from legitimate antivirus programs and investigates the financial aspects behind these products.
Locking the Throne Room - ECMA Script 5, a Frozen DOM and the Eradication of XSS
Innovative approach to prevent XSS attacks using ECMA Script 5 features, sealing DOM properties and creating client-side IDS/IPS systems for modern browsers.

Attacking XML Processing
Explore XML security vulnerabilities, from browsers to enterprise solutions. Learn about DTD, SVG, XSLT, XPath, and XML databases, with practical examples and PoC code.
HTML5 Something Wicked This Way Comes
Exploring HTML5's security vulnerabilities and advanced UI-Redressing techniques, demonstrating how attackers can exploit seemingly minor flaws in web applications for malicious purposes.
Bypassing the Android Permission Model
Explore techniques to bypass Android's permission model, including exploiting insecure storage and interfaces. Learn about security risks and mitigation strategies for developers and users.
A Bit More of PE
Explore the intricacies and limits of the PE format, uncovering its peculiarities and pushing boundaries in this detailed examination of file structure weirdness.
iPhone Hacking - Fuzzing and Payloads
Explore advanced iPhone hacking techniques, focusing on fuzzing methodologies and payload creation for exploiting vulnerabilities in iOS devices.
Dissecting Common Android Game Hacking Techniques - Mobile Hacking
Explore Android game modding techniques, focusing on Unity-based games. Learn how attackers modify mobile games and how developers can detect these modifications through APK inspection.
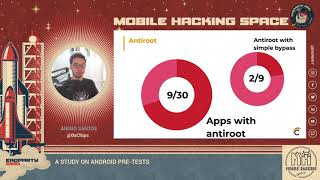
A Study on Android Pre-Tests - Mobile Hacking
Explore Android app security techniques like root detection, SSL pinning, and code obfuscation. Learn to bypass these measures using Frida and static analysis in this beginner-friendly talk on mobile app hacking.
My App Is Running With Kubernetes - Am I Aware of the Potential Exploits That I've Embedded Inside?
Explora las vulnerabilidades potenciales en aplicaciones Kubernetes y aprende prácticas de DevSecOps para mejorar la seguridad en entornos cloud nativos.
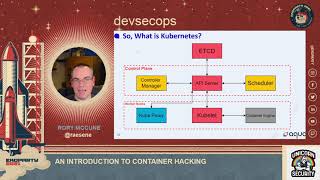
An Introduction to Container Hacking
Explora técnicas de hacking en contenedores, abordando vulnerabilidades y mejores prácticas de seguridad en entornos DevSecOps y tecnologías cloud con el experto Rory McCune.
Introducción a SPIFFE y SPIRE - Autenticando servicios nativos de la nube
Descubre SPIFFE y SPIRE para autenticar servicios nativos de la nube en entornos DevSecOps. Aprende mejores prácticas de seguridad defensiva y ofensiva para aplicaciones en la nube con expertos del sector.
Kubernetes Native Policy Management with Kyverno
Explora la gestión nativa de políticas en Kubernetes con Kyverno, abordando prácticas de DevSecOps para mejorar la seguridad en el ciclo de vida de aplicaciones en entornos cloud.