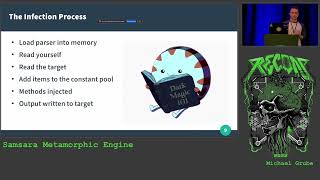
Samsara Metamorphic Engine
Explore Samsara, a viral metamorphic engine for JVM that transforms compiled targets, complicating analysis and enabling supply chain attacks from within IDEs, with added anti-debugging features.
OopsSec - The Bad, the Worst, and the Ugly of APT
Unveiling critical mistakes in APT campaigns across global threat actors, revealing advanced TTPs, and exploring real-time monitoring of sophisticated attacks. Insights on improving organizational defense against evolving threats.
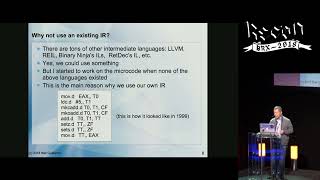
Decompiler Internals - Microcode
Explore the intermediate language used in Hex-Rays Decompiler, its simplicity and power in representing programs, and plans for publication and programmatic access.
When Virtual Hell Freezes Over - Reversing C++ Code
Automated techniques for reversing complex C++ code, focusing on rebuilding inheritance, identifying templates, and tracing program flow to simplify the reverse engineering process.
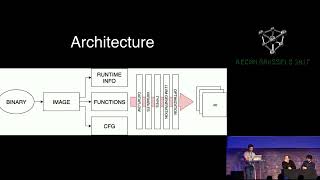
Analyzing iOS Apps - Road from AppStore to Security Analysis Report
Toolset for detecting vulnerabilities in iOS apps: download and decrypt, decompile, statically analyze, and present results. Focuses on high-level semantics reconstruction and common mobile app security flaws.
Recon 2017 Brussels - r2m2 by Guillaume "guedou" Valadon
Presentation on r2m2, a radare2 plugin leveraging miasm2 for reversing rare CPU architectures. Demonstrates integration of powerful reverse engineering tools and simplifies implementation of new architectures.
Using WPP and TraceLogging Tracing to Facilitate Dynamic and Static Windows
Explore advanced Windows tracing techniques using WPP and TraceLogging for enhanced dynamic and static analysis in cybersecurity investigations.
Snow Crashing Virtual Reality - 2019 Edition
Exploring security flaws in VR games leading to remote code execution, highlighting privacy concerns and the need for developers to prevent abuse in online AR/VR communities.
The Road to Qualcomm Trust Zone Apps Fuzzing
Explore Trusted Execution Environment vulnerabilities in Qualcomm's TEE, reverse engineering techniques, and fuzzing methods for TrustZone apps in mobile device security research.
Unveiling the Underground World of Anti-Cheats
Explore the ongoing battle between cheat developers and anti-cheat technologies in gaming. Learn about bypassing techniques and tools for testing anti-cheat software effectiveness.
Attacking Hexagon Security Analysis of Qualcomm's ADSP
Explore Qualcomm's Hexagon ADSP security, architecture, and exploitation techniques. Learn reverse engineering methodologies for proprietary systems and mitigations bypass on Android devices.
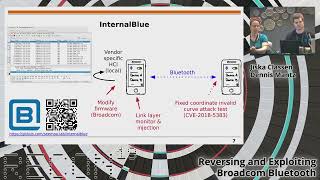
Reversing and Exploiting Broadcom Bluetooth
Insights into reverse engineering Broadcom Bluetooth firmware, including InternalBlue framework, patching techniques, and discovered vulnerabilities CVE-2018-19860 and CVE-2019-6994.
Backdoor Foundry - A Toolchain for Building Application Specific Implants
Explore the creation of application-specific implants using ELF files. Learn about executable containers, software build lifecycle, and advanced techniques for backdoor development in this in-depth technical presentation.
The Path to the Payload - Android Edition
Uncover sophisticated Android malware techniques: obfuscation, anti-analysis, encrypted configs, and fake commands. Learn to reverse-engineer and reveal hidden payloads in this advanced security deep-dive.
Vectorized Emulation - Putting It All Together
Explore vectorized emulation's potential in fuzzing, leveraging AVX-512 for parallel VM execution, enhanced code coverage, and hardware-accelerated taint tracking for improved vulnerability detection.
Taking the Guess Out of Glitching
Explore fault injection techniques in hardware hacking with practical tips on timing, intensity, and effectiveness. Learn innovative methods to determine optimal glitch timing for successful attacks.
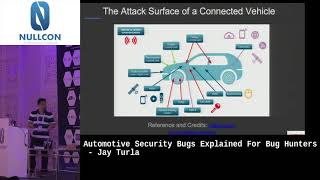
Automotive Security Bugs Explained for Bug Hunters
Explore common automotive security vulnerabilities and learn bug hunting techniques for car systems, from IoT security to CAN bus hacking. Gain insights into PoCs, attacks, and bug prioritization in the automotive industry.
PwdLess - Exploitation Tales from RouterLand
Explore IoT device security through an attacker's perspective, covering fuzzing, reverse engineering, and exploit development. Learn about vulnerabilities, remote execution techniques, and challenges in IoT security.
Building Hardened IoT Implementations With LangSec
Explore Language-theoretic security for IoT, focusing on input recognition and processing separation. Learn about parser combinators, test case generation, and implementation in AMQP protocol for robust IoT systems.
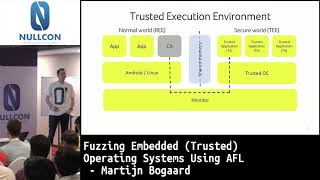
Fuzzing Embedded - Trusted Operating Systems Using AFL
Explore fuzzing techniques for Trusted Execution Environments using AFL, focusing on OP-TEE. Learn about challenges, coverage tracking, and creating initial inputs for effective embedded system security testing.
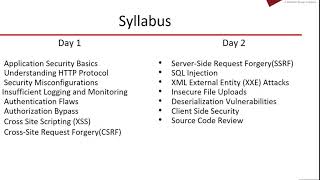
Application Security for Developers - A Holistic Approach
Comprehensive overview of application security for developers, covering holistic approaches to integrate security throughout the development lifecycle.