Practical Security in the Brave New Kubernetes World
Explore Kubernetes security vulnerabilities through hands-on recon and exploitation of clusters, sidecars, and supporting infrastructure. Learn practical techniques for compromising and persisting in real-world K8s environments.
Call Center Authentication
Explore secure customer identity management in call centers, focusing on authentication methods, challenges, and best practices for protecting sensitive information.
Hook, Line and Sinker - Pillaging API Webhooks
Explore techniques for exploiting API webhooks, including SSRF attacks that can lead to cloud compromise, and learn about unique attack vectors in modern web services.
From the Cluster to the Cloud and Back to the Cluster - Lateral Movements in Kubernetes
Explore Kubernetes lateral movements, identity types, and cluster-to-cloud authentication methods. Learn about real-world misconfigurations leading to cluster takeovers and prevention strategies.
Privacy-Friendly QR Codes for Identity
Explore secure QR code frameworks for identity verification, focusing on privacy features that allow selective attribute disclosure. Learn about SMART Health Cards and a new open-source specification.
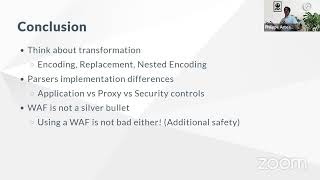
Web Application Firewall Workshop
Hands-on workshop exploring Web Application Firewall bypass techniques, including encoding, SQL injection, protocol switching, and syntax alternatives. Practical exercises with in-depth explanations for each method.
Request Smuggling 101
Explore HTTP Request Smuggling attacks, risks, and payloads. Learn to detect and mitigate vulnerabilities in load balancers and proxies. Includes live demonstration and practical mitigation strategies.
Modern Reconnaissance Phase by APT - Protection Layer
Evolving APT reconnaissance techniques using malicious documents and watering hole attacks. Detailed analysis of obfuscation methods, scripting languages, and mitigation strategies for enhanced cybersecurity.
Android - Practical Introduction into the Insecurity
Practical exploration of Android security vulnerabilities, covering user mistakes and system flaws. Includes demonstrations of local and remote attacks, emphasizing potential risks and damages.
The New Wave of Deserialization Bugs
Explore deserialization vulnerabilities in Java, PHP, and Python. Learn to identify and mitigate risks in enterprise applications using practical examples and tools.
M33tfinder
Discover M33tfinder: a tool for identifying vulnerable web applications. Learn offensive security techniques from an experienced researcher in this informative conference talk.
Secure Programming for Embedded Systems
Explore cryptographic techniques and best practices for secure programming in embedded systems with expert Thomas Pornin, author of BearSSL library.
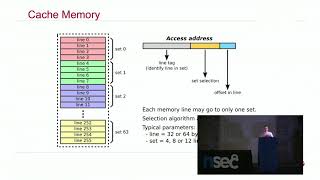
Non-Crypto Constant-Time Coding
Explore cache attacks, SGX technology, and tools for writing constant-time code to protect confidential data from side-channel vulnerabilities in various computing contexts.
Logic Against Sneak Obfuscated Malware
Explore SMT solvers for binary analysis and code deobfuscation in IT security. Learn practical applications, limitations, and solutions for enhancing malware analysis capabilities.
Python and Machine Learning
Explore machine learning for malware categorization using Python and scikit-learn. Learn to transform data, apply clustering algorithms, and generate YARA rules for effective malware hunting.
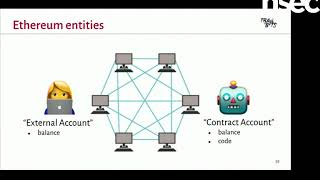
Binary Analysis, Meet the Blockchain
Explore symbolic execution for Ethereum smart contract analysis, addressing technical challenges and introducing Manticore, an open-source tool for enhancing contract security audits.
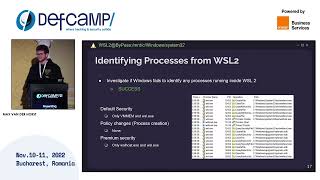
WSL 2 and Security - Productivity Booster or Achilles Heel
Explore WSL 2's security implications: productivity enhancer or potential vulnerability? Gain insights from cybersecurity experts on leveraging this technology safely in your development workflow.
Deanonymization of TOR HTTP Hidden Services
Explore techniques for deanonymizing TOR hidden services, presented by an Application Security Engineer. Gain insights into vulnerabilities and potential risks in anonymous web services.
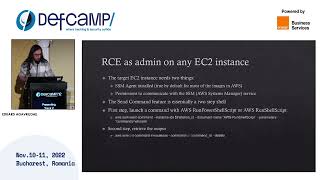
Cloud Configure Review - The New Internal Pentest at DefCamp
Explore cloud configuration review as a modern internal penetration testing approach, focusing on its importance, methodologies, and impact on cybersecurity strategies.
What Social Media Looks Like When You Can't See
Blind engineer Matt King shares insights on making social media accessible, exploring assistive technology's role in bridging the disability-accessibility gap online.
IoT Firmware Analysis
Explore IoT firmware analysis techniques with Bogdan Glazov, Senior Security Researcher. Learn about vulnerabilities, hacking methods, and cybersecurity strategies in the rapidly evolving IoT landscape.