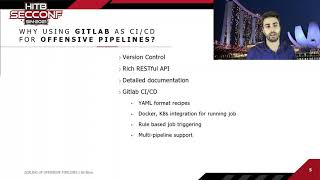
Scaling Up Offensive Pipelines
Innovative approach to offensive CI/CD pipelines for red and purple team operations, automating weaponization and evasion techniques using Infrastructure as Code and Kubernetes.
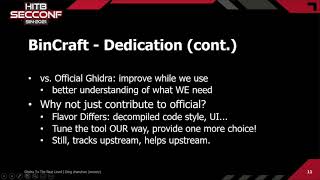
Taking Ghidra to the Next Level
Enhancing Ghidra: BinCraft's modernization efforts, improved decompilation, and integration of advanced techniques like GraalVM for a more powerful reverse engineering tool.

Is Attestation All We Need? Fooling Apple's AppAttest API
Exploración detallada de la API AppAttest de Apple, sus vulnerabilidades y limitaciones como solución anti-manipulación, con ejemplos de implementaciones débiles y escenarios de bypass.
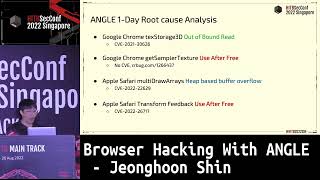
Browser Hacking With ANGLE
Explore browser hacking using ANGLE, covering WebGL basics, vulnerability analysis, and RCE exploitation in macOS. Learn about ANGLE architecture and specific CVEs in Chrome and Safari.
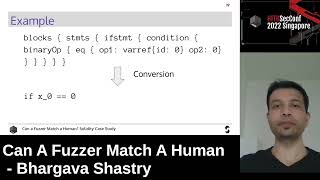
Can A Fuzzer Match A Human
Exploring advanced fuzzing techniques for Solidity compiler testing, focusing on optimizers and code generators to uncover security vulnerabilities in smart contract compilation.
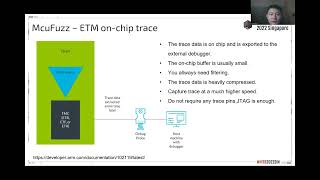
Fuzzing the MCU of Connected Vehicles for Security and Safety
Fuzzing techniques for MCU security in connected vehicles, using ARM ETM and code coverage-guided approach to enhance vulnerability detection and system robustness.
Going Passwordless
Explore passwordless authentication methods, including U2F, Credential Management, and magic links. Learn about their usability, security properties, and implementation challenges.
Sympathy for the Developer
Explore developer challenges and empathetic solutions in cybersecurity, fostering better collaboration between security teams and developers for enhanced software protection.
Modern Internet-Scale Network Reconnaissance - Underflow
Explore modern internet-scale network reconnaissance techniques, including data processing, platform capabilities, certificate transparency, cloud discovery, and domain fronting for enhanced cybersecurity insights.
DefCon DarkNet Badge Hardware and Software - An Introduction to Custom Badge Building
Explore custom badge building for DefCon DarkNet, covering hardware and software aspects. Learn techniques for creating unique, interactive electronic badges for hacker conferences.
Malware Automation
Explore advanced techniques for automating malware analysis, enhancing detection capabilities, and streamlining security processes with expert Christopher Elisan.
Attacking Drupal
Explore techniques for exploiting vulnerabilities in Drupal websites, focusing on common attack vectors and security weaknesses in this popular content management system.
Guardians of GitHub
Explore GitHub security practices and learn to protect your repositories from common vulnerabilities with insights from industry experts.

Solving for Somebody Else's Problem - Hacking Devs for Better Security
Explore strategies for improving security by understanding and addressing developers' challenges, fostering collaboration between security and development teams.
Pacu - Attack and Post-Exploitation in AWS
Explore AWS attack and post-exploitation techniques using Pacu, an open-source tool for penetration testing and security assessments in cloud environments.
iOS Runtime Hacking Crash Course
Dive into iOS runtime hacking techniques, exploring methods to manipulate and analyze iOS applications for security testing and reverse engineering purposes.
All Your Cloud Are Belong To Us - Hunting Compromise in Azure
Explore techniques for detecting and investigating compromises in Azure cloud environments, focusing on security best practices and threat hunting strategies.
The Effect of Constraints on the Number of Viable Permutations of Passwords
Explore the impact of password constraints on permutations and security through Monte Carlo simulations, analyzing character sets, length, and user behavior.
Give the Dog a Bone - Exploring OSINT Capabilities of Pen-testing Tools
Explore OSINT capabilities of pen-testing tools, focusing on security awareness, cloud migration, and new attack strategies. Learn about DNS, AWS logs, Nmap, and honeypots.
Burpsuite Team Collaborator - Enabling Collaborative App Testing
Explore collaborative app testing with Burpsuite Team Collaborator. Learn features, sharing capabilities, and see a live demo for enhanced security assessments and teamwork.
The Case for Software Bill of Materials
Explore the importance of Software Bill of Materials in cybersecurity, its implementation challenges, and potential benefits for software transparency and risk management.