Shifting Left- Raise Your Security Bar! - Guido Rajngewerc & Martin Cuesta - Ekoparty Security Conference - 2020
Integración de seguridad en el ciclo de desarrollo ágil: herramientas y estrategias para detectar vulnerabilidades temprano, empoderando a los desarrolladores como actores clave en la seguridad del producto.
IronPython... OMFG - Marcello Salvati - Hack in Paris - 2019
Explore dynamic .NET runtime access using Python, bypassing PowerShell restrictions for stealthy offensive operations in Windows environments.
10 Mio€ für Open Source - Jedes Jahr
Einblicke in die Struktur und Bedeutung von Open-Source-Projekten für die Sicherheit sowie Vorschlag eines öffentlichen Fonds zur finanziellen Förderung mit 10 Mio € jährlich zur Absicherung wichtiger Projekte.
Measuring Radioactivity Using Low-Cost Silicon Sensors
Learn to build a DIY particle physics detector using low-cost silicon sensors. Explore natural radioactivity, measure particle energy, and analyze data with Python in this hands-on introduction to modern particle physics.
Offensive XSLT - Nicolas Gregoire - Hack in Paris
Explore offensive XSLT techniques, uncovering vulnerabilities in applications using XSLT engines. Learn systematic review methods to identify high-impact security risks.
Why I Wrote My Own Rsync - Michael Stapelberg - Media.CCC.De
Explore the creation of a custom rsync implementation in Go, delving into rsync's inner workings, performance improvements, and integration with home networking projects.
Unwinnable Prizes on the Internet - Roland Meertens - RC3
Exposé sur les jeux en ligne truqués offrant des prix impossibles à gagner, révélant les techniques trompeuses utilisées pour collecter les adresses e-mail des utilisateurs.
Legislative Engineering - Design Privacy Laws, Don't Just Draft Them - USENIX Enigma Conference - 2017
Exploring software engineering techniques to improve technology legislation, focusing on component-based architecture and modeling to create more effective and consistent laws.
Reversing Web Applications
Explore web application reverse engineering techniques, from information gathering to active testing, to understand behavior, analyze code, and improve security assessments.
Brakeman & Jenkins - The Duo Detects Defects in Ruby on Rails Code
Explore static analysis tools for Ruby on Rails, focusing on Brakeman and Jenkins integration. Learn about security warnings, code updates, and best practices for detecting defects.
Million Browser Botnet
Explore how online advertising networks can be exploited to create massive browser botnets, enabling DDoS attacks, spam campaigns, and password cracking without leaving traces. Learn about the scalability and potential risks of this attack scenario.
Deserialization - What, How and Why Not
Explore insecure deserialization risks, vulnerabilities, and prevention techniques through code examples and live demos, focusing on Java but applicable to other languages.
A New Framework to Automate MSTG and MASVS in Your CI/CD Pipeline
Automate mobile app security testing using BDD and UI automation frameworks. Integrate OWASP MASVS/MSTG into CI/CD pipelines for faster, repeatable security checks at DevOps speed.
The Anatomy of a Secure Web Application in Java Using Spring Security and Apache Fortress
Practical guidance on implementing secure Java web applications using Spring Security and Apache Fortress. Covers authentication, authorization, and confidentiality controls with hands-on demos and code examples.
Exploiting Unknown Browsers and Objects
Discover hidden browser vulnerabilities with the Hackability Inspector, a new offensive toolkit for security researchers to explore and exploit unknown entities in embedded browsers.
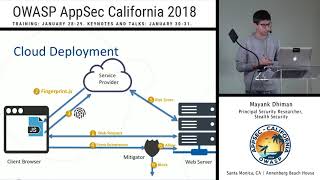
Breaking Fraud and Bot Detection Solutions
Demystifying browser fingerprinting and user behavior tracking in fraud detection, exploring vulnerabilities, and demonstrating proof-of-concept attacks against these defense mechanisms.
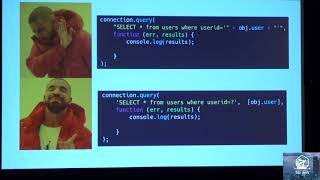
OWASP Top 10 for JavaScript Developers
Explore JavaScript vulnerabilities in OWASP Top 10, covering client and server-side issues with focus on modern frameworks and NodeJS. Learn prevention techniques for secure web development.
Temporal - Code-Origin Policy - Towards a Formal User Privacy Protection for the Web
Explore a novel approach to web privacy protection through code-origin monitoring, offering customizable user safeguards and formal assurance mechanisms for JavaScript execution.
Temporal - Bot or Human? Detecting Malicious Bots with Machine Learning in 2021
Explore advanced techniques for detecting sophisticated bots using machine learning, combining server-side and client-side signals, and leveraging supervised and unsupervised approaches for maximum accuracy.
Topological Defects and Phase Transitions
Explore topological defects in 2D systems, their role in phase transitions, and experimental verifications in superfluids, superconductors, and crystals.

Unlocking the Power of ML for Your JavaScript Applications with TensorFlow.js
Explore TensorFlow.js for ML in JavaScript: learn to integrate, retrain models, and leverage ML beyond browsers. Includes demos of virtual makeup try-on and radiology diagnostics.