MITMf - Bringing Man In The Middle Attacks to the 21st Century
Explore modern Man-In-The-Middle attack techniques with MITMf, a Python framework combining new and old methods for efficient, extendable, and reliable network security testing.
Exploits with Scratch
Explore network exploitation using Scratch programming language, extending its capabilities to create exploits and fuzz vulnerable services through custom TCP/IP function blocks.
ARM Assembly and Shellcode Basics - Workshop
Comprehensive workshop on ARM assembly and shellcode creation, covering basics, execve() shell, and reverse shell. Includes hands-on practice with QEMU emulator and Raspberry Pi hardware.
Koadic C3 - Windows COM Command & Control Framework
Explore Koadic C3, a Windows COM-based command and control framework. Learn about VBScript, threading, HTML applications, and lateral movement techniques for advanced penetration testing.
Breaking Smart - Bank Statements
Explore techniques for breaking encrypted bank statements, including JavaScript and RC4 analysis, with practical demonstrations and insights on difficulty levels and methodologies.
BYOI Payloads - Fusing the Power of .NET With a Scripting Language of Your Choosing
Explore .NET assembly generation, embedding scripting languages, and advanced techniques for creating versatile payloads in this cybersecurity-focused talk on BYOI (Bring Your Own Interpreter).
BaRMIe - Poking Java’s Back Door
Explore Java's Remote Method Invocation security vulnerabilities, enumeration techniques, and exploitation tools with BaRMIe. Learn about common mistakes and potential solutions in RMI implementations.
Penetration Testing Considered Harmful
Critique of penetration testing practices, exploring limitations, misconceptions, and potential harm in cybersecurity. Proposes alternative approaches and challenges industry norms.
Search Engine Deoptimization with Gootloader
Explore search engine deoptimization techniques used by Gootloader malware, including compromised WordPress sites, malicious SEO, and process hollowing. Learn about server infrastructure and potential countermeasures.
Modern Pentest Tricks for Faster, Wider, Greater Engagements
Discover cutting-edge pentest techniques for efficient and comprehensive engagements, focusing on CSV tools, parallel execution, and innovative applications.
Prototype Pollution Attacks in NodeJS Applications
Explore prototype pollution attacks in NodeJS, including APIs vulnerable to pollution, potential impacts, and defensive strategies. Learn from real-world examples and security research findings.
Don't Kill My Cat
Evade antivirus and security layers with polyglot files and assembly obfuscation. Learn to create undetectable payloads for penetration testing using a versatile tool.
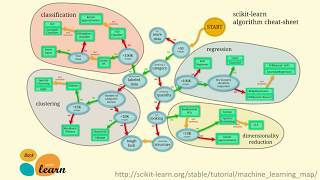
Data Science Tools and Techniques for the Blue Team
Explore data science tools and techniques for cybersecurity, including statistical analysis and machine learning, to enhance threat detection and defense capabilities in large-scale corporate environments.
Practical Uses of Program Analysis - Automatic Exploit Generation
Explore automatic exploit generation through program analysis techniques, including instrumentation and symbolic execution, with practical demonstrations and tool insights.
OO RE with HexraysCodeXplorer
Explore object-oriented reverse engineering techniques for modern malware analysis, focusing on C++ code reconstruction and tools like HexRaysCodeXplorer for tackling complex malware frameworks.
Hopping on the CAN Bus
Learn to hack your car's CAN bus using an open-source toolkit. Explore CAN basics, attack methods, hardware/software tools, diagnostic protocols, and security implications for modern vehicles.
SSO Wars - The Token Menace
Explore SSO vulnerabilities, focusing on JWT and SAML tokens. Learn attack vectors, signature verification issues, and real-world implications for frameworks like WCF and SharePoint.
Lessons Learned by the WordPress Security Team
Insights from WordPress Security Team's journey: challenges, strategies, and lessons in safeguarding open-source software and educating users on cybersecurity best practices.
The Chrome Crusader
Explore Chrome extension vulnerabilities, security considerations, and potential exploits. Learn about architecture, headers, and isolation techniques for safer browsing experiences.
CheckPlease - Payload-Agnostic Sandbox Detection
Explore payload-agnostic sandbox detection techniques, including sleep evasion, encryption, and user activity analysis. Learn to build profiles and implement various detection methods across languages.
Building Secure ASP.NET Core MVC Applications
Explore ASP.NET Core MVC security features, including XSS and CSRF protection. Learn to build robust web applications with modular architecture and cross-platform compatibility.