
Spring Modulith – Spring for the Architecturally Curious Developer
Explore architectural patterns and tools for building maintainable Spring applications, focusing on code organization, bean relationships, and domain events to enhance modularity and testability.
Adventures in Building a CAN Bus Sniffer
Explore the process of building a CAN Bus Sniffer, from prototyping to assembly. Learn hardware development tips, documentation preparation, and small-batch ordering for your first device.
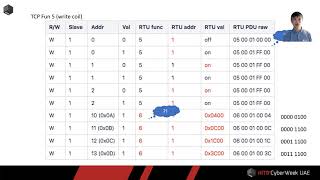
Industrial Protocol Gateways - A Deep-Dive of Moxa MGate 5105-MB-EIP
Explore industrial protocol gateways, focusing on Moxa MGate 5105-MB-EIP. Learn about vulnerabilities, customizing tools, and intercepting configurations in this hands-on deep dive into OT network security.
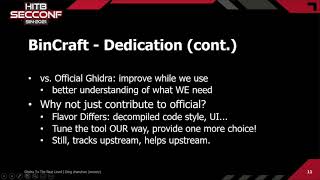
Taking Ghidra to the Next Level
Enhancing Ghidra: BinCraft's modernization efforts, improved decompilation, and integration of advanced techniques like GraalVM for a more powerful reverse engineering tool.
Browser Hacking With ANGLE
Explore browser hacking using ANGLE, covering WebGL basics, vulnerability analysis, and RCE exploitation in macOS. Learn about ANGLE architecture and specific CVEs in Chrome and Safari.
Modern Internet-Scale Network Reconnaissance - Underflow
Explore modern internet-scale network reconnaissance techniques, including data processing, platform capabilities, certificate transparency, cloud discovery, and domain fronting for enhanced cybersecurity insights.
The Effect of Constraints on the Number of Viable Permutations of Passwords
Explore the impact of password constraints on permutations and security through Monte Carlo simulations, analyzing character sets, length, and user behavior.
Baited Canaries - Monitoring Attackers With Active Beacons
Explore active beacons for monitoring attackers, including JavaScript canaries, DNS prefetch, and Google Drive auditing techniques to enhance cybersecurity defenses.
Securing and Trusting Third-Party Javascripts in Your Web App
Learn techniques to secure and trust third-party JavaScript in web applications, enhancing overall security and mitigating potential vulnerabilities.
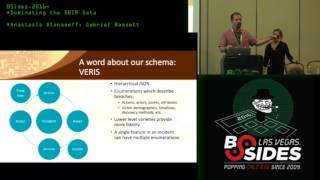
Dominating the DBIR Data
Explore data analysis techniques for cybersecurity incidents, covering data collection, processing, and validation. Learn to generate meaningful statistics and uncover novel findings in security datasets.
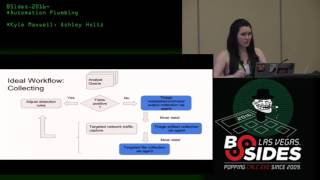
Automation Plumbing
Explore efficient automation workflows for cybersecurity, covering detection, aggregation, processing, and plumbing solutions using tools like Python, Elastic Search, Splunk, and Log Stash.
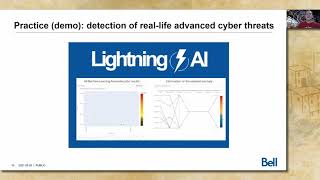
Data Science Way to Deal With Advanced Threats
Explore data science methods for advanced threat detection in SOCs, combining unsupervised and supervised learning to reduce false positives and streamline anomaly triage using ML and interactive visualizations.
dRuby Security Internals
Comprehensive analysis of dRuby's security vulnerabilities, exploring its API, internals, and wire protocol. Demonstrates novel exploitation techniques and discusses efforts to harden dRuby against identified issues.
How to Harden Your Electron App
Learn techniques to enhance security in Electron apps, focusing on threat modeling, separation of concerns, and best practices. Discover insights from building a secure password manager using this framework.
Web Application Firewall Workshop
Hands-on workshop exploring Web Application Firewall bypass techniques, including encoding, SQL injection, protocol switching, and syntax alternatives. Practical exercises with in-depth explanations for each method.
Modern Reconnaissance Phase by APT - Protection Layer
Evolving APT reconnaissance techniques using malicious documents and watering hole attacks. Detailed analysis of obfuscation methods, scripting languages, and mitigation strategies for enhanced cybersecurity.
The New Wave of Deserialization Bugs
Explore deserialization vulnerabilities in Java, PHP, and Python. Learn to identify and mitigate risks in enterprise applications using practical examples and tools.
M33tfinder
Discover M33tfinder: a tool for identifying vulnerable web applications. Learn offensive security techniques from an experienced researcher in this informative conference talk.
Non-Crypto Constant-Time Coding
Explore cache attacks, SGX technology, and tools for writing constant-time code to protect confidential data from side-channel vulnerabilities in various computing contexts.
Python and Machine Learning
Explore machine learning for malware categorization using Python and scikit-learn. Learn to transform data, apply clustering algorithms, and generate YARA rules for effective malware hunting.
An Open-Source Machine-Code Decompiler
Explore RetDec, an open-source machine-code decompiler for analyzing binary applications. Learn about its components, applications in reverse engineering, and real-world examples demonstrated by Avast developers.