How to Learn and Teach Hacking
Explore hacking techniques, competitions, and effective teaching methods for cybersecurity skills. Learn problem-based approaches and gain insights into CTF challenges and binary exploitation.
Preventing Common Security Mistakes in the MEAN Stack - AppSec EU 2017
Learn to secure Angular applications by understanding common threats and implementing effective defenses. Covers script-based attacks, session management, CSRF, and more for robust client-side security.
Combining Security Risks of Native and Web Development in Hybrid Apps - AppSec EU 2017
Explore security risks in hybrid app development, combining native and web technologies. Learn defensive programming and testing strategies for secure cross-platform mobile applications.
Securing Single Page Applications - Design Considerations and Pitfalls
Explore security pitfalls in Single Page Applications and learn mitigation strategies. Covers stateless design, JSON handling, caching, local storage, and resource sharing, with practical demos and key takeaways.
Automated Gadget Chain Discovery for Deserialization Vulnerability Remediation
Explore automated discovery of Java deserialization gadget chains for vulnerability assessment and prioritized remediation, with insights on a new FOSS toolkit for evaluating security risks.
Securing C Code That Seems to Work Fine
Explore strategies for securing C codebases in high-performance environments, balancing best practices with startup culture. Learn from real-world successes and failures in implementing application security controls.
Remediating XSS in GitHub Open Source Projects - Lessons Learned
Insights on scaling XSS remediation across GitHub open source projects, focusing on risk reduction, adding security controls, and automating code modification for diverse applications.
Dangerous Optimizations and the Loss of Causality in C and C++ Programming
Explore compiler optimizations in C/C++ that can lead to software vulnerabilities. Learn about mitigation strategies and the importance of maintaining causality in code.
SPArring with the Security of Single Page Applications
Explore security challenges in Single Page Applications with insights on automating detection and mitigation strategies for modern web development vulnerabilities.
Modern XSS Defense Strategies - Frameworks, CSP, and Sanitization
Explore modern XSS defense strategies, including JavaScript frameworks, CSP deployment, HTML sanitization, and design considerations for building secure web applications against evolving threats.
User Groups: The Gateway to Apache
Discover strategies to leverage user groups for promoting open source ecosystems, engaging communities, and fostering active participation in software development.
Talking TUF: Securing Software Distribution
Explore The Update Framework (TUF) for securing software update systems. Learn how to integrate this flexible security framework to protect against vulnerabilities and enhance software distribution safety.
OWASP Glue Tool: Security Automation Made Easier
Learn about OWASP Glue Tool, a Ruby gem for security automation that coordinates multiple analysis tools and generates reports, simplifying the process of integrating security into development workflows.
SPArring with the Security of Single Page Applications - MMA Hacker Training
Explore security challenges in Single Page Applications through an MMA analogy. Learn about SPA frameworks, REST APIs, WebSockets, and interconnectivity to become a "Mixed Multilayer Application Hacker".
Building Secure Cloud-Native Applications with Spring Boot and Spring
Learn to build secure cloud-native applications using Spring Boot and Spring, focusing on best practices and techniques for robust, scalable, and protected software development.
Benchmarking Application Security Across Industries
Insights from 200,000+ application assessments reveal industry-specific software security trends, vulnerabilities, and best practices. Benchmark your AppSec program against peers for improved security outcomes.
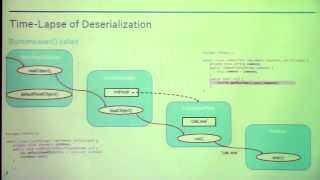
Marshalling Pickles - How Deserializing Objects Can Ruin Your Day
Explore vulnerabilities in object serialization across languages, learn exploitation techniques for code execution, and discover protective strategies against deserialization attacks.
Security Testing Windows Store Apps
Explore security testing for Windows Store Apps, focusing on HTML/JavaScript development, architecture, and potential vulnerabilities in this emerging application model.
Hybrid Analysis Mapping - Making Security and Development Tools Play Nice Together
Explore techniques for integrating security testing and development tools, improving collaboration between testers and developers for more effective application security and code quality.
Insecure Expectations - Testing for Common Security Issues in Rails Applications
Explore hands-on examples of security testing in Rails, learn about common vulnerabilities, and discover a new open-source tool for simplified security test writing. Gain practical skills to enhance your application's security.
Dynamic Source-Sink Analysis for Java Applications - From the Ground Up
Dynamic source-sink analysis for Java applications to detect security vulnerabilities, aimed at developers for use during development, not production. Demonstrates live detection of issues like log manipulation.