Lateral Movement and Privilege Escalation in GCP - Compromise Organizations without Dropping an Implant
Explore techniques for identity compromise, privilege escalation, and lateral movement in Google Cloud. Learn about GCP's unique security model and default permissions, with demonstrations and tool releases.
GPU Security Exposed
Explore GPU security vulnerabilities, including shared memory risks and privilege escalation issues, with insights on protecting popular devices from potential exploits.
7 Sins of ATM Protection Against Logical Attacks
Comprehensive exploration of ATM security vulnerabilities, covering kiosk mode bypass, privilege escalation, software flaws, network security, and device management. Insights for enhancing ATM protection.
Windows Operating System Archaeology - Casey Smith and Matt Nelson
Explore Windows OS archaeology, focusing on Component Object Model, persistence techniques, and evasion methods for enhanced system understanding and security awareness.
New Shiny in Metasploit Framework
Explore Metasploit Framework updates: new commands, modules, and features for various platforms. Learn about privilege escalation, persistence, and reverse operations.
SQL Server Hacking on Scale Using PowerShell
Explore SQL Server hacking techniques using PowerShell, covering server discovery, login access testing, privilege escalation, and post-exploitation strategies for enhanced security awareness.
From Logic to Memory - Winning the Solitaire in Reparse Points
Explore advanced Windows file redirection vulnerabilities, bypassing mitigations with novel exploit techniques. Learn about reparse points, logic flaws, and memory corruption in system services.
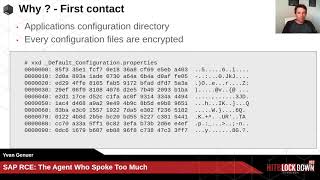
SAP RCE - The Agent Who Spoke Too Much
Explore SAP vulnerabilities: authentication bypass, OS command injection, and privilege escalation. Learn to decrypt sensitive files, manipulate security reports, and implement protective measures.
Exploiting Directory Permissions on macOS
Explore macOS directory permission vulnerabilities, from arbitrary overwrites to privilege escalation. Learn techniques to control file contents and understand the intricacies of macOS security.
Dreamboot - A UEFI Bootkit
Exploración detallada de la arquitectura UEFI y desarrollo de un bootkit para Windows 8 x64, analizando riesgos de seguridad y demostrando payloads maliciosos como escalada de privilegios y bypass de autenticación.
So You Think You Can Secure Your Cloud - Red Team Engagements in GCP
Comprehensive guide to adversary simulations in GCP, covering initial access, persistence, privilege escalation, C2 using Google products, and data exfiltration techniques.
Threat Hunting - Using MITRE ATT&CK Against Carbanak Malware
Explore threat hunting using MITRE ATT&CK framework against Carbanak malware, covering tactics, techniques, and procedures for effective cybersecurity defense and mitigation strategies.
Crashing Your Way to Medium-IL - Exploiting the PDB Parser for Privilege Escalation
Discover vulnerabilities in Windows PDB parser, learn exploitation techniques for privilege escalation, and explore the intricacies of memory corruption in DbgHelp.dll.
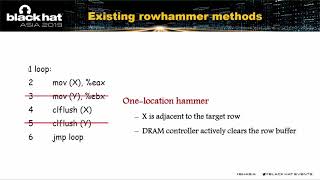
Winter is Coming Back - Defeating the Most Advanced Rowhammer Defenses to Gain Root and Kernel Privileges
A novel exploit breaking advanced rowhammer defenses, allowing unprivileged applications to gain root and kernel privileges. Stealthier and more efficient than existing exploits, this talk presents key steps and implications.
Explosion - The Hidden Mines in the Android ION Driver
Uncover vulnerabilities in Android's ION driver, explore root causes, and learn how to achieve privilege escalation. Gain insights into preventing similar security issues in the Android ecosystem.
Unix Domain Socket - A Hidden Door Leading to Privilege Escalation in the Android Ecosystem
Explore Unix domain socket vulnerabilities in Android, revealing potential privilege escalation risks and security implications for third-party applications and vendor implementations.
Typhoon Mangkhut - One-click Remote Universal Root Formed with Two Vulnerabilities
Exploit chain for remote Android root using Chrome and Binder vulnerabilities. Demonstrates bypassing security mitigations to achieve one-click root access on modern Pixel devices.
Continuous Intrusion - Why CI Tools Are An Attacker's Best Friends
Explore how CI tools can be exploited for attacks, including command execution, credential theft, and privilege escalation, with live demonstrations on popular open-source and proprietary platforms.
Social Engineering the Windows Kernel - Finding and Exploiting Token Handling Vulnerabilities
Explore Windows kernel token handling vulnerabilities, learn to identify and exploit them for privilege escalation, and understand patterns for conducting security reviews.
The Memory Sinkhole - Unleashing An X86 Design Flaw Allowing Universal Privilege Escalation
Unveiling a critical x86 design flaw allowing privilege escalation, exploring forgotten backdoors, and demonstrating how to exploit vulnerabilities in processor architecture.
Attacking Hypervisors Using Firmware and Hardware
Explore vulnerabilities in hypervisors through firmware and hardware emulation, demonstrating attacks and their impacts. Learn about firmware rootkits and new testing modules for hypervisor security.