Steel Mountain Walkthrough - Manual Windows Exploitation
Gain initial foothold and elevate privileges on Windows target by exploiting Unquoted Service Paths manually and with Metasploit. Learn practical techniques for Windows penetration testing.

Windows Privilege Escalation Tutorial for Beginners
Learn techniques for Windows privilege escalation, including local enumeration, exploit suggestion tools, token impersonation, hash dumping, and pass-the-hash attacks to gain elevated system access.
Attacking and Defending Supply Chains - How We Got Admin in Your Cloud
Explore software supply chain vulnerabilities leading to secrets exfiltration and privilege escalation, with best practices for securing reference architectures and production environments.
The Print Spooler Bug that Wasn't in the Print Spooler
Explore a unique Windows vulnerability discovery, from initial bug report to full exploit chain, with insights on Microsoft's patch process and security implications.
The Hidden Risk in Undocumented API Behavior
Explore undocumented Win32 API risks affecting AV and EDR vendors. Learn how overlooked behaviors can lead to security vulnerabilities and gain insights on mitigating these hidden threats.
Surprising Ways to Escalate Privileges in Entra ID
Explore common pitfalls and privilege escalation techniques in Entra ID. Learn to identify, prevent, and monitor security risks through practical demonstrations and expert insights.
Detecting Credential Abuse - Core Concepts and Challenges
Explore detection strategies for credential abuse, including core concepts, patterns, and challenges. Learn to identify suspicious activity and protect systems from unauthorized access.
SystemUI as EvilPiP - Hijacking Attacks on Modern Mobile Devices
Reveals new Android attack surface 'PiP', exploiting vulnerabilities to bypass security measures and perform stealthy hijacking attacks on modern devices without permissions or user awareness.
BOLABuster: Harnessing LLMs for Automating BOLA Detection
Harnessing LLMs to automate BOLA detection in APIs and web applications, reducing requests by 99% while uncovering critical vulnerabilities and submitting multiple CVEs.
Undocumented Windows Hash Leak Vulnerability
Uncover an undocumented Windows feature that leaks valuable hashes, enabling faster privilege escalation and domain admin access. Learn this simple yet powerful technique from experienced IT security specialists.
Privilege Escalation from Medium to High Integrity Level in Windows
Unveiling a Windows design flaw allowing privilege escalation from Medium to High integrity level, demonstrating a 100% reliable exploit on the latest Windows versions.
Windows Agentless C2 - Abusing the MDM Client Stack
Unveils innovative research on exploiting Windows MDM stack for agentless C2 systems. Explores vulnerabilities, custom C2 server creation, and remote device control techniques, inspiring new defensive strategies.
Attacking Windows Device Drivers: Almost Escaping the Sandbox
Explore techniques for attacking Windows device drivers and potential sandbox escape methods in this advanced security analysis presentation.
Practical Exploitation of Registry Vulnerabilities in the Windows Kernel
Explore practical exploitation techniques for Windows kernel registry vulnerabilities, enhancing your understanding of system security and potential attack vectors.
Breaching AWS Through Shadow Resources - Critical Vulnerabilities and Security Implications
Uncover critical AWS vulnerabilities and security insights through real-world examples of shadow resource exploitation, featuring detection methods, privilege escalation techniques, and best practices for cloud security.
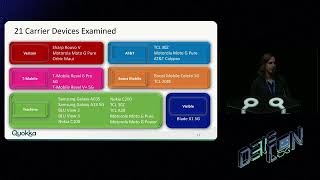
Security Vulnerabilities in Prepaid Android Smartphones - A Comprehensive Analysis
Uncover critical security vulnerabilities in prepaid Android smartphones through detailed analysis of 32 devices, revealing system-level flaws and privilege escalation risks in pre-loaded software.
Hunting for Amazon Cognito Security Misconfigurations
Explore Amazon Cognito security misconfigurations, including unauthorized access, authentication bypass, and privilege escalation. Learn detection techniques and developer recommendations.
Automatic Detection of Inadequate Authorization Checks in Web Applications
Automatic detection of missing authorization checks in web apps using static analysis. Explores techniques, real-world applications, and provides remediation suggestions for developers.
Infrastructure as Remote Code Execution: How to Abuse Terraform to Elevate Access
Explore security risks in Terraform, including privilege escalation and data exfiltration. Live demos showcase attack scenarios and provide recommendations for securing implementations.
A Methodical Approach to Privilege Escalation in AWS
Explore methodical AWS privilege escalation techniques with Senior Penetration Tester Eduard Agavriloae. Learn advanced cybersecurity strategies for identifying and exploiting vulnerabilities in cloud environments.
Attacking Debug Modules in the Android Ecosystem
Explore security vulnerabilities in Android debug modules, focusing on vendor-specific implementations. Learn about attack surfaces, real-world cases, and mitigation strategies for Android ecosystem security.