Controlling the Source - Abusing Source Code Management Systems
Explore vulnerabilities in Source Code Management systems, including reconnaissance, user role manipulation, and repository takeover. Learn attack scenarios and defensive strategies for GitHub, GitLab, and Bitbucket.

How to Be an Ethical Hacker in 2025 - A Comprehensive Guide to Cybersecurity Skills
Master the path to ethical hacking with comprehensive guidance on foundational IT skills, networking, Linux, programming, and advanced security concepts, including web applications and wireless hacking techniques.
Analyzing and Executing ADCS Attack Paths with BloodHound
Discover how to identify, analyze, and execute ADCS attack paths using BloodHound, while learning practical remediation strategies for defending against PKI-based privilege escalation in Active Directory environments.
Secure Containers - Do Reduction Strategies Fix Your Nightmares?
Explore container security challenges and reduction strategies to enhance your Docker environment's protection against vulnerabilities and potential threats.
Physical Attacks Against Smartphones: Android Security Vulnerabilities and Exploits
Discover physical attack vulnerabilities in Android smartphones, from Recovery mode exploits using SD cards to USB stack weaknesses in secondary bootloaders for achieving root access and code execution.
Breaking Microsoft Teams and SharePoint Through Migration APIs
Uncover critical security vulnerabilities in Microsoft SharePoint Online's migration APIs and learn how threat actors can exploit these features to compromise Microsoft 365 services and Azure Active Directory.
Spooky Authentication at a Distance - Post-exploitation Techniques for Windows Environments
Discover innovative post-exploitation techniques for proxying Windows authentication protocols remotely, enabling user impersonation and domain control without elevated privileges.
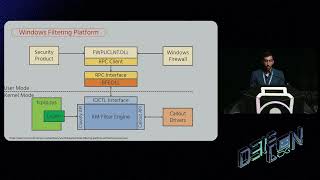
Abusing Windows Filtering Platform for Privilege Escalation - Undetected Attack Techniques
Discover an innovative Windows privilege escalation technique that exploits the Windows Filtering Platform, enabling stealthy system-level access through network traffic manipulation and kernel component abuse.
Breaking BMC: The Forgotten Key to the Kingdom - Security Vulnerabilities in Baseboard Management Controllers
Dive into the security vulnerabilities of Baseboard Management Controllers (BMC), exploring exploit chains and firmware implants in NVIDIA hardware with AMI MegaRAC BMC implementation.
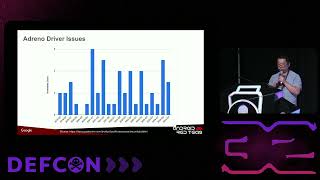
The Way to Android Root: Exploiting Smartphone GPU
Dive into advanced Android security research exploring Qualcomm Adreno GPU vulnerabilities, exploitation techniques, and kernel-level attacks to achieve root access, with practical mitigation strategies.
Exploiting Bluetooth Vulnerabilities: From Car Systems to Bank Account Security
Discover how to identify and exploit Bluetooth vulnerabilities in modern vehicles and flight systems, using BlueToolkit framework for testing, with practical tips and new attack vectors for security research.
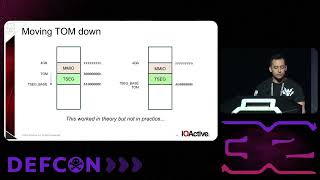
AMD Sinkclose - Universal Ring2 Privilege Escalation in System Management Mode
Delve into AMD processor security vulnerabilities, exploring System Management Mode (SMM), CPU design flaws, and the methodology behind ring-2 privilege escalation exploits.
Manipulating Shim and Office Infrastructure for Code Injection and Privilege Escalation
Delve into advanced Windows exploitation techniques, focusing on stealthy shim manipulation and Office infrastructure vulnerabilities for code injection and privilege escalation attacks.
Don't Let Your Permissions Be Hijacked - Preventing Permission Exploitation in SQL Server
Discover techniques to prevent malicious users from exploiting power user permissions through permission hijacking, ensuring robust database security.
How to Fuzz Your Way to Android Universal Root: Attacking Android Binder
Entdecken Sie Techniken zur Ausnutzung von Android Binder-Schwachstellen für Root-Zugriff durch Fuzzing-Methoden und Sicherheitsanalyse.
Infrastructure as Remote Code Execution: How to Abuse Terraform to Elevate Access
Explore security risks of Terraform, demonstrating exploitation techniques for privilege escalation and unauthorized access. Learn practical recommendations for securing cloud infrastructure deployments.
Infrastructure as Remote Code Execution: How to Abuse Terraform
Explore security risks in Terraform, including privilege escalation and data exfiltration. Learn attack scenarios and practical recommendations for securing cloud infrastructure deployments.
LinkDoor - A Hidden Attack Surface in the Android Netlink Kernel Modules
Explore Netlink vulnerabilities in Android kernel modules, uncovering security threats and exploitation techniques. Learn to analyze and mitigate risks in this overlooked attack surface.
Argo CD and GitOps Security: Exploiting Redis Vulnerability in Kubernetes Clusters
Unveiling a critical vulnerability in Argo CD, exposing Kubernetes clusters to privilege escalation attacks. Learn about the exploit, its impact, and essential mitigation strategies for GitOps security.
Windows EventLog Persistence Techniques for Red Team Operations
Explore Windows environment exploitation techniques, including bypassing constrained language, XML file abuse, and EventLog persistence, with a focus on red team operations and defense strategies.
Misconfiguration Manager - Overlooked and Overprivileged
Explore overlooked security risks in Configuration Manager, focusing on overprivileged settings and potential vulnerabilities. Learn to identify and mitigate these threats in enterprise environments.