A Series of Unfortunate Events - Where Malware Meets Murphy
Exploring a real-world ransomware incident, its challenges, and unexpected failures in security infrastructure and recovery processes. Learn valuable lessons for better incident preparedness.
Ask the Expert - Linux and PowerShell on Azure
Gain insights from Linux and PowerShell experts on Azure, covering recent announcements, best practices, and practical implementation strategies for optimizing your cloud infrastructure.
Ask the Expert - Linux and PowerShell on Azure
Gain insights on Linux and PowerShell on Azure from product experts. Learn about recent announcements, latest news, and best practices for optimizing costs and maximizing value with Azure IaaS.
Powershell Is Dead - Epic Learnings
Explore advanced PowerShell techniques, EDR evasion, and the evolving landscape of Windows endpoint security. Gain insights into offensive and defensive strategies for red teaming and threat emulation.
Return From The Underworld - The Future Of Red Team Kerberos
Explore Kerberos authentication, its vulnerabilities, and future developments in red team security through practical demonstrations and in-depth analysis.
Modern Evasion Techniques
Explore modern evasion techniques for cybersecurity, including Metasploit tips, email controls, Apache ModRewrite, and PowerShell, with practical demonstrations and expert insights.
Tracing Adversaries - Detecting Attacks with ETW
Explore advanced threat detection using ETW, covering process tracking, PowerShell monitoring, and file I/O analysis for enhanced cybersecurity defenses.
Rapid Incident Response with PowerShell
Learn essential PowerShell techniques for rapid incident response, focusing on preparation, identification, and containment strategies to effectively handle cyber attacks like NotPetya.
Attacking Azure Environments with PowerShell
Learn to exploit Azure environments using PowerShell, covering data dumping, modules, and various services. Gain insights into escalation techniques and practical demonstrations.
Detecting WMI Exploitation
Learn techniques to detect and prevent WMI exploitation, covering tools, processes, and best practices for enhanced Windows security and threat hunting.
Introducing DeepBlueCLI v2 Now Available in PowerShell and Python
Explore DeepBlueCLI v2's enhanced features for Windows malware detection, including PowerShell and Python implementations, regex improvements, and automated whitelisting techniques.
Subverting Trust in Windows - A Case Study of the How and Why of Engaging in Security Research
Explore Windows security research through a case study on subverting trust, covering dynamic analysis, code signatures, and PowerShell, with insights on validating trust and lessons learned.
Windows Event Logs - Zero to Hero
Comprehensive guide to leveraging Windows Event Logs for security monitoring, from basic concepts to advanced techniques for threat detection and incident response.
Weaponizing Splunk - Using Blue Team Tools for Evil
Explore how Splunk, a popular security tool, can be exploited for malicious purposes. Learn about vulnerabilities, attack surfaces, and practical demonstrations of potential threats.
Coding Secure Code - Best Practices, Advice for Writing Secure Code
Discover best practices for writing secure code, focusing on business-driven approaches, understanding your model, and integrating security seamlessly into development processes.
Lessons from Applying MITRE ATT&CK in the Wild
Experts discuss practical applications of MITRE ATT&CK framework, sharing insights on improving cybersecurity operations, leveraging adversary knowledge, and enhancing organizational defense strategies.
The Seven Most Dangerous New Attack Techniques, and What's Coming Next
Explore cutting-edge cyber threats, their mechanisms, and defense strategies. Learn about PowerShell attacks, Android vulnerabilities, and industrial control system risks from leading security experts.
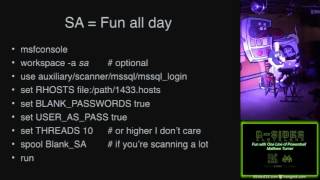
Fun with One Line of Powershell
Explore creative PowerShell one-liners for security testing, including USB controls, macros, and vulnerability scanning. Learn practical tips and techniques for ethical hacking.
Owning MS Outlook with PowerShell
Master PowerShell for Outlook: data mining, Exchange rules, persistence techniques, and dynamic triggers. Enhance productivity and automate tasks with advanced scripting.
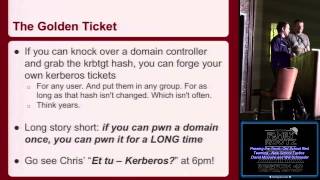
Passing the Torch - Old School Red Teaming - New School Tactics
Explore red teaming tactics, from traditional user hunting to modern PowerShell techniques, covering domain trusts, escalation, pivoting, and persistence in Windows environments.
Powershell and You - Using Microsoft's Post Exploitation Language
Explore PowerShell's potential for cybersecurity, from basic cmdlets to advanced scripting techniques. Gain insights into its use in hacking, post-exploitation, and incident response.