A Starters Guide to Pentesting with OWASP
Learn essential web security concepts, OWASP Top 10 vulnerabilities, and practical pentesting techniques to enhance your cybersecurity skills and protect web applications effectively.
Pentesting vs Bug Bounty - Approaches and Methodologies
Explore the differences between bug bounty hunting and penetration testing methodologies, comparing approaches, impacts, and scoping techniques.
How I Hacked 55 Banks and Cryptocurrency Exchanges - LevelUpX Series 3
Alissa Knight reveals tactics used to breach 55 financial institutions, offering insights into vulnerabilities in FinTech apps and APIs. Learn from a veteran hacker's experience in cybersecurity.
Cybersecurity in Education with Softdocs
Explore Softdocs' approach to safeguarding sensitive educational data through advanced cybersecurity measures, including penetration testing and bug bounty programs with Bugcrowd.
Critical Security Issues and Trends for 2017
Explore critical security trends with industry experts, covering IoT vulnerabilities, crowdsourced testing, AI impacts, and evolving threats to prepare for the cybersecurity landscape of 2017.
Hacking, Recon, and Breaking Into Cybersecurity - A Conversation with Lilly
Insightful interview with @seclilc on her cybersecurity journey, covering hacking, reconnaissance, tools, work-life balance, and overcoming challenges in the field.
Creating Wordlists for Hacking, Pentesting & Bug Bounty Hunting Using Seclists, Bigquery, and More
Learn to create effective wordlists for ethical hacking using tools like Seclists and Bigquery. Enhance your penetration testing and bug bounty hunting skills with expert techniques.
Your Guide to Burp Suite - Setup and Usage in 30 Minutes
Learn to set up and effectively use Burp Suite for web security testing in under 30 minutes, covering essential features and functionalities.
Recon Sunday with Top HackerOne Paid Hackers - Dawgyg, Mayonaise, and cdl
Live hacking event featuring top-paid hackers Dawgyg, Mayonaise, and cdl discussing reconnaissance techniques and strategies for bug bounty hunting on HackerOne's platform.
VirSecCon 2020 - Cybersecurity Conference on Bug Bounty, Mobile, Web, and Reconnaissance
Comprehensive cybersecurity conference featuring expert talks on bug bounty, mobile security, web hacking, and reconnaissance. Gain insights from industry leaders and enhance your ethical hacking skills.
Pentesting, Bug Escalation, and Career Insights - Interview with Codingo
Insightful discussion on pentesting, bug escalation, OSCP certification, and industry experiences, offering valuable insights for aspiring and seasoned cybersecurity professionals.
OSCP, Deserialization Bugs, Shodan Tips, and Becoming an MVH - Interview with SMSecurity
Insightful discussion on OSCP certification, deserialization vulnerabilities, Shodan techniques, and achieving Most Valuable Hacker status, offering valuable insights for aspiring cybersecurity professionals.
Hacking Uber, Working at Synack, and the 120 Reports in 120 Days Challenge
Insightful discussion on ethical hacking experiences, including Uber vulnerabilities, Synack employment, and a unique 120-day bug bounty challenge. Valuable insights for aspiring cybersecurity professionals.
Recon Methodology for Consistent High-Value Bug Bounties - Interview with Th3G3nt3lman
Discover effective recon methodologies for high-value bug bounties. Learn from @Th3G3nt3lman's experience in GitHub reconnaissance, tool usage, and collaboration strategies for successful hacking.
Setting Up Ubuntu for Pentest and Bug Bounty Automation
Learn to set up an Ubuntu environment for efficient penetration testing and bug bounty automation, covering droplet creation, aliases, and folder structure.
Developing crtndstry - A Tool for Finding Root Subdomains - Live Coding and Explanation
Live coding session demonstrating the creation of crtndstry, a tool for discovering root subdomains. Gain insights into the developer's thought process and learn practical cybersecurity techniques.
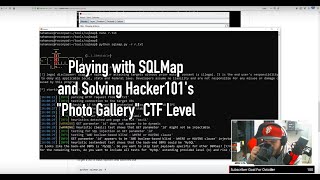
SQL Injection Techniques - SQLMap and Hacker101's Photo Gallery CTF
Explore SQL injection techniques using SQLMap and tackle Hacker101's "Photo Gallery" CTF challenge to enhance your ethical hacking skills and web security knowledge.
Using BurpSuite's Intruder for Bug Hunting and CTF Challenges
Learn to use BurpSuite's Intruder for bug hunting and solving CTF challenges, focusing on IDOR, XSS, and LFI/RCE vulnerabilities.
Live Recon on Rockstar Games - Vulnerability Testing Methodology
zseano demonstrates vulnerability testing methodologies on Rockstar Games, showcasing tools like Burp Suite and techniques for identifying XSS and open redirects in this live recon session.
Recon Methodology Using SecurityTrails, FDNS, Whoxy, and More
Explore codingo_'s unique recon methodology for ethical hacking, featuring tools like SecurityTrails, FDNS, and Whoxy to enhance your cybersecurity skills and bug bounty hunting techniques.
Live Recon and Distributed Recon Automation Using Axiom
Explore live recon and distributed recon automation using Axiom with @pry0cc. Learn advanced techniques for efficient and effective bug bounty hunting and cybersecurity research.