Beyond XP Cmdshell - Owning the Empire through SQL Server
Explore advanced SQL Server exploitation techniques, from disabling audit controls to leveraging machine learning, with insights on future research and Empire modules.
Extending Burp
Explore techniques for enhancing Burp Suite's functionality through extensions, improving web application security testing capabilities and efficiency.
Metasploit Townhall
Explore Metasploit's latest developments, including Railgun, packet encryption, and REST API, with insights from experts on scalability, automation, and new database models.
Common Assessment Mistakes Pen Testers and Clients Should Avoid
Explore common pitfalls in penetration testing and client assessments, learning strategies to enhance security evaluations and avoid critical mistakes.
A Better Tool for Hunting Default Creds - Zach Grace
Explore an improved tool for hunting default credentials, featuring demos, explanations, and insights into fingerprinting techniques and Docker integration.
Red Team Yourself - Thomas Richards
Learn to emulate adversaries, conduct comprehensive security assessments, and build an effective in-house red team. Explore reconnaissance, attack planning, and post-exploitation techniques for robust cybersecurity.
Hillbilly Storytime - Pentest Fails
Entertaining tales of penetration testing mishaps and lessons learned, offering valuable insights for cybersecurity professionals and aspiring ethical hackers.
Adding Simulated Users to Your Pentesting Lab with PowerShell
Learn to enhance your pentesting lab by creating simulated users with PowerShell, improving realism and complexity for more effective security testing and analysis.
Adding Pentest Sauce to Your Vulnerability Management Recipe
Enhance vulnerability management with pentesting techniques. Learn to identify weak spots, understand attacker perspectives, and implement effective security measures beyond basic scanning.
How to Test a Security Awareness Program - Matt Perry
Learn effective methods for evaluating and improving security awareness programs, covering digital footprints, physical security, social engineering, and best practices for organizational cybersecurity culture.
Hillbilly Storytime - Pentest Fails
Humorous and insightful talk on penetration testing failures, offering valuable lessons and takeaways for security professionals through real-world examples and stories.
Evaluating Injection Attack Tools Through Quasi Natural Experimentation
Explore the effectiveness of injection attack tools through experimental evaluation, gaining insights into cybersecurity vulnerabilities and defense strategies.
Adding Simulated Users to Your Pentesting Lab with PowerShell
Learn to enhance your pentesting lab by creating simulated users with PowerShell, improving realism and effectiveness in security testing environments.
Prowling Better Penetration Testing
Explore advanced penetration testing techniques, focusing on network monitoring, encryption, and control systems to enhance cybersecurity strategies and identify vulnerabilities.
Hacking Identity - A Pen Tester's Guide to IAM - Jerod Brennen
Comprehensive guide to identity and access management security, covering attack surfaces, pen testing processes, and best practices for securing user lifecycles and admin privileges.
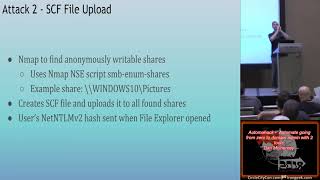
Automahack - Automate Going from Zero to Domain Admin with 2 Tools
Automate domain admin access using MITM6 and Responder. Learn NTLM relay, SMB signing, and various attack techniques for efficient network penetration and privilege escalation.
Operator - The Well Rounded Hacker
Explore the concept of becoming a well-rounded hacker, focusing on diverse skills and perspectives to enhance cybersecurity expertise and adaptability in the ever-evolving digital landscape.
Code Execution with JDK Scripting Tools Nashorn Javascript Engine
Explore JDK scripting tools and Nashorn Javascript Engine for code execution, including advantages, detection methods, and prevention strategies.
Evolving the Teaching of Pen Testing in Higher Ed
Explore evolving approaches to teaching penetration testing in higher education, addressing challenges and proposing strategic solutions for effective curriculum development.
Hacking Identity - A Pen Tester's Guide to IAM
Explore identity and access management vulnerabilities through a pen tester's perspective. Learn OSINT, password spraying, social engineering, and strategies to enhance IAM security.
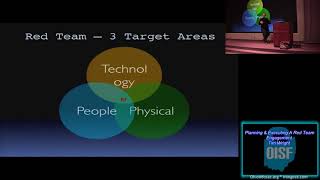
Planning & Executing a Red Team Engagement
Comprehensive guide to planning and executing effective red team engagements, covering strategies, methodologies, and best practices for simulating real-world cyber attacks.