Beyond OWASP Top 10 by Aaron Hnatiw - Hack in Paris - 2017
Explore 5 dangerous web vulnerabilities beyond OWASP Top 10, covering exploits and mitigations for both developers and pentesters to enhance application security.
Offensive Nature - Winn Schwartau, Georgia Weidman, Mario Heiderich Panel - Hack in Paris
Explore cybersecurity challenges with experts discussing international cyber law, counterattacks, and the future of digital threats in this thought-provoking panel.
Pen Testing for Humans
Learn essential penetration testing techniques, focusing on human vulnerabilities and social engineering in cybersecurity. Explore real-world scenarios and strategies to strengthen organizational security.
Practical Physical Security Advice for the Modern Enterprise
Practical advice on improving physical security, covering common weaknesses, bypass techniques, vulnerability mapping, and cost-effective solutions for modern enterprises.
A Physical Security Plan for Implementing ISO 27002
Explore physical security implementation for ISO 27002, covering human resources, asset management, and access control. Learn from real-world examples and gain insights on testing, remediation, and continuous improvement.
An Introduction to ZAP - The OWASP Zed Attack Proxy
Learn to use ZAP, an open-source web application security scanner. Explore features like active scanning, fuzzing, and brute force attacks to enhance your penetration testing skills.
Breaking Into Red Teaming
Explore essential skills, objectives, and methodologies for successful Red Team operations, covering physical access, cloud infrastructure, and effective communication strategies.
No More Monkey Business - Quality Assurance in Penetration Testing
Explore quality assurance in penetration testing, addressing declining standards and providing guidance for improving security assessment practices and maintaining excellence in the field.
Penetration Testing - The Other Stuff
Explore tools and tips for effective penetration testing, from data collection to reporting, with insights on organization, documentation, and disaster recovery.
Httpillage - Calling All Nodes
Explore distributed HTTP-based attacks using Httpillage, a tool for multi-node penetration testing. Learn to enhance impact demonstration and overcome limitations of single-host security assessments.
Pose a Threat - How Perceptual Analysis Helps Bug Hunters
Innovative techniques for efficient bug hunting using perceptual analysis, serverless infrastructure, and machine learning to identify security vulnerabilities at scale.
A New Framework to Automate MSTG and MASVS in Your CI/CD Pipeline
Automate mobile app security testing using BDD and UI automation frameworks. Integrate OWASP MASVS/MSTG into CI/CD pipelines for faster, repeatable security checks at DevOps speed.
Optimize Your Pentesters Time
Optimize pentesting resources with Hunter, an open-source tool grading websites for low-risk security issues. Learn how eBay saved 10-15% of their pentesting budget and improved efficiency.
Being Powerful While Powerless - Elevating Security By Leading Without Authority
Learn strategies for elevating security without formal authority, including technical approaches and cultural tactics to influence stakeholders and drive positive change in organizational security practices.
Building & Hacking Modern iOS Apps
Explore iOS app security from both developer and hacker perspectives, covering secure development practices, vulnerability assessments, and insights into Apple's latest security features.
Testing and Hacking APIs
Learn techniques for testing and exploiting API vulnerabilities, including understanding implementation, detecting weak points, and conducting effective penetration tests on modern applications.
OWASP Standard Classification - Achieving Security by Shifting Left in Agile
Integrating security into Agile development through persona-based stories, prioritization, and testing strategies to create more secure web applications and shift security left in SDLC.
Intelligence Led Penetration Testing
Explore intelligence-led penetration testing using threat intel and OSINT to create bespoke, realistic assessments that mimic real-world attack techniques and toolkits.
Penetration Testing Must Die
Explore the limitations and challenges of penetration testing in cybersecurity, discussing its effectiveness, terminology issues, and potential alternatives for improving security assessments.
Pushing Left - How We're All Doing It Wrong
Explore how shifting security left in development can lead to unexpected wins, improved processes, and better collaboration between security teams and developers.
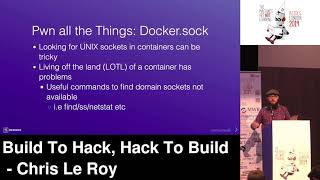
Build to Hack, Hack to Build
Explore container exploitation and security in DevOps with BOtB tool. Learn to identify, exploit, and remediate vulnerabilities in Docker and LXC environments before production releases.