OWASP Web Security Testing Guide
Comprehensive guide for web security testing, covering methodologies and best practices to identify vulnerabilities and enhance application security.
How the Latest MASVS and MSTG Specs Enhance Mobile Penetration Testing
Explore mobile security challenges, attack surfaces, and best practices using OWASP guidelines. Learn to leverage tools and frameworks for effective mobile app security testing and policy development.
OWASP Security Shepherd - Mobile and Web Security Awareness and Education
Explore web and mobile app security risks through interactive lessons and challenges. Improve penetration testing skills and understand vulnerabilities using OWASP Security Shepherd's comprehensive platform.
Smart Storage Scanning for Mobile Apps - Attacks and Exploits
Explore mobile app security vulnerabilities, focusing on local storage attacks. Learn automated scanning techniques for Android and iOS, with live demonstrations and defense strategies.
OWASP ZAP Advanced Features for Web Application Security Testing
Explore advanced features of OWASP ZAP for web application security testing, including handling non-standard apps, client-side testing, fuzzing, scripting, and more with expert Simon Bennetts.
HTTP Time Bandit - Identifying Web Application Performance Bottlenecks
Explore web application vulnerabilities and efficient DOS/DDOS attack techniques using HTTP Time Bandit tool. Learn to identify resource-consuming pages for improved security or targeted attacks.
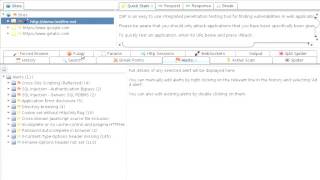
Introduction to OWASP's Zed Attack Proxy - Web Application Penetration Testing
Explore OWASP's free, open-source penetration testing tool for web applications. Learn its features, installation, and usage through hands-on demonstrations and testing of insecure web apps.
OWASP Zed Attack Proxy: Latest Features and Developments - Lecture
Explore web application security with OWASP's Zed Attack Proxy. Learn key features, including Plug-n-Hack and Zest scripting, suitable for both novice and experienced penetration testers.
Falco and Atomic Red Team - Real-time Threat Detection in Cloud-Native Systems
Explore real-time threat detection in cloud-native systems using Falco and Atomic Red Team, enhancing security practices for modern infrastructure.
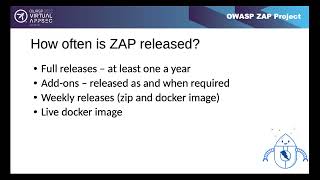
OWASP ZAP Project: Introduction to Web Application Security Testing
Learn to use OWASP ZAP, a powerful open-source web application security scanner. Discover its features, capabilities, and best practices for identifying vulnerabilities in web applications.
Azure Vulnerability Testbed (AzGOAT) - Understanding and Hardening Azure Security
Explore Azure security vulnerabilities and defenses with AzGOAT, a lab environment for understanding attack surfaces, designing secure solutions, and minimizing threats in Azure environments.
Exploiting Web Messaging Implementations
Uncover vulnerabilities in cross-document messaging, learn common developer mistakes, and explore open-source tools for identifying post messaging security issues in web applications.
Insiders Guide to Mobile AppSec with Latest OWASP MASVS
Explore mobile app security with OWASP MASVS, covering data storage, network calls, authentication, coding, and reverse engineering. Gain insights from real-world experience and latest tools for effective mobile pentesting.
Squeezing the Last Drop Out of OWASP Juice Shop
Explore advanced hacking techniques and security challenges in this hands-on session with OWASP Juice Shop, led by its creator Bjoern Kimminich.
OWASP Juice Shop Project
Explore web application security with OWASP's intentionally vulnerable Juice Shop, learning about common vulnerabilities and how to exploit and defend against them.
Unveiling the Vulnerabilities: Hacking Cloud Native Apps and Discovering the Silver Lining
Explore cloud-native app vulnerabilities, including OAuth, storage services, and API-based microservices. Learn to identify, exploit, and mitigate risks through penetration testing and automated tools.
Main App Methodology for Bug Bounty Hunting
Discover a unique and effective methodology for app testing, learning from an expert's successful approach to enhance your own skills and techniques.
Falco and Atomic Red Team - Real-Time Threat Detection in Cloud Native Systems
Explore real-time threat detection in cloud-native systems using Falco and Atomic Red Team. Learn effective strategies for enhancing security and identifying potential vulnerabilities in modern infrastructures.
Web Security: Broken by Default?
Explore web security challenges, focusing on browser vulnerabilities and emerging standards to address these issues. Learn how developers can enhance application security beyond code fixes.
ASVS Testing: Understanding Access Requirements for Verification
Analyzing ASVS requirements to identify necessary access for accurate verification, aiding test case generation and helping companies understand the effort required for comprehensive security assessments.
Security Testing for Smart Metering Infrastructure - BSidesLV 2014
Explore security testing for smart metering infrastructure, covering AMI hacks, test scopes, standards, and strategies for effective implementation and risk mitigation.