How Hacking Works - Web Edition - NDC Oslo 2024
Explore web exploitation techniques and tools to enhance software security through gamified environments. Learn to think like a hacker for safer development.
Writing Powerful Penetration Testing Reports
Learn strategies for crafting effective penetration testing reports, including key components, proof-of-concept creation, and common pitfalls to avoid. Enhance your ability to deliver impactful security assessments.
Protecting Small Businesses from Cyber Attacks - Strategies and Real-World Scenarios
Explore attacker strategies, real-world scenarios, and cost-effective measures to protect small businesses from cyber threats. Learn to engage employees through gamification for enhanced security.
Offensive Security Awareness: Understanding Assessment Types and Methodologies
Demystify offensive security techniques, tools, and assessment types. Gain insights into vulnerability management strategies and learn to choose the right approach for your organization's security needs.
Mapping Your External Attack Surface: Illuminating Hidden Vulnerabilities
Illuminate hidden assets and vulnerabilities in your external attack surface using powerful reconnaissance tools. Proactively defend your digital perimeter and stay ahead of potential threats.
You Wouldn't Hack a Car? A Pentester's Approach to Embedded Security on Automotive ECUs
Explore automotive security testing of electronic control units, focusing on embedded systems in modern vehicles and their vulnerabilities. Learn pentesting approaches for ECU analysis and defense mechanisms.
Metasploit Auxiliary Modules Demo - TCP Port Scanners, FTP Login, SSH Version, and SSH Login
Explore Metasploit Auxiliary modules, including TCP port scanners, FTP login, and SSH tools. Learn practical techniques for network reconnaissance and vulnerability assessment.

Ethical Hacking: Using Metasploit to Crack Passwords
Explore ethical password cracking using Metasploit. Learn to create dictionaries, launch attacks, and understand techniques for responsible penetration testing and system security enhancement.
Metasploit Framework Introduction - Modules in Metasploit
Explore Metasploit's core modules: Auxiliary, Exploit, Payload, Encoder, Evasion, and Post-Exploitation. Learn their functions and applications in penetration testing.
Exploiting AI-Generated Code Vulnerabilities and Their Solutions
Discover vulnerabilities in AI-generated code and learn how to exploit and fix them. Gain insights into potential security risks and implement effective solutions using Snyk.
Developer Security Essentials
Discover how attackers exploit code vulnerabilities and learn to identify and fix complex security issues efficiently. Participate in a hands-on hacking session to address open source security problems.
Hacking Demos: Dangerous Lies and Asset Intelligence in IoT Security
Explore hacking demos, asset intelligence, and XIoT vulnerabilities. Learn about common attack types, see live industrial device hacks, and discover remediation strategies for enhanced cybersecurity.
Abusing Symbolic Links on Windows - A Link to the Past
Explore techniques for exploiting symbolic links on Windows systems, uncovering potential vulnerabilities and security risks in file system operations.
TryHackMe Ice - Walkthrough - Windows Privilege Escalation
Comprehensive walkthrough of Windows exploitation and post-exploitation techniques using TryHackMe's Ice challenge, covering essential skills for penetration testing and privilege escalation.
Windows Privilege Escalation - Token Impersonation With RoguePotato & PrintSpoofer
Elevate Windows privileges using access token impersonation techniques RoguePotato and PrintSpoofer. Learn practical steps for privilege escalation in penetration testing and cybersecurity.
Windows Privilege Escalation - Exploiting AutoRun Programs
Demonstrating how to identify and exploit AutoRun programs in Windows Registry for privilege escalation, with practical examples and tools like winPEAS.
Salesforce Object Recon - LevelUpX Series 1
Explore Salesforce Object Recon techniques with security researcher Kyle Benac. Learn valuable insights for enhancing your bug bounty and penetration testing skills in this informative presentation.
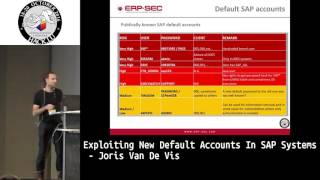
Exploiting New Default Accounts in SAP Systems
Explore SAP system vulnerabilities through new default accounts, focusing on platform security and practical exploitation techniques for enhanced protection.
Physical Intrusion - Access Uncontrolled
Explore techniques and strategies for physical security breaches, focusing on unauthorized access methods and countermeasures in various environments.
Unexpected Intrusion Testing Results in SAP Systems - Critical Vulnerabilities and Exploits
Unveiling critical vulnerabilities in SAP Start Service, from local to remote exploits. Explores memory corruption and OS command injection leading to root-level RCE, with live demo and recommendations.
macOS Red Teaming 101 - Corporate Scenarios and Vulnerability Exploitation
Exploración detallada de vulnerabilidades en macOS desde la perspectiva de un atacante interno, abordando explotación y medidas de protección para entornos corporativos.