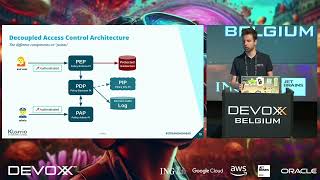
Decoupling Data Policy and Application Code with Open Policy Agent OPA
Explore Open Policy Agent (OPA) for decoupling data policies from application code, enhancing security and flexibility in software development.
Help! My Cluster Is On The Internet - Container Security Fundamentals
Explore container and Kubernetes security fundamentals, covering supply chain and runtime security. Learn practical strategies to protect clusters and prevent vulnerabilities using real-world examples and essential tools.
Episode IV - A New Network Service Mesh
Explore Network Service Mesh: a revolutionary approach to Cloud Native networking that simplifies complexity, enables multi-cloud connectivity, and integrates with SPIFFE and OPA for enhanced identity and policy support.
Open Policy Agent Introduction
Introduction to Open Policy Agent (OPA), a versatile policy engine for Kubernetes and cloud-native ecosystems. Learn about its features, use cases, and recent updates in OPA and OPA Gatekeeper.
Open Policy Agent Deep Dive
Explore Open Policy Agent's new features, integration capabilities, and use cases in cloud-native environments. Learn about partial evaluation and upcoming developments from project maintainers.
Managing Multi-Cluster - Multi-Tenant Kubernetes with GitOps
Modernize deployments using GitOps in multi-cluster/multi-tenant environments. Learn FluxCD implementation, CI tools integration, and best practices for consistent and secure Kubernetes management.
Introduction to Open Policy Agent
Learn about Open Policy Agent (OPA), a versatile policy engine for enforcing rules across various systems. Explore core features, integrations, and use cases in cloud-native environments.
No More Moats - Protecting Your Cloud Native Infrastructure with Zero Trust
Explore Zero Trust security for cloud native infrastructure using SPIFFE, SPIRE, and open-source tools. Learn practical architectures and implementation strategies from Fortune 500 examples.
Fortifying Microservice Security with SPIRE and OPA
Learn how to enhance microservice security using SPIRE for authentication and OPA for authorization. Discover scalable solutions for reliable service-to-service and end-user access control in complex environments.
Using Open Policy Agent to Meet Evolving Policy Requirements
Explore how Open Policy Agent enables rapid development and deployment of evolving security policies for Kubernetes platforms, meeting diverse compliance requirements across commercial and government environments.
Customizing OPA for a "Perfect Fit" Authorization Sidecar
Explore customizing Open Policy Agent (OPA) for enhanced authorization: high-performance gRPC API, Kafka decision logging, and OAuth2 Rego functions. Tailored solutions for improved security and integration.
Secure Policy Distribution With OPA
Explore secure policy distribution using OPA's signed bundles. Learn how to verify authenticity, prevent corruption, and reduce attack surfaces in policy enforcement systems.
DevOps All the Things - Creating a Pipeline to Validate Your OPA Policies
Learn to streamline OPA policy validation using unit, mock, and integration testing for Kubernetes clusters, featuring a live demo of applying changes to ephemeral clusters and deploying via GitOps.
Open Policy Agent Intro
Introduction to Open Policy Agent (OPA) and Gatekeeper: Learn about policy enforcement for cloud-native technologies, featuring demos and updates on latest features.
Enabling Autonomous Teams With Policy Enforcement at Yubico
Explore Yubico's approach to enabling autonomous teams through policy enforcement, leveraging Open Policy Agent for scalable, flexible, and performant solutions in Kubernetes environments.
Argo - Real Enterprise-Scale with Kubernetes
Explore enterprise-scale Kubernetes with Argo, covering continuous delivery, automated canary deployments, workflows, and security testing in this comprehensive overview.
Implementing Authorization
Explore implementing robust authorization systems using Open Policy Agent, decoupling from authentication for fine-grained control and easier maintenance in various software environments.
Access Policies for Hybrid Cloud Environments
Explore challenges and solutions for managing access policies across diverse systems in hybrid cloud environments, aiming for a secure and consistent experience.
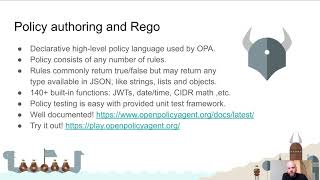
Cloud Native Policy Enforcement with Open Policy Agent
Explore Open Policy Agent for cloud-native policy enforcement, covering deployment options, Rego language, and Kubernetes integration.
Introduction to Open Policy Agent
Explore Open Policy Agent (OPA), a versatile policy engine for Kubernetes, microservices, CI/CD, and cloud. Learn about its features, integrations, and applications in cloud-native security.
AuthN and AuthZ at Cruise - Crawl, Walk, Run
Explore Cruise's journey in implementing authentication and authorization within Kubernetes clusters, from basic approaches to advanced solutions for zero trust security at scale.