Windows Red Team Exploitation Techniques - Luckystrike & PowerShell Empire
Explore Windows Red Team exploitation techniques for initial access, including creating malicious macro documents and setting up a C2 server with PowerShell Empire & Starkiller.
The Hack@DAC Story - Learnings from Organizing the World's Largest Hardware Hacking Competition
Explore insights from organizing Hack@DAC, the world's largest hardware hacking competition. Learn about unique aspects, value for the security community, and key takeaways for industry, academia, and researchers.
Information Security: An Ecology of Horrors and You Are the Solution - Keynote
Explore the ecology of information security, examining strategic force design, great power conflicts, and the evolving role of hackers in modern systems and deterrence.
Exploit Engineering: Attacking the Linux Kernel
Explore Linux kernel exploitation techniques, from attack surface mapping to vulnerability discovery and exploit development. Gain insights into advanced kernel exploitation methods and tools.
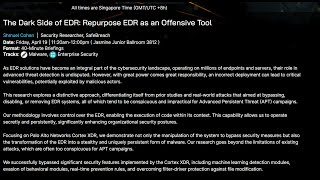
The Dark Side of EDR - Repurposing EDR as an Offensive Tool
Explore innovative attack vector transforming EDR into stealthy malware. Learn to bypass security features, exfiltrate data, and establish persistent control, focusing on Palo Alto Networks Cortex XDR.
Evasion Techniques for Red Team Engagements
Techniques for deploying code undetected during red team engagements, evading modern EDR solutions. Insights from an experienced red teamer on covert operations in complex environments.
Introduction to Red Teaming
Explore red teaming origins, roles, and key differences from penetration testing in offensive cybersecurity. Gain insights for beginners and experienced professionals alike.
Introduction to Software Defined Radio for Offensive and Defensive Operations
Overview of Software Defined Radio for security professionals, covering basics to advanced tactics for adversary emulation. Learn quick SDR operations and explore offensive and defensive applications.
How to Build a Secure Recon Network Using Tailscale
Build a secure recon network with Tailscale to protect your offensive tools, safeguard data, and enhance your bounty hunting capabilities.
Defense Through Offense: Microcontroller Security in Meta's First Generation of Smart Glasses
Explore microcontroller security in Meta's smart glasses, focusing on defense strategies through offensive techniques and real-world applications.
Offensive Security Awareness: Understanding Assessment Types and Methodologies
Demystify offensive security techniques, tools, and assessment types. Gain insights into vulnerability management strategies and learn to choose the right approach for your organization's security needs.
Command-Line Data-Wrangling for Security Professionals
Mastering command-line tools for efficient data manipulation in offensive security. Learn sorting, regex, grep, find, and JSON processing to enhance your hacking capabilities.
Cloud Hacking - Hacking Amazon AWS
Explore techniques for hacking Amazon AWS, focusing on offensive security and red team strategies. Learn about potential vulnerabilities and ethical hacking approaches in cloud environments.
Cloud Hacking - Common Attacks and Vulnerabilities
Explore common cloud vulnerabilities including SSRF, metadata endpoints, S3 permissions, and federation. Learn to identify and exploit these weaknesses in cloud environments.
Hunting for Amazon Cognito Security Misconfigurations
Explore Amazon Cognito security misconfigurations, including unauthorized access, authentication bypass, and privilege escalation. Learn detection techniques and developer recommendations.
Cloud Hacking - Malware Not Needed
Explore cloud hacking techniques without malware, covering state actors, exploitation methods, and initial foothold strategies for offensive security professionals.
Cloud Hacking- The Basics
Explore fundamental techniques for identifying and exploiting vulnerabilities in cloud infrastructure, enhancing your offensive security skills and understanding of cloud security risks.
PHP Filter Chains - How to Use Them
Explore PHP filter chains for web security, understanding their mechanisms and potential exploits. Learn practical techniques to enhance application defenses against vulnerabilities.
Taking Your DevOps Tooling to the Dark Side
Explore the dark side of DevOps tooling and its potential security implications in this thought-provoking conference presentation.
RFIDler: RFID Hacking and Security Analysis Tool
Explore RFID technology and security with Adam Laurie's presentation on RFIDler, covering vulnerabilities, hacking techniques, and practical demonstrations of RFID exploitation.
The DeFi Threat Model
Explore the security landscape of decentralized finance (DeFi) and learn about potential threats, vulnerabilities, and attack vectors in blockchain-based financial systems.