Securing an API Ecosystem with OAuth 2.0
Explore OAuth 2.0 implementation for robust API security in this comprehensive talk by Philippe De Ryck, covering best practices and ecosystem protection strategies.
ASP.NET Core 3 - IdentityServer4 - Implementing Sign-in Redirect with OIDC-Client.js - Episode 15
Implement sign-in redirect with oidc-client.js and integrate access tokens into axios headers for ASP.NET Core 3 and IdentityServer4 authentication.
ASP.NET Core, C#, IdentityServer4, and Nuxtjs - Client Authentication Implementation - Tricking Library Episode 29
Implementación del flujo de autenticación en cliente Nuxtjs usando oidc-client. Guía práctica para integrar autenticación segura en aplicaciones web modernas.
GPT-4 is Not Replacing Programmers - The Value Beyond Code Writing
Explore how GPT-4 complements programming skills, focusing on the broader aspects of software development beyond coding and its potential to enhance productivity.
Building a Single-Page Application with JHipster, Vue.js, and Okta
Learn to build modern web apps using JHipster, integrating Vue.js for the front-end, Spring Boot for the back-end, and Okta for secure authentication. Discover how to streamline development with this powerful combination.
Secure Your Microservices with Spring Security and OAuth
Learn to create a secure microservices architecture using Spring Boot 2.0, Spring Security, and OAuth 2.0 in this practical screencast.
Comparing Native Java REST API Frameworks - Spring Boot, Micronaut, Quarkus, and Helidon
Comprehensive comparison of popular Java REST frameworks: Spring Boot, Micronaut, Quarkus, and Helidon. Learn to build, secure, and optimize APIs using each framework, with performance insights and community metrics.
Better Testing with Spring Security Test
Learn to configure and mock Spring Security tests for OpenID Connect, JWT authentication, and OAuth 2.0 authorization with opaque tokens in this comprehensive screencast.
Protecting Your APIs with OAuth
Discover OAuth 2.0 for API security, learn common flows, explore token types, and understand best practices to protect your APIs effectively.
OAuth and OpenID Connect in Plain English
Comprehensive guide to OAuth 2.0 and OpenID Connect, explaining key concepts, flows, and best practices for secure authentication and authorization in web applications.
OAuth 2.0 - It's the Implementation, Stupid
Explore OAuth 2.0 implementation, covering key concepts, grant types, and security considerations for robust authentication and authorization in web applications.
Deploying Nomad on Google Cloud - Setting Up Web UI Access
Set up DNS, Global Load Balancer, and Identity-Aware Proxy to access Nomad's web UI on Google Cloud. Learn to inspect clusters, submit, and manage jobs via browser interface.
Federated Login CSRF
Explore federated login CSRF vulnerabilities in OpenID Connect and OAuth 2.0, examining attack scenarios, risks, and mitigation strategies for secure identity linking in web applications.
A Comprehensive Formal Security Analysis of OAuth 2.0
Comprehensive formal security analysis of OAuth 2.0, examining authorization, authentication, and session integrity properties, and discussing potential attacks and mitigations.
OAuth 2.0 Deconstructed
Comprehensive deconstruction of OAuth 2.0, exploring its intricacies, implementation strategies, and best practices for secure authentication in modern web applications.
Don't Lose Sleep, Secure Your REST
Learn to secure REST APIs using JOSE standards, including JWT, JWS, and JWE. Explore key concepts like cryptography, hierarchical auth, and request/response validation for robust API protection.
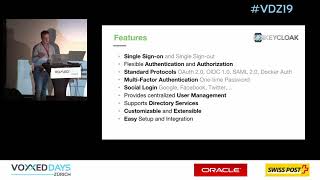
How to Secure Your Spring Apps with Keycloak
Comprehensive guide to implementing Keycloak for centralized authentication and authorization in Spring applications, covering core concepts, integration scenarios, and identity management infrastructure.

Securing Your APIs with OAuth 2.0
Learn to secure APIs using OAuth 2.0, covering JWT access tokens, scope design, and microservices architecture. Gain insights on authorization protocols, multi-factor auth, and backend service separation.
OAuth All the Things - What Is OAuth 2.0?
Comprehensive introduction to OAuth 2.0, covering various flows, use cases, and implementation details for developers building secure authentication systems.
How to Secure Your Spring Apps with Keycloak
Comprehensive guide to integrating Keycloak for robust authentication in Spring applications, covering core concepts, OAuth/OpenID Connect flows, and centralized identity management.
How to Leak a 100-Million-Node Social Graph in Just One Week
Exploración de vulnerabilidades en OAuth 2.0 para redes sociales, demostrando cómo la suplantación de aplicaciones puede llevar a la filtración masiva de datos de usuarios y gráficos sociales.