If 6,000 Mobile Malware Applications Could Talk - Analyzing Malware Behavior and Trends
Explore insights from analyzing 6,000 mobile malware apps, covering distribution, behavior, fingerprinting, and common characteristics. Learn about APK scanning and permission requests.
Adaptive Testing Methodology: Crowdsourced Testing for Customized Target Stack
Discover an efficient, customizable pentesting methodology that adapts to specific technology stacks and time constraints, improving consistency and effectiveness in vulnerability detection.
Why Using SMS in Authentication is Risky and Better Alternatives - AppSecUSA 2016
Explore limitations of SMS-based authentication and discover more secure alternatives using push notifications for improved user experience and enhanced security in two-factor authentication.
HTTPS and TLS Security Practices - Front Line Insights 2016
Comprehensive overview of modern HTTPS and TLS security practices, covering protocol vulnerabilities, certificate fundamentals, and best practices for implementing strong encryption in web services.
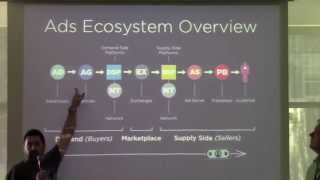
Modern Malvertising and Malware Web-Based Exploit Campaigns
Explore modern malvertising and web-based exploit campaigns, including top malware types, real-world attack breakdowns, and emerging threats in this technical presentation on cybersecurity.
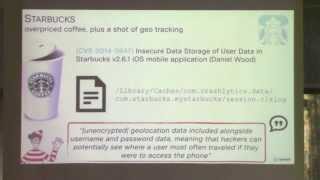
When Geo Goes Wrong - A Case Study of Geolocation Vulnerabilities in Mobile Apps
Exploring geolocation vulnerabilities in mobile apps, focusing on a dating app case study. Discusses common bugs, attack methods, and best practices for secure location-aware app development.
Everything You Need to Know About Certificate Pinning - AppSecEU 2016
Comprehensive guide to certificate pinning: implementation, benefits, and potential pitfalls. Essential knowledge for enhancing mobile app security and protecting against man-in-the-middle attacks.
Security Testing Windows Store Apps
Explore security testing for Windows Store Apps, focusing on HTML/JavaScript development, architecture, and potential vulnerabilities in this emerging application model.
OWASP Mobile Top Ten 2014 - The New Lack of Binary Protection Category
Explore the new OWASP Mobile Top Ten category: lack of binary protections. Learn about risks to mobile apps, their impact on the app economy, and strategies to mitigate these threats on iOS and Android platforms.
Getting a Handle on Mobile Security
Comprehensive overview of mobile security challenges and best practices, covering encryption, data protection, and platform-specific concerns for developers building secure mobile applications.
Security Management and Training - OWASP AppSec Europe 2014
Comprehensive security conference covering threat intelligence, JavaScript crypto, mobile/web security education, HTML5 security, CISO insights, PCI DSS, and Android malware analysis.
Mobile Security Track - AppSec Europe 2014
Explore cutting-edge mobile security topics at AppSecEU 2014, covering iOS and Android vulnerabilities, OWASP Mobile Top Ten, smart storage scanning, and practical defense strategies for app developers.
Building Secure Containers for Mobile Devices
Explore secure container solutions for BYOD environments, covering application wrapping, design challenges, iOS runtime analysis, and implementation best practices for mobile data protection.
PiOSoned POS - A Case Study in iOS-Based Mobile Point-of-Sale Security Flaws
Explore security vulnerabilities in iOS-based mobile point-of-sale systems, including coding mistakes, platform misunderstandings, and hardware weaknesses. Learn best practices for securing mobile POS applications.
Mobile Security Attacks - A Glimpse from the Trenches
Explore emerging mobile security threats, from physical to network and application levels, with real-world attack examples and insights from experts who uncovered iOS vulnerabilities.
AppSecUSA 2014 Builders Track - Friday Sessions
Explore key AppSec topics: mobile security, threat modeling, continuous security, and component vulnerabilities. Gain insights from industry experts to enhance your application security practices.
AppSecUSA 2014 - Breakers Track Sessions
Explore cutting-edge web and mobile security topics, including mobile attacks, use-after-free exploitation, static analysis, runtime manipulation, and top hacking techniques from AppSecUSA 2014.
AppSec is Eating Security
Explore the future of information security with Yahoo's CISO Alex Stamos as he discusses the evolving landscape of application security and its impact on the broader security field.
Top 10 Web Hacking Techniques of 2013 - OWASP AppSecUSA 2014
Explore the top 10 innovative web hacking techniques of 2013, including Mutation XSS, BREACH, and HTML5 attacks. Learn about cutting-edge security vulnerabilities and their implications for web applications.
OWASP Top 10 Mobile Risks: 2014 Reboot
Explore the updated 2014 OWASP Top 10 Mobile Risks, comparing changes since 2011, understanding new threats, and learning recommended fixes for iOS, Android, and Windows Phone platforms.
Android and iPhone Risks and Solutions
Explore mobile security risks and effective solutions for Android and iPhone devices, enhancing your understanding of smartphone vulnerabilities and protection strategies.