BlueSnarfing - The Risk From Digital Pickpockets
Explore digital pickpocketing risks and BlueSnarfing techniques in this cybersecurity presentation, uncovering vulnerabilities in Bluetooth-enabled devices.
Software Security
Explore mobile and web app security, including SSL/TLS, authentication, and cross-site scripting. Learn testing techniques and effective report writing for security assessments.
Bypassing 2Factor Auth with Android Trojans
Explore techniques for bypassing two-factor authentication using Android trojans, uncovering potential vulnerabilities in mobile security systems.
A Newbie's Talk On Mobile Dangers Through The Looking Glass
Explore vulnerabilities in rooted Android devices and potential attacks using Raspberry Pi and USB-OTG accessories. Discusses programmatic rooting, charging port risks, and past iOS vulnerabilities.
Abusing Over-The-Air Client Provisioning
Uncovers vulnerabilities in major phone brands' network settings, allowing attackers to manipulate user data. Demonstrates attack flows and discusses vendor mitigations for these security risks.
Understanding the Prevailing Security Vulnerabilities in TrustZone-Assisted TEE Systems
Comprehensive analysis of security vulnerabilities in TrustZone-assisted Trusted Execution Environments, exploring architecture issues, implementation bugs, and hardware flaws across popular TEE systems. Offers insights for improving TEE security.
Cloak & Dagger - From Two Permissions to Complete Control of the UI Feedback Loop
Unveiling Android vulnerabilities: combining permissions for stealthy UI control attacks, exploring security mechanisms, and discussing potential countermeasures and Android team responses.

ARMageddon - How Your Smartphone CPU Breaks Software-Level Security and Privacy
Explore smartphone CPU vulnerabilities that compromise security and privacy, revealing potential threats to sensitive data and personal information without requiring permissions.
Can You Trust Me Now? An Exploration Into the Mobile Threat Landscape
Comprehensive exploration of mobile security, examining hardware, software, and network components across platforms to uncover vulnerabilities and discuss protective measures for data and devices.
Vaccinating Android
Explore Android security, decompilation, and analysis techniques. Learn about APK tools, dynamic and static analyses, and hacking challenges in this comprehensive mobile security talk.
Tell Me Who You Are and I Will Tell You Your Lock Pattern
Explore Android lock pattern vulnerabilities, user behavior, and security implications through data analysis and visual complexity assessment.
Security Impact of High Resolution Smartphone Cameras
Explores security risks of high-res smartphone cameras, including keystroke capture via facial reflections and fingerprint extraction, with potential for authentication bypass and identity fraud. Proposes mitigation strategies.
Inaudible Sound as a Covert Channel in Mobile Devices
Explores ultrasonic and vibration-based covert channels in mobile devices for data exfiltration, bypassing security measures. Proposes solutions to regulate sound-based vulnerabilities in information flow control.
Dirty Stream Attack - Turning Android Share Targets Into Attack Vectors
Explore Android's intent system vulnerabilities, focusing on how file-sharing mechanisms can be exploited to target and attack applications, with insights on potential security risks and mitigation strategies.
OEMs Considered Harmful - Hello New 0Days
Explores zero-day vulnerabilities in OEM Android customizations, demonstrating how these modifications can undermine Google's security measures and affect millions of devices worldwide.
The State of Mobile Security
Exploración del panorama actual de la seguridad móvil, incluyendo amenazas recientes, técnicas de detección, investigación forense y la iniciativa FreeTheSandbox para mejorar el acceso y control de los usuarios sobre sus dispositivos.
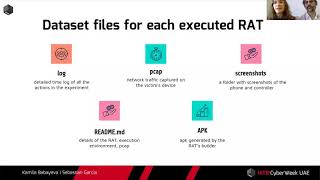
Android RATs Detection With a Machine Learning-Based Python IDS
Explore Android RATs detection using machine learning and Python IDS. Learn about dataset creation, Slips IDS implementation, and live demo of RAT activity detection in mobile device network traffic.
Viewer Discretion Advised - Decoding an iOS Vulnerability
Uncover a hidden iOS vulnerability in the video-decoder driver, exploitable from sandboxed processes. Learn techniques for finding and exploiting complex mobile security flaws in closed-source environments.
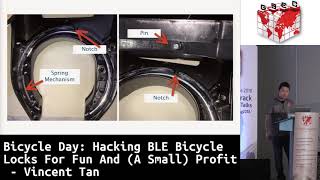
Hacking BLE Bicycle Locks for Fun and - A Small - Profit
Explore BLE bicycle lock hacking in ride-sharing economy. Learn to analyze mobile-lock communications, simplify BLE attacks using mobile phones and Frida, and break locks for free rides.
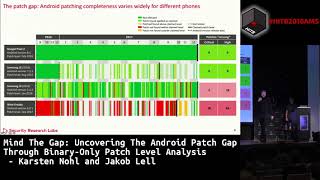
Uncovering the Android Patch Gap
Revealing Android security vulnerabilities: analysis of missing patches in vendor firmwares, enabling users to verify patch levels and improve overall protection.
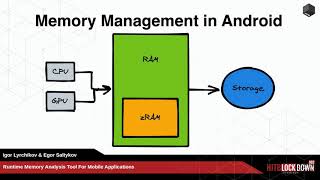
Runtime Memory Analysis Tool for Mobile Apps
Runtime memory analysis tool for mobile apps, automating common checks during penetration testing. Simplifies reverse engineering of obfuscated code for iOS and Android, tracking app behavior changes in real-time.