Bugs & Kisses - Spying On BlackBerry Users For Fun
Explore BlackBerry security vulnerabilities and potential spying techniques in this eye-opening presentation on mobile device privacy and data protection.
Hacking Fortune 2000th CEO's Mobile
Explore mobile security vulnerabilities and hacking techniques targeting high-profile executives, with insights on protecting sensitive corporate data on smartphones.
Strong Story to Tell - Top 10 Mistakes by Administrators about Remote Work
Discover top 10 remote work security mistakes, hacker perspectives, and effective solutions. Learn to protect corporate infrastructure from cyber threats in this insightful presentation by cybersecurity expert Paula Januszkiewicz.
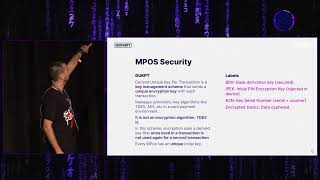
Turning My Phone into a Scamming Device
Exploración de vulnerabilidades en dispositivos de cobro móviles y métodos para convertir smartphones en herramientas de estafa, incluyendo inyección de datos y manipulación de tráfico. Se presentan casos reales y soluciones.
Messenger Hacking - Remotely Compromising an iPhone through iMessage
Detailed exploration of a remote iPhone exploit via iMessage, covering vulnerability analysis, exploitation techniques, and mitigation strategies for mobile OS and messenger security.
Mobile MFA Madness - Mobile Device Hygiene and MFA Integrity Challenges
Explore vulnerabilities in mobile authenticator apps and learn how poor device hygiene compromises MFA integrity. Includes live demonstration of exploiting these weaknesses.
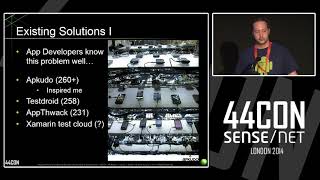
Researching Android Device Security with the Help of a Droid Army
Explore Android device security using a diverse cluster, addressing fragmentation challenges and enabling efficient vulnerability research and testing across multiple devices.
Integrating Mobile Devices into Your Penetration Testing Program - DefCamp 2015
Explore integrating mobile devices into penetration testing programs, covering security risks, attack vectors, and defensive strategies for corporate and personal devices.
Red Team Engagements and the Forgotten Risk of Mobile Devices - DefCamp - 2019
Explore red team engagements and mobile device risks in cybersecurity. Learn about mobile app vulnerabilities, penetration testing tools, and offensive instrumentation techniques for enhanced security awareness.
Modmob Tools - Home Made Tools to Test Mobile Devices and Monitor Networks
Explore homemade tools for testing mobile devices and monitoring networks, covering interception techniques, firmware analysis, and hardware auditing for enhanced security understanding.
Attack Vectors in Biometric Recognition Systems - Mobile Authentication Use Case, Blockchain, and More
Explore vulnerabilities in biometric recognition systems, including mobile authentication, spoofing techniques, and emerging technologies like blockchain, with insights on future developments and security challenges.
ECDSA Key Extraction from Mobile Devices via Nonintrusive Physical Side Channels
Explore physical side-channel attacks on ECDSA key extraction from mobile devices, covering analysis methods, results, equipment, and potential countermeasures.
iLock - Immediate and Automatic Locking of Mobile Devices against Data Theft
Innovative mobile device security system using acoustic sensing to automatically lock devices when users leave, preventing data theft and unauthorized access.
When CSI Meets Public WiFi - Inferring Your Mobile Phone Password via WiFi Signals
Explores WiFi signal-based mobile password inference, discussing attack scenarios, challenges, system design, and data processing methods for enhancing cybersecurity awareness.
Hey Google, Activate Spyware! - When Google Assistant Uses a Vulnerability as a Feature
Explore Android vulnerabilities allowing unauthorized camera control, revealing security flaws in Google Assistant and discussing implications for user privacy and smartphone security.
All Your SMS & Contacts Belong to ADUPS & Others
Uncover Android firmware vulnerabilities exposing user data to third parties without consent. Learn about ADUPS and other threats to mobile privacy and security.
Blink for Your Password, Blink Away Your Civil Rights?
Explore legal implications of biometric technology on civil rights, focusing on 4th and 5th Amendment protections. Learn design suggestions for mobile devices and tips for users.
Unearthing the TrustedCore - A Critical Review on Huawei’s Trusted Execution Environment
Unveils critical security flaws in Huawei's TrustedCore, exposing vulnerabilities in trusted execution environments and demonstrating weaknesses in hardware-backed cryptography on mobile devices.
Drammer - The Making Of
Exploración técnica del ataque Drammer, que aprovecha la vulnerabilidad Rowhammer en dispositivos Android sin permisos de usuario ni fallas de software. Detalla el proceso de desarrollo y los desafíos enfrentados.
Fingerprint-Jacking - Practical Fingerprint Authorization Hijacking in Android Apps
Practical exploration of fingerprint authorization vulnerabilities in Android apps, demonstrating attack techniques and suggesting mitigation strategies for developers.
Start Arbitrary Activity App Components as the System User Vulnerability Affecting Samsung Android
Vulnerability in Samsung Android allows zero-permission apps to execute arbitrary activities as system user, compromising device security across multiple Android versions.