QARK: Android App Exploit and Static Code Analysis Tool
Explore QARK, a comprehensive tool for Android app security analysis and exploitation. Learn how it combines static code analysis, vulnerability detection, and automatic exploit generation for developers and pentesters.
Automated Mobile Application Security Assessment with MobSF - AppSec EU 2016
Discover automated mobile app security assessment using MobSF. Learn techniques for identifying vulnerabilities and enhancing protection in mobile applications.
The ABCs of Source-Assisted Web Application Penetration Testing
Learn advanced web application penetration testing techniques using source code analysis for improved vulnerability detection and assessment.
Mobile Application Assessments By The Numbers - A Holistic View
Explore mobile app security through data-driven insights, examining vulnerabilities and best practices for comprehensive assessments in this OWASP presentation.
So, You Want To Use A WebView? - Security Considerations and Best Practices
Explore WebView security challenges, interfaces, testing methods, and threat models. Learn best practices for implementing secure WebViews in mobile applications.
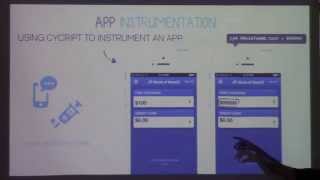
Uncovering OWASP's Mobile Risks in iOS Apps - AppSec California 2015
Explore iOS app vulnerabilities through reverse engineering techniques. Learn to extract, analyze, and identify common security risks in mobile applications using real-world examples.
Runtime Manipulation of Android and iOS Applications - Mobile Security Testing
Hands-on exploration of runtime manipulation and memory analysis techniques for Android and iOS apps, enhancing mobile security testing skills using tools like cycript and snoop-it.
Ten Secrets to Secure Mobile Applications
Discover key strategies for securing mobile apps, focusing on encryption, web service design, and user privacy. Learn to threat model and address top vulnerabilities using OWASP Mobile Top Ten framework.
iOS App Integrity: Enhancing Security with Encrypted Code Modules
Explore iOS app security vulnerabilities and learn advanced protection techniques like Encrypted Code Modules (ECM) to safeguard against static analysis, binary patching, and other common attacks.
Android App Protection Techniques: Obfuscation, Packing, and Protection - APPSEC Cali 2018
Explore Android app protection techniques, including obfuscation, packing, and protection. Learn to analyze and counter these methods to identify potential malware and enhance app security.
Fixing Mobile Application Security - OWASP Mobile Security Testing Guide
Introduction to OWASP Mobile Security Testing Guide and Mobile Application Security Verification Standard, addressing challenges in mobile app security testing and best practices for secure development.
Android Password Manager Security Analysis - AppSec EU 2017
Explore Android password manager security, common vulnerabilities, and best practices for protecting stored secrets. Learn about implementation pitfalls and design failures in popular apps.
Fixing Mobile Application Security - The OWASP Mobile Project
Explore OWASP's Mobile Application Verification Standard and Security Testing Guide, addressing key mobile app security challenges and best practices for secure data storage, communication, and API usage.
A Case for Integrity: JavaScript Apps Should Have It Too
Explore JavaScript app integrity with Pedro Fortuna, discussing cybersecurity challenges and innovative solutions for protecting client-side code in web applications.
Needle: Finding Issues within iOS Applications
Discover Needle, an open-source framework for streamlined iOS app security assessments. Learn about its modular architecture, capabilities, and how it simplifies vulnerability detection in iOS applications.
iGoat: A Self-Learning Tool for iOS App Security Testing
Learn iOS app security through hands-on exercises with iGoat, an open-source tool for developers and pentesters. Explore vulnerabilities, exploit techniques, and implement fixes in a safe environment.
Testing iOS Apps without Jailbreak - Penetration Testing Techniques
Learn techniques for penetration testing iOS apps without jailbreaking, including live demos on accessing protected resources on the latest iOS version. Ideal for pentesters facing jailbreak limitations.
OWASP Security Shepherd - Introduction and Overview
Learn to identify and mitigate web application vulnerabilities with OWASP Security Shepherd, an interactive platform for hands-on cybersecurity training and skill development.
Mobile DevSecOps: 5 Tips for Building Secure Apps Used by Millions
Discover 5 essential tips for implementing Mobile DevSecOps, drawing insights from large-scale app development experiences to enhance security and efficiency in your mobile projects.
How the Latest MASVS and MSTG Specs Enhance Mobile Penetration Testing
Explore mobile security challenges, attack surfaces, and best practices using OWASP guidelines. Learn to leverage tools and frameworks for effective mobile app security testing and policy development.
Smart Storage Scanning for Mobile Apps - Attacks and Exploits
Explore mobile app security vulnerabilities, focusing on local storage attacks. Learn automated scanning techniques for Android and iOS, with live demonstrations and defense strategies.