DTM Components - Shadow Keys to the ICS Kingdom
Explore vulnerabilities in industrial control system components, focusing on DTM technology used in critical industries. Learn about security flaws and their implications for field devices.
Network Attached Shell - N.A.S.ty Systems that Store Network Accessible Shells
Explore critical vulnerabilities in network storage devices, their impact on data security, and potential for network exploitation. Learn about attack techniques and implications for IT professionals and consumers.
WebKit Everywhere - Secure or Not?
Explore WebKit security, vulnerabilities, and exploitation techniques across platforms. Learn about security enhancements, mitigation strategies, and advanced exploit methods with real-world demos.
DPTrace - Dual Purpose Trace for Exploitability Analysis of Program Crashes
Explore advanced crash analysis techniques combining backward and forward taint propagation to enhance exploitability assessment and speed up vulnerability triage for security researchers and exploit writers.
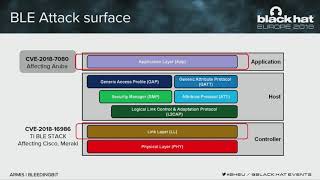
BLEEDINGBIT - Your APs Belong to Us
Explore zero-day vulnerabilities in BLE chips, allowing unauthenticated network penetration. Learn about BLEEDINGBIT, its impact on enterprise APs, and potential attack scenarios.
Network Attached Shell - N.A.S.ty Systems that Store Network Accessible Shells
Explore critical vulnerabilities in network storage devices, their impact on data security, and implications for network infrastructure. Learn about attack methods and the importance of robust security measures.
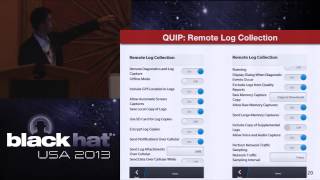
BlackBerryOS 10 from a Security Perspective
Comprehensive analysis of BlackBerryOS 10's security architecture, exploring attack surfaces, privilege escalation, remote entry points, rootkit persistence, and the effectiveness of BlackBerry Balance.
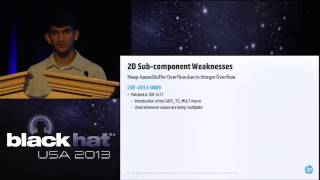
Java Every-Days - Exploiting Software Running on 3 Billion Devices
Explore Java vulnerabilities, exploitation trends, and security measures in this Black Hat talk. Gain insights into common weaknesses, attack surfaces, and Oracle's responses to protect 3 billion devices.
Introduction to Code Sanitizers
Explore code sanitizing tools for detecting memory corruptions, race conditions, and undefined behavior in programs. Learn about Valgrind, AddressSanitizer, ThreadSanitizer, and UndefinedBehaviorSanitizer.
New Shiny in the Metasploit Framework
Explore new features in Metasploit Framework, including infrastructure updates, exploitation techniques, and enhancements for various platforms and protocols.
Bypassing Control Flow Guard in Windows 10
Explore advanced Windows 10 security bypassing techniques, focusing on Control Flow Guard. Learn about memory corruption, relaxed control flow, and innovative bypass methods.
Fuzzing - Finding Your Own Bugs and Zero-Days
Master the art of fuzzer creation and vulnerability discovery, exploring buffer overflow exploitation techniques with hands-on demonstrations and practical exploit development strategies.
Using ALPC Security Features to Compromise RPC Services
Dive into Windows kernel security through ALPC and RPC services, exploring vulnerability exploitation techniques, security bypass methods, and system privilege escalation strategies.
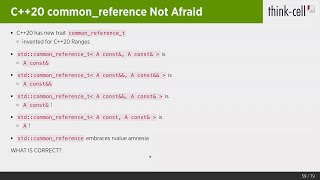
The C++ Rvalue Lifetime Disaster - Understanding and Mitigating Issues
Explore rvalue reference lifetime issues in C++, their impact on code safety, and potential solutions for improved memory management and generic programming.
Introduction to Procedural Debugging through Binary Libification
Discover techniques for transforming ELF binaries into shared libraries and analyze memory corruption vulnerabilities through procedural debugging methods and direct function calls.
Exploiting Android's Hardened Memory Allocator - Security Analysis and Exploitation Techniques
Discover techniques for exploiting Scudo, Android's memory allocator, through an analysis of security measures and demonstration of new exploitation methods for gaining arbitrary memory write access.
On the Effectiveness of Control-Flow Integrity in Practice - A Systematic Overview
Explore the real-world effectiveness of Control-Flow Integrity protection across Android and Windows systems, revealing critical gaps between research advances and actual deployment in practice.

Black Hat Europe 2024
Black Hat Europe 2024