Underground Wi-Fi Hacking for Web Pentesters
Explore underground Wi-Fi hacking techniques for web penetration testing, covering hijacking, evil twin attacks, client vulnerabilities, and man-in-the-middle exploits using tools like Pineapple and Kali Linux.
Man-in-the-Middle Attacks without Rogue AP - When WPAs Meet ICMP Redirects
Explore a novel Man-in-the-Middle attack technique combining Wi-Fi Protected Access and ICMP redirects, revealing vulnerabilities in network security without using rogue access points.
EtherOops - Exploring Practical Methods to Exploit Ethernet Packet-in-Packet Attacks
Explore practical methods to exploit Ethernet packet-in-packet attacks, bypassing firewalls and NAT solutions. Learn how attackers can establish man-in-the-middle positions to eavesdrop on corporate communications.
Zeroconf Protocols and Their Numerous Man in the Middle Attacks
Explore vulnerabilities in Zeroconf protocols, focusing on man-in-the-middle attacks. Learn about potential security risks and implications for network configurations.
Owning Bad Guys and Mafia with Javascript Botnets
Explore mitm attacks on anonymous services and learn to create JavaScript botnets for analyzing connections, uncovering activities of malicious actors behind these services.
Man in the Middle Attacks
Explore advanced techniques for intercepting and manipulating network communications, focusing on Man-in-the-Middle attacks and their implications for cybersecurity.
Stick a Pin in Certificate Pinning - How to Inspect Mobile Traffic and Stop Data Exfiltration
Learn how certificate pinning in mobile apps can bypass security controls and explore solutions for inspecting encrypted traffic to prevent data exfiltration and attacks.
Automating MiTM for Winning
Explore automated Man-in-the-Middle attack techniques for network security testing, focusing on efficient methods to intercept and analyze network traffic.
Information Gathering and Social Media Attacks to Gain Access
Explore social engineering tactics, evil twin attacks, and information gathering techniques using LinkedIn and other social media platforms for cybersecurity purposes.
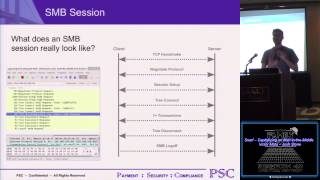
Snarf Capitalizing on Man in the Middle
Explore techniques for exploiting Man-in-the-Middle vulnerabilities, focusing on network security and potential attack vectors.
You Have Updates - A Look at an Old Tool Making a Comeback - Evilgrade
Explore Evilgrade, a resurgent tool for exploiting software update processes, and learn about its attack structure, technical factors, and potential applications.
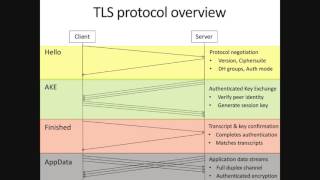
Protecting TLS from Legacy Crypto
Explore TLS vulnerabilities, attacks on legacy crypto, and downgrade protection strategies. Learn about protocol agility, SIGMA, Logjam, SLOTH, and TLS 1.3's improved security features.
Out of Band Authentication in Group Messaging - Computational, Statistical, Optimal
Explore secure group messaging protocols, focusing on out-of-band authentication methods to prevent man-in-the-middle attacks and enhance end-to-end encryption in multi-user settings.
Trusting SDKs
Explore the risks of including SDKs in applications, with real-world examples of injecting malicious code into 3rd party iOS SDKs using man-in-the-middle attacks.
Playable Ads - What REALLY Are They?
Explore the world of playable ads: their nature, functionality, potential for hijacking or bypassing, and hidden purposes. Uncover the truth through reverse engineering and man-in-the-middle techniques.
Making Hacking Childs Play
Explore common online attacks executed by kids using simple tools, and learn essential strategies to secure your applications against various threat actors.
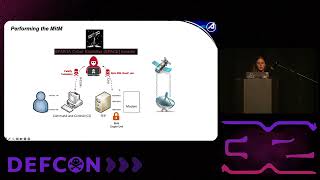
From Theory to Reality: Demonstrating SPARTA Techniques Through Ground Infrastructure Attacks
Discover how to exploit space mission vulnerabilities through ground infrastructure attacks, focusing on SPARTA techniques and man-in-the-middle exploits for spacecraft communications.
How a Combination of Bugs in KakaoTalk Compromises User Privacy
Uncover critical security vulnerabilities in KakaoTalk messaging app, from account takeover exploits to encryption weaknesses, with practical demonstrations and analysis of protocol flaws.
Breaking into Secure Facilities with OSDP - Vulnerabilities and Exploitation Techniques
Uncover critical vulnerabilities in OSDP security protocols and learn practical exploitation techniques for bypassing encrypted RFID systems through demonstrated pentesting tools and methodologies.
Automatic Exploitation of TLS Certificate Validation Vulnerabilities
Explore TLS certificate validation vulnerabilities and their automated exploitation using certmitm, featuring real-world attacks on iOS and Windows 11 systems.
Exploiting Bluetooth Vulnerabilities: From Car Systems to Bank Account Security
Discover how to identify and exploit Bluetooth vulnerabilities in modern vehicles and flight systems, using BlueToolkit framework for testing, with practical tips and new attack vectors for security research.