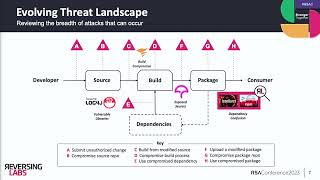
The Rise of Malware Within the Software Supply Chain
Explore malicious injections in open source software, their impact on the supply chain, and strategies to protect, detect, and respond to these evolving threats.
Multi-Step Initial Access Strategies: Desperate Infection Chains - Part 2
Explore modern infection chain techniques and multi-step strategies used by threat actors for initial access, focusing on post-MOTW era tactics and file format exploitation.
Mobile Device Security Threats: Malware Distribution and Corporate Vulnerabilities - Lecture 3
Explore mobile device security vulnerabilities and malware threats like Pegasus, understanding how personal phones can compromise corporate cybersecurity through various attack vectors and data extraction methods.
Demystifying Thread Call Stack Spoofing - Advanced Techniques for Stack Manipulation
Dive into advanced thread stack spoofing techniques, combining stack frames forging with ROP and JOP to achieve stealthy module execution and call stack manipulation.
Improving the Stealthiness of Memory Injection Techniques Using Python Ctypes
Delve into advanced memory injection techniques using Python ctypes, exploring stealthy methods like Module-Shifting for enhanced payload delivery and process manipulation.
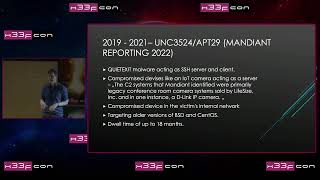
Addressing Tactics Related to Edge Device Compromise - Security Detection and Defense
Explore advanced threat hunting techniques and defense strategies against edge device compromises, focusing on detection methods, forensic analysis, and proactive security measures for network infrastructure.
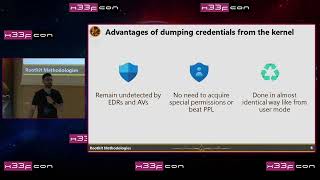
Kernel Games: The Ballad of Offense and Defense in Rootkit Methodologies
Dive into advanced kernel rootkit techniques for red team operations and defense strategies, covering stealthy persistence, EDR evasion, and practical detection methods with hands-on demos.
Modern Stuxnet-Style Attacks Using Filesystem Vulnerabilities and NTFS Exploits
Explore modern cyber attack techniques inspired by Stuxnet, focusing on filesystem vulnerabilities, NTFS exploits, and advanced persistence methods while learning effective defense strategies.
Purple Teaming: Attack Simulation and Control Validation with Atomic Red
Discover how to leverage Atomic Red Team for simulating cyber attacks, validating security controls, and improving SOC effectiveness through practical demonstrations and MITRE framework mapping.
Driving Your Own Vulnerability: How to Navigate the Road of BYOD Attacks
Explore Windows driver vulnerabilities and BYOD attack prevention through real-world case studies, understanding threat categories and security implications for effective system protection.
Social Engineering and Real-Time Malware Attack Strategies - War Stories
Explore real-world social engineering tactics in targeted malware attacks, where attackers use direct communication and psychological manipulation to achieve successful system compromises.
Malware Design: Abusing Legacy Microsoft Transports and Session Architecture
Explore advanced malware design techniques and covert communication frameworks, focusing on Windows architecture exploitation and maintaining persistent access while evading detection systems.
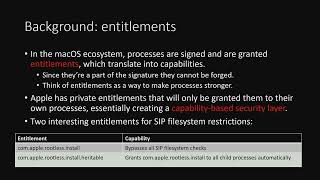
Getting a Migraine - Unique System Integrity Protection Bypass on macOS
Delve into advanced MacOS security exploitation, exploring System Integrity Protection bypass techniques, undeletable malware creation, and essential detection strategies for security teams.
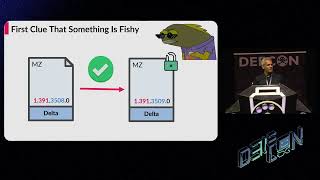
When Windows Defender Updates Become a Security Risk
Dive into Windows Defender's architecture and signature update vulnerabilities, exploring how unprivileged users can exploit security flaws to compromise Windows systems and manipulate EDR functionality.
Bootsquad: Introduction to Secure Boot Exploitation and Defense
Dive into the world of cybersecurity and virtual reality as Joe Mast presents Bootsquad, exploring innovative security concepts and challenges in the DCGVR Village at DEF CON 31.
HookChain: A New Perspective for Bypassing EDR Solutions
Discover a sophisticated EDR bypass technique combining IAT Hooking, dynamic SSN resolution, and indirect system calls to redirect Windows subsystem execution flow while remaining undetected by traditional security measures.
DriverJack: Turning NTFS and Emulated ROFs into an Infection
Discover advanced exploitation techniques targeting NTFS and emulated filesystem vulnerabilities, exploring novel attack vectors that bypass Windows security measures and maintain system persistence.
Detecting Persistent Threats on Draytek Devices - Security Assessment and Mitigation Tools
Discover how to detect and mitigate persistent threats on Draytek devices through firmware analysis, reverse engineering, and custom security module development for enhanced network protection.
DoubleDrive - Double Agents Hide Behind The Clouds
Explore cloud-based double agent techniques in IT security. Learn about innovative attack methods and defense strategies for protecting cloud environments.
Confused Learning: Supply Chain Attacks Through Machine Learning Models
Explore novel ML model vulnerabilities, including malware distribution and data exfiltration. Learn to create, distribute, and analyze ML malware, with insights on threat hunting and mitigation strategies.
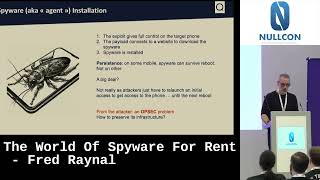
The World of Spyware for Rent - Nullcon Berlin 2024
Explore the world of commercial spyware with cybersecurity expert Fred Raynal. Gain insights into the industry, its impact, and the latest developments in this controversial field of digital surveillance.