Hyper-scale Detection and Response - Cost-Effective SIEM Alternatives
Discover cost-effective, open-source solutions for hyper-scale threat detection, processing 45TB+ logs daily. Learn to enhance security monitoring without expensive SIEM platforms.
Forwarding Snort Logs to Splunk
Learn to forward Snort logs to Splunk for powerful data analysis and monitoring. Explore Splunk's web interface to search, analyze, and visualize machine-generated data, enhancing your cybersecurity capabilities.
Installing and Configuring Wazuh for SIEM - Blue Team Operations
Learn to set up Wazuh SIEM for detecting intrusions, attacks, and malicious activity. Covers installation and agent configuration on Windows and Linux for effective security data management.
The SaaS-y Side of Incident Response - Key Log Sources for Okta, GitHub, and Salesforce
Explore key log sources for Okta, GitHub, and Salesforce in cloud-based incident response. Learn to interpret SaaS logs, avoid common pitfalls, and improve detection strategies for effective security management.
Security Onion Essentials 2024 - Detection Engineering
Explore detection engineering in Security Onion 2.4.70, covering key techniques and best practices for enhancing network security and threat detection capabilities.
Detecting Credential Abuse - Core Concepts and Challenges
Explore detection strategies for credential abuse, including core concepts, patterns, and challenges. Learn to identify suspicious activity and protect systems from unauthorized access.
LLMs at the Core - From Attention to Action in Scaling Security Teams
Explore practical tools leveraging LLMs to scale security teams, streamline workflows, and enhance decision-making in complex environments. Gain insights on automating tasks and improving security processes.
War Stories from the SOC - Cybersecurity Incident Response Lessons
Cybersecurity expert shares real-world experiences from Security Operations Center, offering insights into threat detection, incident response, and best practices for defending against cyber attacks.
Demystifying Anomaly Detection in OpenSearch - Setup and Implementation
Explore OpenSearch's anomaly detection capabilities through a hands-on walkthrough of remote logging setup, using fluent-bit and creative techniques to spark ideas for larger-scale solutions.
Being Fluentd with Logs
Explore efficient log management using Fluentd, a powerful open-source data collector. Learn techniques for streamlined log handling and analysis in modern IT environments.
Unstable Log Sequence Anomaly Detection - Introducing Vocabulary-Free BERT
Innovative anomaly detection method for unstable log data in cybersecurity, improving on BERT models to reduce false positives and enhance SOC efficiency.
Logging Modernization and Cybersecurity at Scale with MiNiFi, Kafka and Flink
Modernize logging and enhance cybersecurity using MiNiFi, Kafka, and Flink. Learn efficient log collection, processing, and streaming analytics for global network monitoring and alert generation.
Mastering AI Issue Debugging - A Data Scientist's Guide
Discover efficient AI debugging techniques through a unified system that streamlines troubleshooting processes, reduces resolution time, and improves product quality for data science teams.
Looks Good to Me (LGTM) with Tremor
Explore /lgtm with Tremor: Learn to efficiently review and approve code changes using this powerful tool for streamlined collaboration and enhanced productivity.
Observing Failure in Reactive Systems
Explore key metrics, isolation issues, and failure patterns in distributed reactive systems. Learn to identify and visualize critical data for effective production environment management.
Ask Your Logs: Structured Logging for Rails Applications
Explore structured logging in Rails to transform logs into queryable data, enabling efficient debugging and insightful analysis of production issues.
Ceph Troubleshooting in a Containerized Environment
Master essential techniques for troubleshooting Ceph in containerized environments, from diagnosing issues and analyzing logs to resolving daemon problems and memory leaks.
Solving a Real-World SRE Issue with Eclipse Trace Compass
Discover how to effectively analyze and resolve site reliability issues using Eclipse Trace Compass through a real-world case study of system slowdown affecting thousands of developers.
Revolutionizing Monitoring and Logging Systems
Explore innovative approaches to enhance monitoring and logging systems for improved site reliability engineering practices.

Linux Monitoring and Logging - HackerSploit Linux Security
Explore essential Linux monitoring and logging tools for enhanced system visibility. Learn to read auth logs, track logins, monitor resources, and use commands like last, who, htop, and glances.
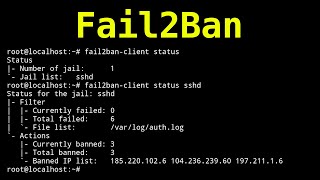
SSH Brute Force Protection with Fail2Ban
Learn to set up SSH brute-force protection using Fail2Ban on Linux. Discover how to scan log files, ban malicious IPs, and update firewall rules to enhance your system's security against unauthorized access attempts.