Updating Linux with TUX: Trust Update for Linux Kernel
Explore TUX, a system for maintaining Linux kernel integrity during updates. Learn about secure boot, TPM, and remote attestation to enhance platform trust and mitigate security threats.
Protecting Your System from Security Threats - Linux Security Mechanisms
Comprehensive overview of Linux security mechanisms for embedded systems, covering encryption, secure boot, and integrity measures to protect against various attacks.
Improving Containers Isolation in Kubernetes
Explore Kubernetes Security Profiles Operator for enhanced container isolation, focusing on SELinux, seccomp, and AppArmor. Learn how eBPF simplifies custom profile creation and gain insights from Adobe's implementation.
Mitigating Hackers with Hardening on Linux - An Overview for Developers with Focus on Buffer Overflow
Learn Linux security techniques to protect against hackers, focusing on buffer overflow vulnerabilities and hardening methods for embedded systems and IoT devices using C programming.
TPM Software Stack - Enabling the TPM2.0 Ecosystem in Linux
Explore TPM2.0 ecosystem in Linux: architecture, APIs, implementation, and use cases. Learn about recent developments, tools, and integrations with OpenSSL and PKCS11.
Security Module Stacks That Don't Fall Over
Explore security module stacking pitfalls, configuration conflicts, and best practices for new modules, with emphasis on networking challenges and infrastructure usage.

SELinux Overview and Recent Developments
Annual update on SELinux developments, covering past achievements, current work, and future plans. Insights from maintainer Paul Moore on kernel, userspace, and policy changes.
Overview and Recent Developments in Smack Linux Security Module
Explore Smack Linux Security Module's current state, recent developments, and practical applications in this comprehensive overview by Intel expert Casey Schaufler.
AppArmor Overview and Recent Developments
Explore AppArmor security project's model, recent developments, and challenges with Canonical's John Johansen. Learn about its use, direction, and open issues in Linux security.

Tying EVM into LSM Policy for Enhanced Linux Security
Explore securing developer machines using Linux's Extended Verification Module, integrating it with security mechanisms for enhanced application privilege management based on metadata integrity.
Linux Encryption Performance Improvements and Best Practices
Explore recent Linux cryptographic stack improvements, covering TLS, dm-crypt, and hardware acceleration. Learn how enhanced encryption performance can bolster data protection across various architectures.
Protect Containerized Applications with System Call Profiling
Explore system call profiling for containerized application security. Learn to develop accurate profiles, monitor runtime behavior, and detect anomalies with low performance overhead and false positives.
Device Mapper Target Measurements for Remote Attestation Using IMA
Explore remote attestation using IMA, focusing on Device Mapper Target Measurements. Learn about module attributes, see a demo, and discover future ideas in this technical presentation.
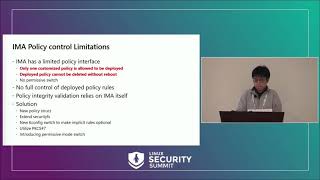
The Future of Code Integrity Enforcement - Extending IMA
Explore advancements in code integrity enforcement, focusing on extending IMA capabilities and addressing limitations in policy control and appraisal mechanisms.
Deep Dive into Landlock Internals
Explore Landlock's security sandboxing features, internals, and roadmap. Learn about access control, ruleset creation, and policy composition for enhanced system protection.
Sandboxing Applications with Landlock
Learn about Landlock, a Linux security feature for sandboxing applications. Explore its use cases, implementation, and benefits for developers and system administrators.
Fileless Malware Infection and Linux Process Injection in Linux OS
Explore fileless malware and process injection techniques in Linux systems, enhancing your understanding of advanced cybersecurity threats and defense strategies.
What Have Syscalls Done for You Lately? - Exploring Container Security
Explore syscalls, their role in container setup, and how to enhance deployment security by limiting syscall usage. Learn about seccomp, AppArmor, and microservices security advantages.
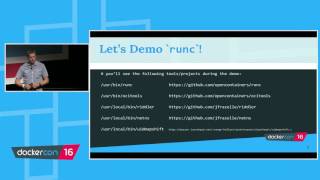
runC: The Little Engine That Could Run Docker Containers - Black Belt Track
Explore runC, a lightweight Docker container runtime. Learn to convert configurations, experiment with security features, and understand OCI tools for efficient container management.
Linux System Security Tutorial
Comprehensive exploration of Linux system security principles and best practices, emphasizing practical strategies for robust protection in enterprise environments.
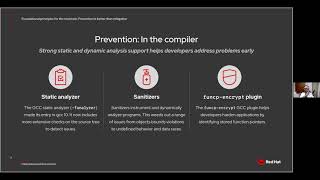
Securing GCC and GLIBC
Explore strategies for enhancing security in GCC and GLIBC, crucial components of Linux systems, with insights from a Red Hat expert.