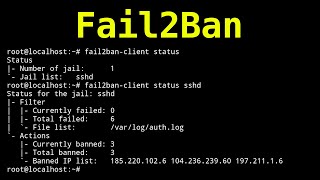
SSH Brute Force Protection with Fail2Ban
Learn to set up SSH brute-force protection using Fail2Ban on Linux. Discover how to scan log files, ban malicious IPs, and update firewall rules to enhance your system's security against unauthorized access attempts.
Introduction to the Kubernetes Seccomp Operator
Explore Kubernetes Seccomp Operator: enhance security, manage profiles, and implement secure computing mode for improved container isolation and system call control.

Linux Security - UFW Complete Guide - Uncomplicated Firewall
Comprehensive guide on setting up and configuring UFW (Uncomplicated Firewall) for Linux server security, covering installation, rule management, and best practices.
DockerSlim and Kyverno - Enhancing Kubernetes Workload Security
Explore how DockerSlim and Kyverno enhance Kubernetes workload security through container image minification, automated AppArmor and SecComp profiles, and simplified cluster security management.
Least Privilege Containers: Keeping a Bad Day from Getting Worse
Explore strategies for reducing container privileges, enhancing security through unprivileged users and minimal images, and implementing design changes to segment permissions and prevent future vulnerabilities.
Securing the Superpowers: Who Loaded That eBPF Program?
Explore eBPF technology's power and security implications. Learn about auditing, monitoring, and enforcing eBPF program loading on Linux systems using Tetragon for enhanced system protection and accountability.
Controlling Script Execution in Linux - Security Mechanisms and Challenges
Explore kernel-managed script execution control in Linux, addressing challenges and implementation approaches for a consistent global policy.
Verifiable End-to-End Secure OCI Native Machines
Explore a secure toolchain for verifiable workloads using signed OCI images, ensuring tamper-proof boot processes and authenticated communication with hosts.
Enforcing Runtime Integrity with Maat
Explore Maat: an open-source framework for runtime integrity measurement in Linux systems, enabling continuous security checks and malware detection throughout system execution.
SecurityPerf - A New Open-Source Framework for Benchmarking Linux Security Solutions Performance
Explore SecurityPerf, an open-source framework for benchmarking Linux security solutions' performance impact. Learn about its containerized approach, supported services, and real-world applications.
Hypervisor-Enforced Kernel Integrity for Linux with KVM
Explore hypervisor-enforced kernel integrity for Linux using KVM. Learn about advanced protection mechanisms against kernel vulnerabilities and their implementation through virtualization.
Building the Largest Working Set of AppArmor Profiles
Discover how to build an extensive set of AppArmor profiles for enhanced Linux security. Learn about challenges, security architecture, and integration testing in this comprehensive project.
Hardening Linux for Confidential Cloud Computing - Deep Dive and Results
Explore techniques for hardening Linux guest systems in confidential cloud computing environments, focusing on security mechanisms, kernel subsystem treatments, and results from fuzzing and code audits.
BPF LSM - Updates and Future Developments
Explore BPF LSM's latest updates, real-world applications, and future developments. Learn about new features, case studies, and challenges in building advanced security policies.
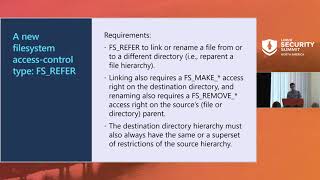
Landlock Update: File Reparenting and Network Rules Support
Explore Landlock's latest updates: file reparenting improvements and new network access controls for enhanced app and container security in Linux systems.
PowerVM Platform Keystore - Securing Linux Credentials Locally
Explore PowerVM's Platform Keystore for secure Linux credential storage, focusing on boot-time security, kernel interfaces, and challenges in developing unified interfaces for diverse platforms.
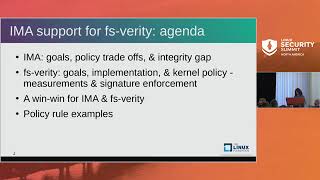
IMA Policy Support for fs-verity - A Win-win for Linux Integrity and File System Verification
Explores Linux Integrity subsystem's new fs-verity support, enhancing file integrity detection and verification. Discusses system-wide policy benefits and closing existing integrity gaps.
Program Signing and BPF Policy
Explore program signing and BPF policy implementation with expert insights on enhancing system security and performance optimization.
Smack Reference Policy: Creating a Rule Set for Linux Distributions
Explore Smack Linux security module, its unique features, and a new effort to create a reference rule set for major Linux distributions. Learn about threat protection and implementation challenges.
Lessons Learned Applying Compile-time Hardening Options for Security-Critical Programs in Linux
Explore compile-time hardening techniques for Linux security, including SafeStack and CFI. Learn practical lessons from rebuilding critical system components with enhanced protection.
BPF Signing Using FSVerity and LSM Gatekeeper
Explore BPF signing techniques using fsverity and LSM gatekeeper to enhance system security and integrity verification in Linux environments.